Topics (349k) Articles (361k) Users (406) Discussions (237) Comments (383) Files (12k) New article

Proof of Stake (PoS) is a consensus mechanism used by blockchain networks to validate transactions and add new blocks to the blockchain. Unlike Proof of Work (PoW), which requires miners to solve complex mathematical problems to validate transactions, PoS selects validators based on the number of coins they hold and are willing to "stake" as collateral.
Proof of Space (PoS) is a consensus mechanism used primarily in blockchain networks to validate transactions and secure the network by utilizing the storage capacity of participants' devices, rather than relying on computational power like in Proof of Work (PoW) systems. The concept allows users to allocate a certain amount of disk space to participate in the network, and their chances of being chosen to create the next block (or verify transactions) are proportional to the amount of space they have contributed.
Proof of personhood is a concept related to verifying the identity of an individual in various contexts, particularly in the realms of technology and online interactions. It aims to establish that a user is a human being rather than a bot or automated system, thereby ensuring authenticity in digital transactions, voting, and other online activities where human identity is critical. The idea is significant in the context of blockchain and decentralized systems, where traditional forms of identity verification might be less suitable.
Proof of knowledge is a concept in cryptography and computer science that pertains to demonstrating that a party (the prover) possesses certain information (usually a secret or private key) without revealing the information itself. It is often associated with zero-knowledge proofs, which are protocols that allow one party to prove to another that they know a value (like a password or cryptographic key) without disclosing the value itself.
Proof of identity in the context of blockchain consensus refers to a mechanism or method used to establish and verify the identity of participants within a blockchain network. This is particularly important in permissioned blockchains or systems where user identity and verification are critical for ensuring trust, security, and compliance within the network. ### Key Aspects of Proof of Identity: 1. **Identity Verification**: Participants must verify their identities to gain access to the blockchain.
A **Probabilistic Signature Scheme (PSS)** is a type of digital signature scheme that incorporates randomness into its signing process to provide enhanced security against specific types of attacks. The primary purpose of using randomness is to ensure that even if the same message is signed multiple times, it will yield different signatures each time, thus preventing attackers from being able to derive useful information from multiple signatures of the same message.
Privilege Management Infrastructure (PMI) refers to a set of technologies and solutions designed to manage and control elevated user privileges in IT environments. PMI is crucial for maintaining security and compliance in organizations by ensuring that users have only the access necessary to perform their job functions and that elevated privileges are granted in a controlled, auditable manner.
Private Set Intersection (PSI) is a cryptographic protocol that allows two or more parties to compute the intersection of their datasets without revealing any additional information about their respective datasets. This means that while the parties can determine which elements are common to both sets, they do not have access to any other data outside of the intersecting elements. ### Key Concepts: 1. **Privacy**: The main goal of PSI is to ensure the privacy of the datasets involved.
PrivateCore is a cybersecurity company that focuses on securing server infrastructure, particularly in cloud environments. Founded in 2012, the company is known for its development of software solutions that help protect against various types of attacks, especially those targeting system memory and virtualization layers. One of the key products developed by PrivateCore is vCage, which is designed to create a secure and isolated environment for running sensitive workloads.
Prince is a lightweight block cipher that was designed for high performance in constrained environments, such as IoT devices and smart cards. It was introduced in 2012 by its creators, who wanted to provide a secure and efficient encryption solution. The cipher uses a structure known as a "substitution-permutation network" and operates on blocks of data.
Polygraphic substitution refers to a type of substitution cipher where groups of letters (or digraphs, trigraphs, etc.) are replaced with other groups of letters. In contrast to simple monoalphabetic ciphers, where each letter is substituted consistently for another single letter, polygraphic substitution takes into account multiple characters at once, which enhances the complexity of the encryption.
Point-to-point encryption (P2PE) is a specific method of data encryption that protects sensitive information, such as payment card data, as it travels between a device, such as a point-of-sale (POS) terminal, and a secure decryption endpoint. The goal of P2PE is to ensure that the data remains encrypted throughout its entire journey, reducing the risk of exposure to data breaches or unauthorized access.
Plaintext refers to data that is in a readable and understandable format without any encryption or encoding applied to it. It is the original unaltered version of information, allowing it to be readily understood by humans or processed by machines. For example, a simple text document or an unencoded message is considered plaintext.
"Pizzino" can refer to different things based on the context. Here are a few possibilities: 1. **Food**: In some regions, "pizzino" may refer to a small pizza or a type of pizza slice, often made as a snack or for individual consumption. It could also describe a specific style or preparation of pizza. 2. **Cultural Reference**: It might refer to a dish or product in a particular culture or cuisine, especially in Italian or Mediterranean contexts.
PhotoDNA is a technology developed by Microsoft in collaboration with the National Center for Missing and Exploited Children (NCMEC) designed to help combat the distribution of child exploitation images online. It uses a hashing technique to create a unique digital signature or "hash" for images, which allows for the identification and tracking of specific content without needing to directly view the images themselves.
Philco, originally known as the Philadelphia Storage Battery Company, was an American company founded in the 1890s. Initially focused on battery production, the company diversified into various electronics and consumer products, including radios and televisions. In the mid-20th century, Philco became known for its innovations in electronics, and it expanded into the computer market.
Pepper is a security mechanism used in cryptography, particularly in the context of password hashing. It involves adding a secret value to a password before hashing it. The goal of using pepper is to enhance the security of stored passwords by providing an additional layer of protection against various attacks, such as rainbow table attacks and brute-force attacks.
Password strength refers to how difficult it is for an unauthorized party to guess or crack a password. A strong password is essential for protecting personal and sensitive information from cyber threats, such as hacking and unauthorized access. Several factors contribute to password strength, including: 1. **Length**: Longer passwords are generally stronger. A good rule of thumb is to use at least 12 to 16 characters.
Password-based cryptography refers to cryptographic techniques that utilize passwords for the purpose of securing data, authenticating users, or generating cryptographic keys. This method relies on the assumption that the password, which is typically a string of characters created by the user, is known only to that user and serves as a means of encryption or decryption. Here are some key aspects of password-based cryptography: 1. **Key Derivation**: In many systems, passwords are not used directly as encryption keys.
Password-authenticated key agreement (PAKE) is a cryptographic protocol that allows two parties to establish a shared secret key based on a password, without transmitting the password itself over the network. This method ensures that even if an eavesdropper is listening to the communication, they cannot derive the password or the shared key from the exchanged messages.
Pinned article: Introduction to the OurBigBook Project
Welcome to the OurBigBook Project! Our goal is to create the perfect publishing platform for STEM subjects, and get university-level students to write the best free STEM tutorials ever.
Everyone is welcome to create an account and play with the site: ourbigbook.com/go/register. We belive that students themselves can write amazing tutorials, but teachers are welcome too. You can write about anything you want, it doesn't have to be STEM or even educational. Silly test content is very welcome and you won't be penalized in any way. Just keep it legal!
Intro to OurBigBook
. Source. We have two killer features:
- topics: topics group articles by different users with the same title, e.g. here is the topic for the "Fundamental Theorem of Calculus" ourbigbook.com/go/topic/fundamental-theorem-of-calculusArticles of different users are sorted by upvote within each article page. This feature is a bit like:
- a Wikipedia where each user can have their own version of each article
- a Q&A website like Stack Overflow, where multiple people can give their views on a given topic, and the best ones are sorted by upvote. Except you don't need to wait for someone to ask first, and any topic goes, no matter how narrow or broad
This feature makes it possible for readers to find better explanations of any topic created by other writers. And it allows writers to create an explanation in a place that readers might actually find it.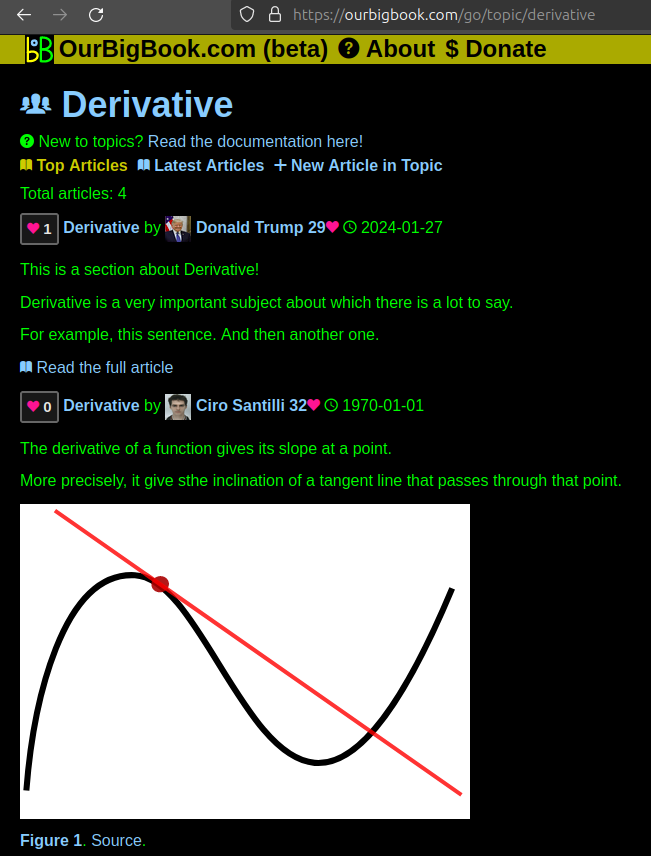
Figure 1. Screenshot of the "Derivative" topic page. View it live at: ourbigbook.com/go/topic/derivativeVideo 2. OurBigBook Web topics demo. Source. - local editing: you can store all your personal knowledge base content locally in a plaintext markup format that can be edited locally and published either:This way you can be sure that even if OurBigBook.com were to go down one day (which we have no plans to do as it is quite cheap to host!), your content will still be perfectly readable as a static site.
- to OurBigBook.com to get awesome multi-user features like topics and likes
- as HTML files to a static website, which you can host yourself for free on many external providers like GitHub Pages, and remain in full control
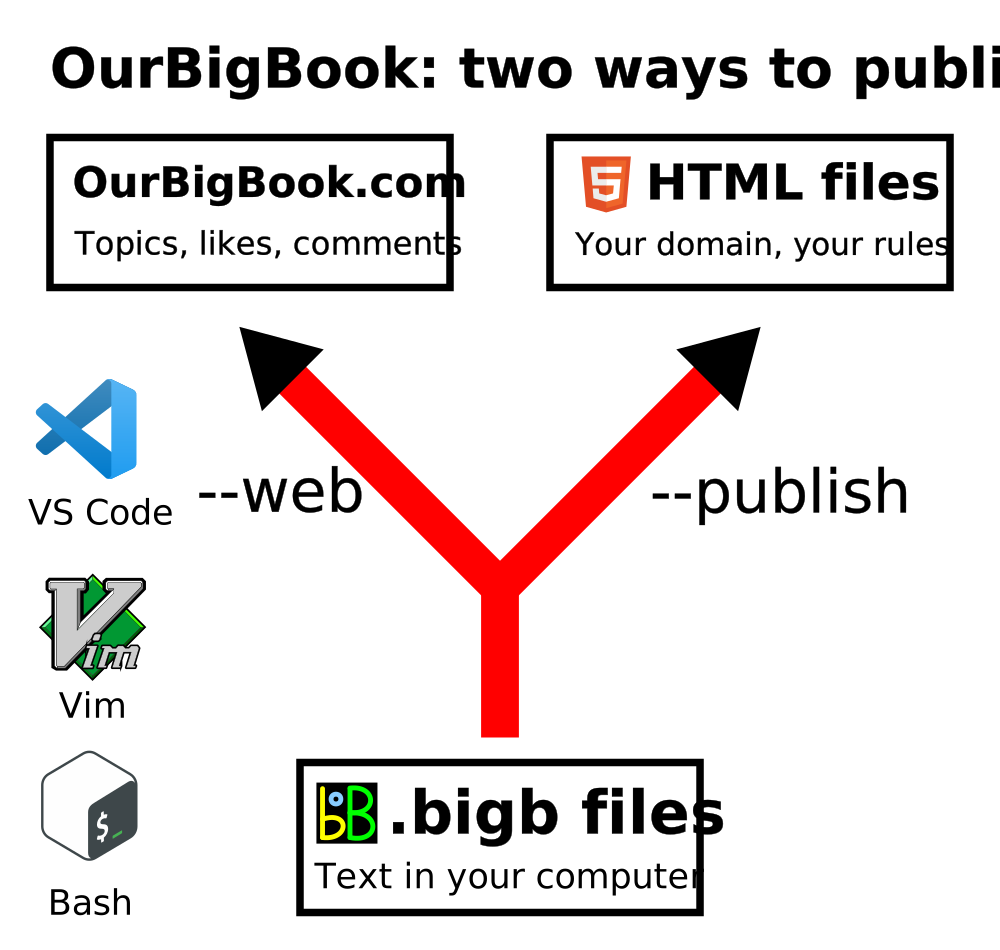
Figure 2. You can publish local OurBigBook lightweight markup files to either OurBigBook.com or as a static website.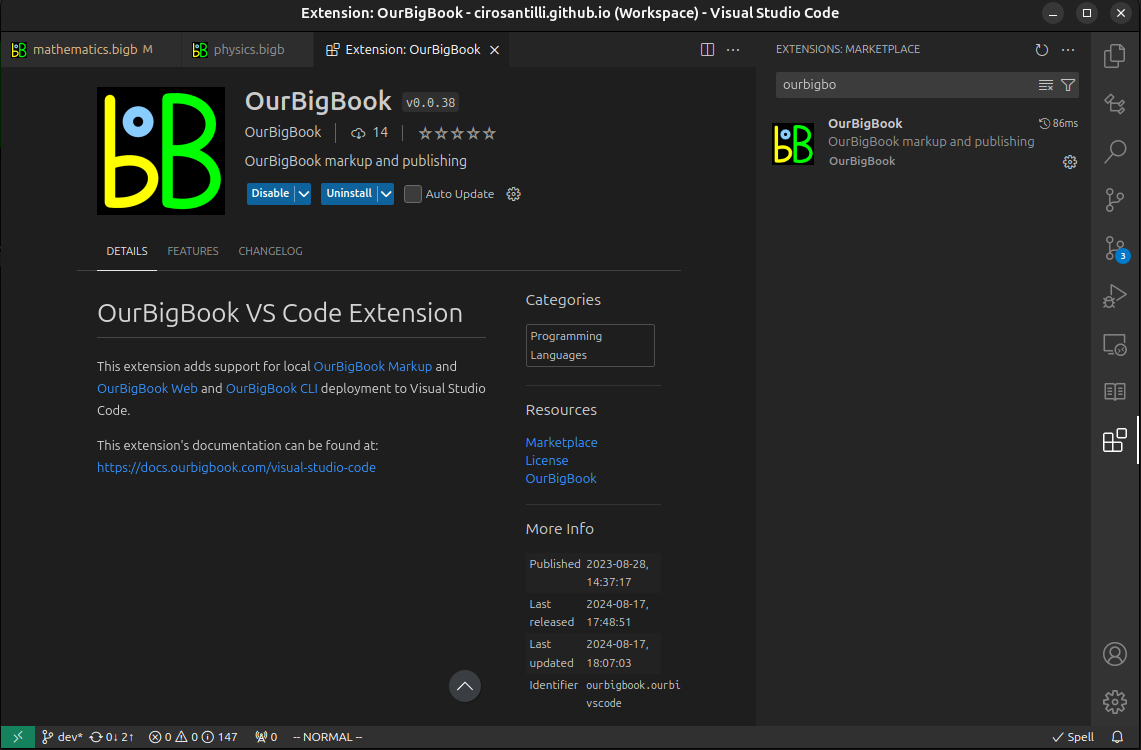
Figure 3. Visual Studio Code extension installation.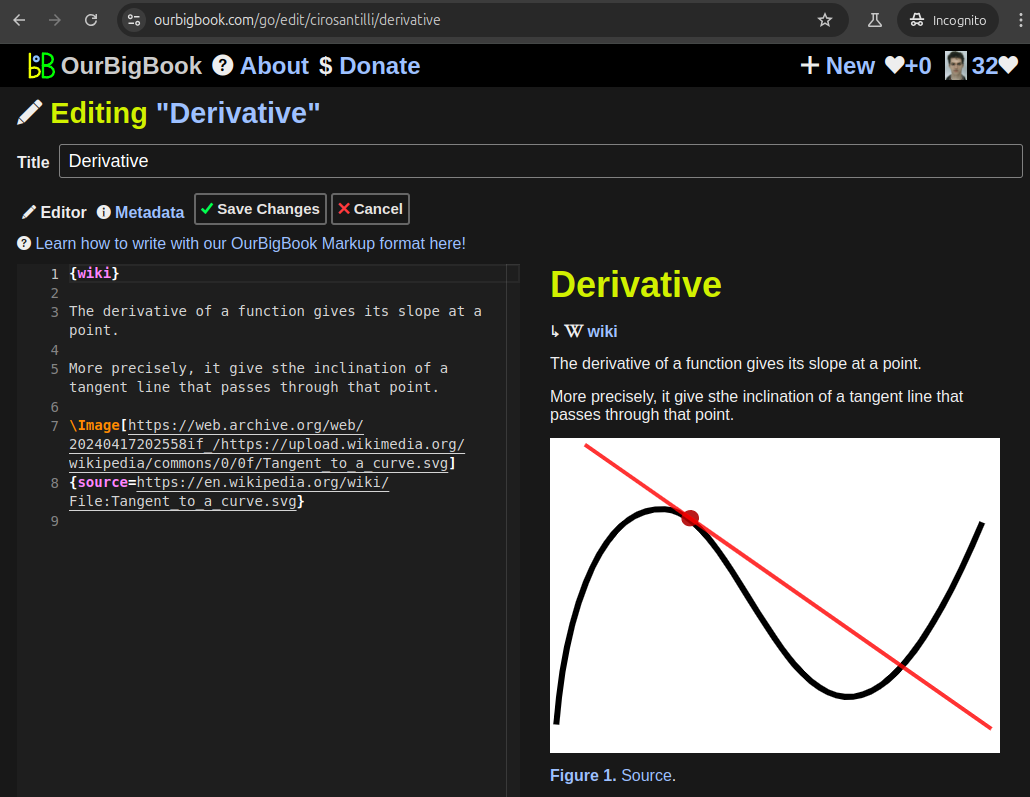
Figure 5. . You can also edit articles on the Web editor without installing anything locally. Video 3. Edit locally and publish demo. Source. This shows editing OurBigBook Markup and publishing it using the Visual Studio Code extension. 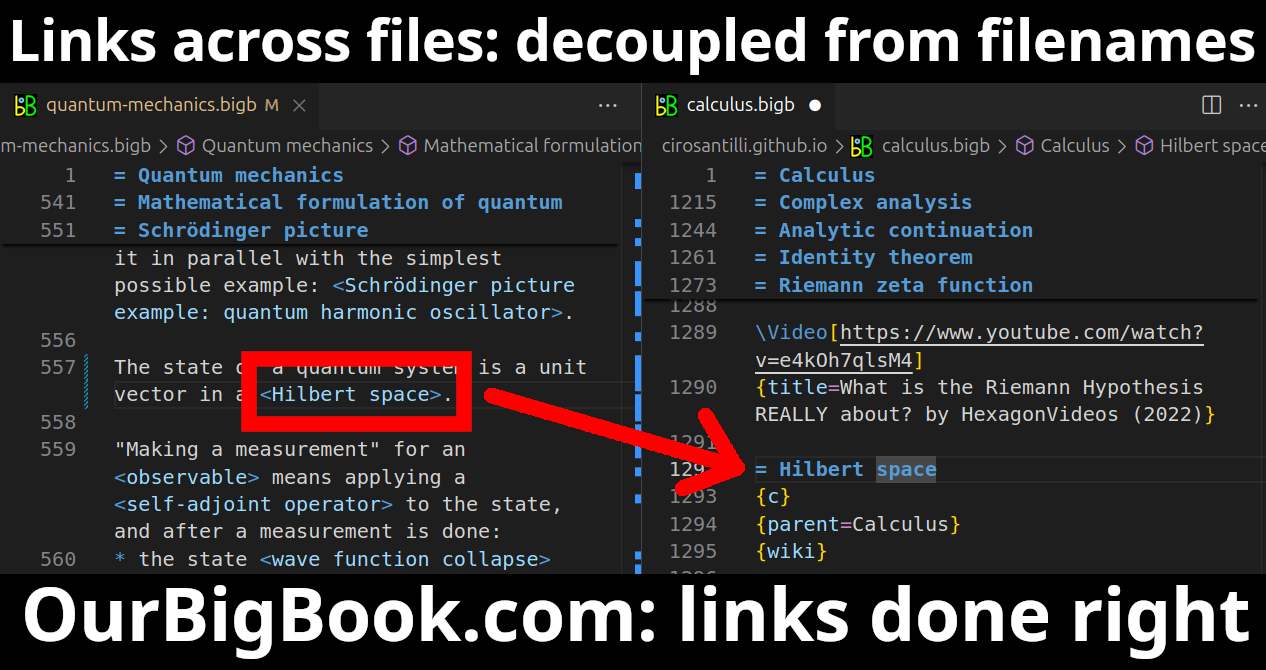
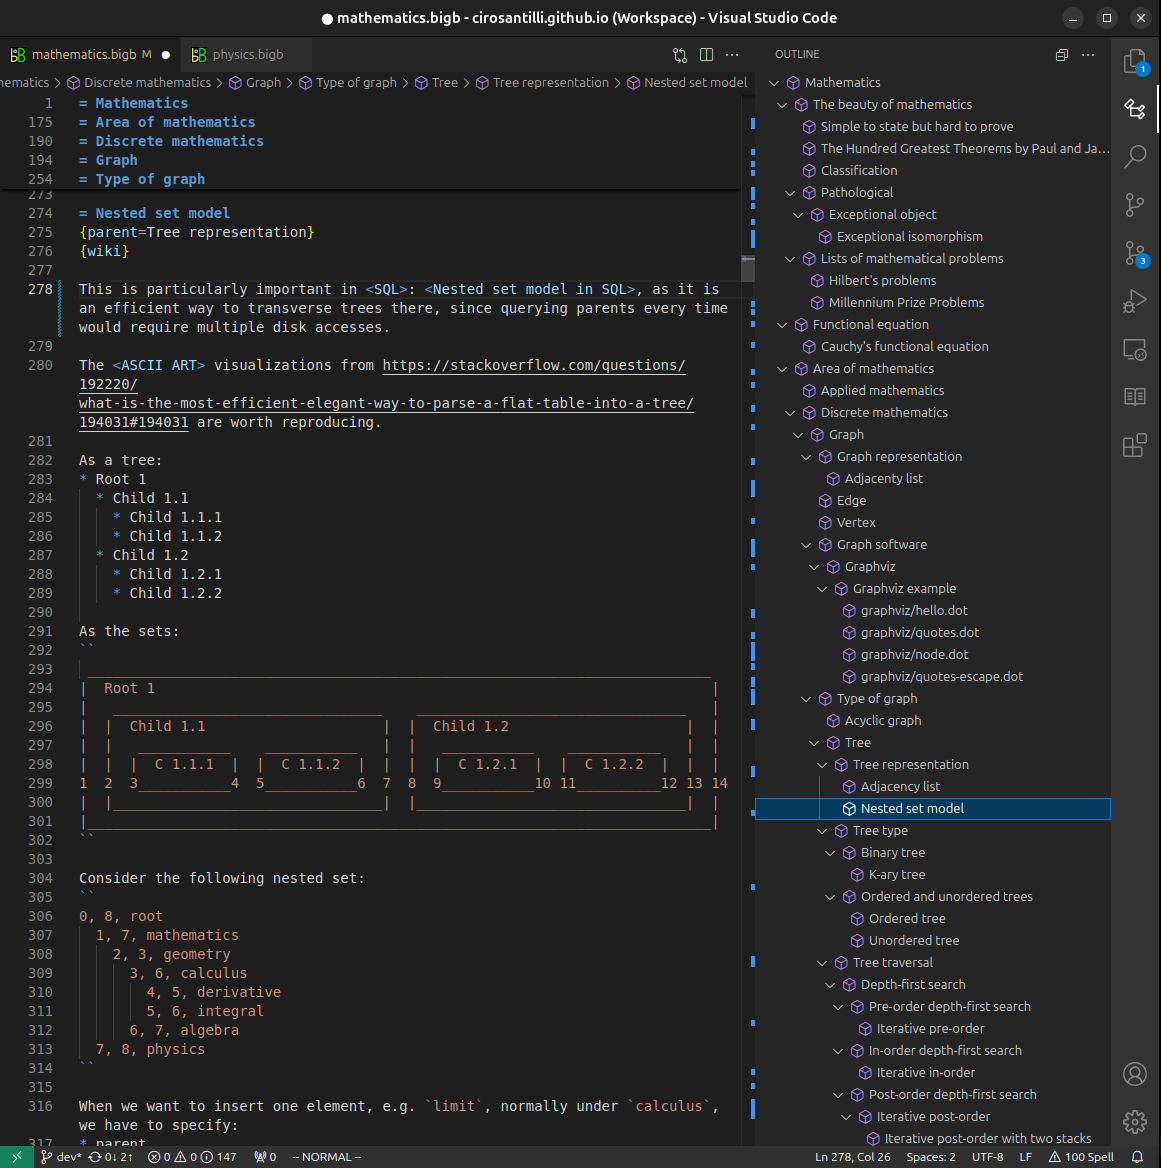
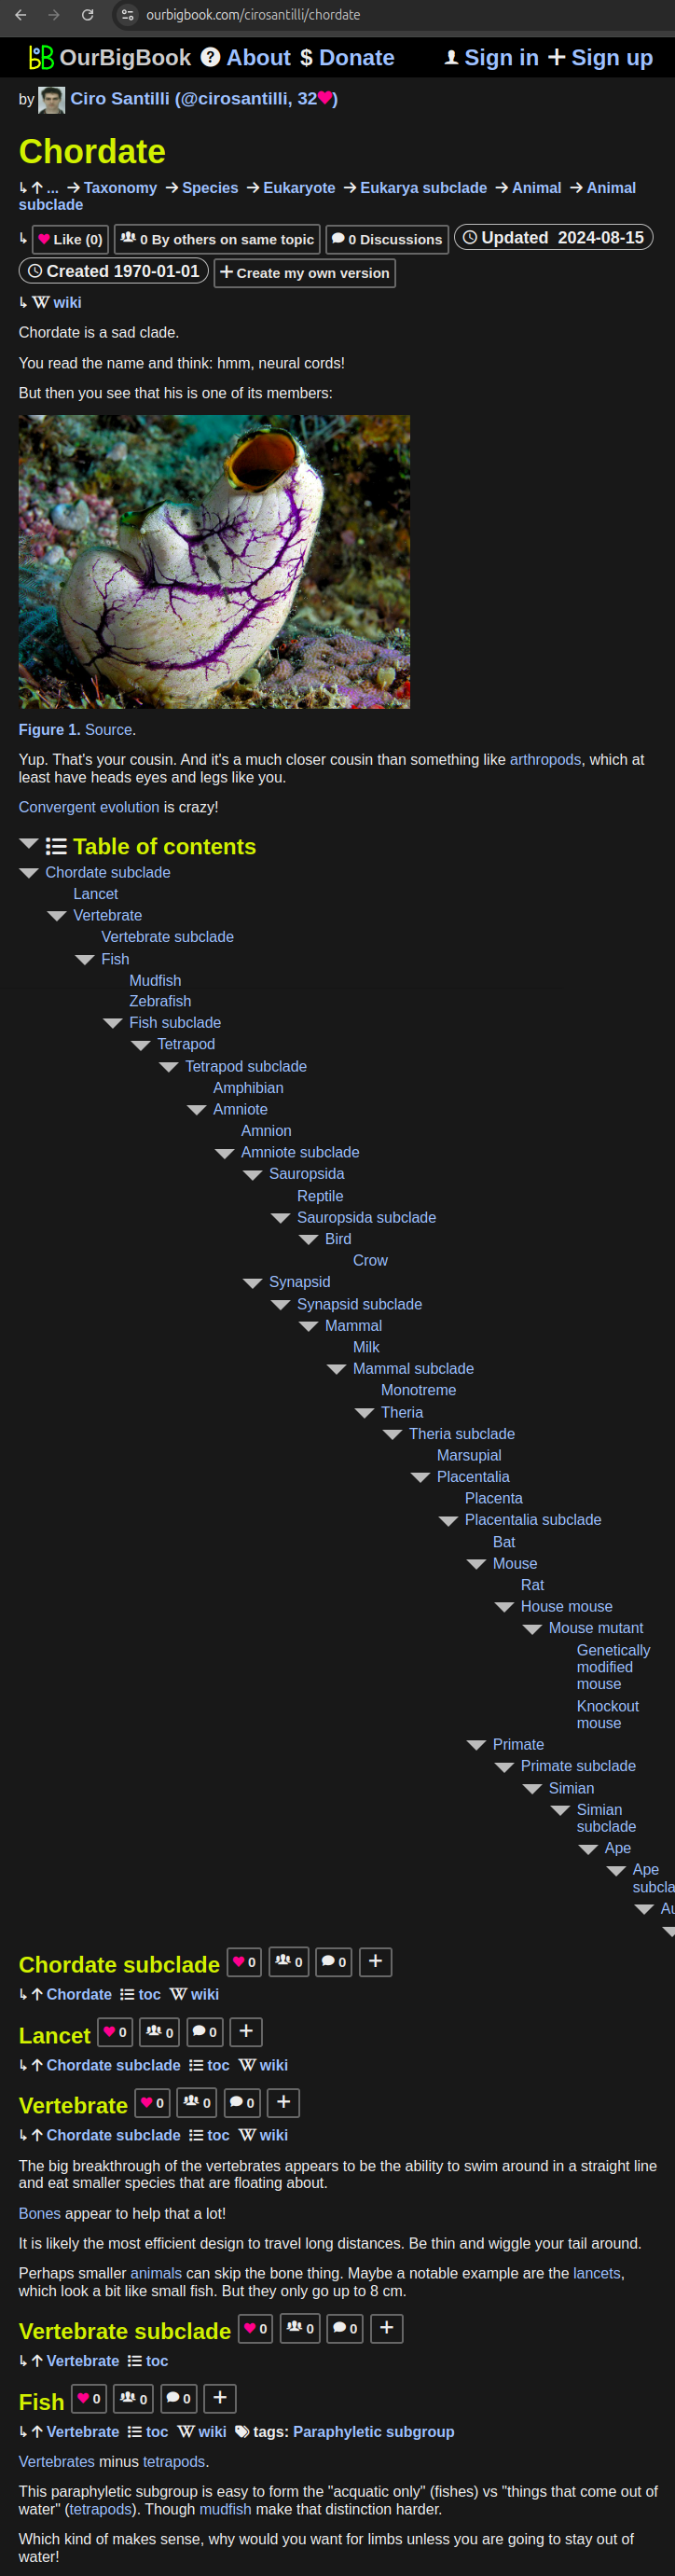
- Infinitely deep tables of contents:
All our software is open source and hosted at: github.com/ourbigbook/ourbigbook
Further documentation can be found at: docs.ourbigbook.com
Feel free to reach our to us for any help or suggestions: docs.ourbigbook.com/#contact