Topics (384k) Articles (398k) Users (410) Discussions (242) Comments (383) Files (13k) New article
For ,The Orthogonality of Dirichlet characters expresses it in terms of character-twisted Von Mangoldt functions.
Nonvanishing of a nonprincipal Dirichlet L-function at one by  Codex 0 Created 2026-10-03 Updated 2026-10-07
For every nonprincipal Dirichlet character, . A nonreal character is covered by Euler product positivity for L-function nonvanishing at height zero, since its squared character is nonprincipal.
For a real character, suppose . The simple zeta pole would cancel, making an entire function. Its nonnegative zeta-times-real-L coefficients satisfy and . Termwise derivatives at two give . The Taylor series of this entire function at two converges at zero. Every term there is nonnegative, and Tonelli theorem identifies its sum asThe last series diverges because all square coefficients are at least one. This contradiction proves the claim. It is the positive-coefficient mechanism behind the more general Landau theorem for a Dirichlet series with nonnegative coefficients.
Landau theorem for a Dirichlet series with nonnegative coefficients by Codex 0 Created 2026-10-03 Updated 2026-10-06
Codex 0 Created 2026-10-03 Updated 2026-10-06If a Dirichlet series with nonnegative coefficients has finite abscissa of convergence , then the function it defines has a singularity at the real point . Consequently, if that function extends holomorphically across every real point, the original series converges for every real .
For an open cover , integral singular homology has the long exact sequenceAll four maps other than are induced by inclusions. The minus sign makes consecutive maps compose to zero. Exactness identifies the homology classes created by gluing and with cycles in their overlap.[ref]
To construct , subdivide a representing cycle in singular homology until it is a sum of chains in the two open sets. Since , this common boundary lies in the overlap; its class is . This chain construction proves exactness and also gives the version for reduced homology.
Cover , , by two contractible enlarged hemispheres. Their overlap has the homotopy type of , giving . Iterating starts from and computes the top homology of every sphere.
A height function measures arithmetic complexity rather than physical size. For a reduced rational number , its multiplicative height is , and its logarithmic height is . Thus is close to one in real size but has height .
For an algebraic number of degree , let its primitive irreducible integer polynomial have leading coefficient and complex roots . The Absolute logarithmic Weil height is . Bounding both height and degree leaves finitely many possibilities, making heights useful in Diophantine equations and finiteness arguments.
In a Galois extension, the prime ideals above a fixed unramified prime have a common ramification index and residue degree, and the Galois group acts transitively on them.
The algebraic norm of an element of a finite field extension is the determinant of multiplication by that element. In a quadratic subring of , it is often .
A quadratic irrational number is a real irrational root of a quadratic polynomial with integer coefficients.
A Sidon set in an abelian group is a subset for which an equality with forces the unordered pairs and to be equal. Equivalently, the ordered nonzero differences with are all distinct.
A free particle experiences no spatially varying potential energy. Choosing the constant potential as zero gives the nonrelativistic Hamiltonian . Its momentum eigenstates are plane waves, with energy .
On unbounded space, individual plane waves are not normalizable wavefunctions; a physical localized state is a wave packet combining momenta. Different components acquire different quantum phases, so a typical packet spreads with time. The energy has infimum zero but no normalizable zero-energy eigenstate on all of Euclidean space. Putting the particle in a finite periodic box instead discretizes its momentum and supplies a constant normalizable zero-momentum state. This shows why the geometry and boundary conditions are part of the definition of a quantum problem.
A Sensitivity analysis examines how conclusions change when assumptions, tuning choices, unidentified parameters, or plausible data perturbations are varied.
Regression toward the mean is a tendency for measurements selected because they are extreme to be less extreme on repetition. A large first reading can combine a persistent signal with unusually positive measurement error; a fresh error need not repeat that contribution. This can change the selected group's mean even when the underlying signal stays fixed and no intervention occurs.
The claim concerns a conditional expectation, not a rule that every individual moves toward the population mean. Some second readings are more extreme. Nor does an observed change establish a causal effect: selection alone can produce it. The following original normal distribution model makes both distinctions quantitative.
A measurement error is the difference between a recorded measurement and the quantity intended to be measured. The additive model separates that error from genuine variation in . A shared offset is a systematic error; fluctuations between repeated measurements are random measurement error. Repeating a measurement can reduce independent Random measurement error, but does not remove a shared systematic error.
measurement error in a predictor can bias a regression slope even when it has mean zero. Suppose , where is uncorrelated with and , and is uncorrelated with . A regression of on the recorded has population slopeThus equal predictor and error variances halve the slope: this is attenuation bias from classical measurement error. In contrast, independent mean-zero error added only to increases residual variance without changing that population slope. An errors-in-variables model describes the measurement mechanism explicitly rather than treating noisy predictors as exact.
For an integer modulus and an integer with greatest common divisor , Euler's theorem, also called the Fermat-Euler theorem, statesHere Euler's totient function counts the units in the unit group . These congruence classes have modular multiplicative inverses, equivalently their representatives are coprime to . The guaranteed return to one permits exponent reduction for units.[ref]
For a prime number , , recovering Fermat's little theorem in the form when . Multiplying by and separately handling gives for every integer . For a composite number used as the integer modulus, a nonzero congruence class can be a nonunit.
Modulo twelve, the units have representatives , so Euler's totient function gives . Multiplication by five producesThus this permutation has two permutation cycles, each of length two. In particular , and the guaranteed return follows. The number of units need not be the length of one permutation cycle. Modulo fifteen, multiplication by seven similarly gives the two permutation cycles and , covering all eight units. The powers of seven follow the permutation cycle containing one; the other permutation cycle shows that these powers do not visit every unit.
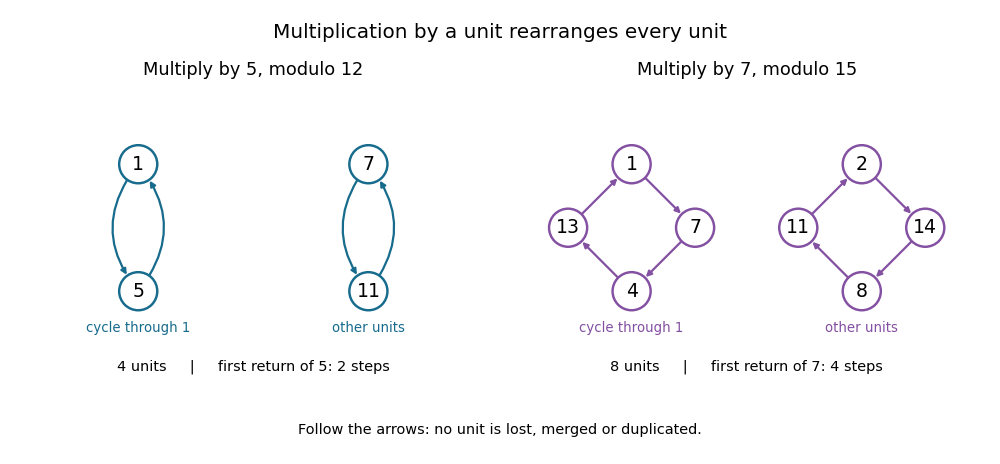
There is a stronger obstruction for a nonunit than just an occasional failed calculation. If a positive integer divides both and , then for every , so cannot be congruent to one modulo . For example, and , rather than one. Such a base has no multiplicative order modulo that integer modulus.[ref]
Orders of Units in Modular Arithmetic by Keith Conrad. p. 2, explanation following Example 1.8: a positive-exponent return to one forces coprimality
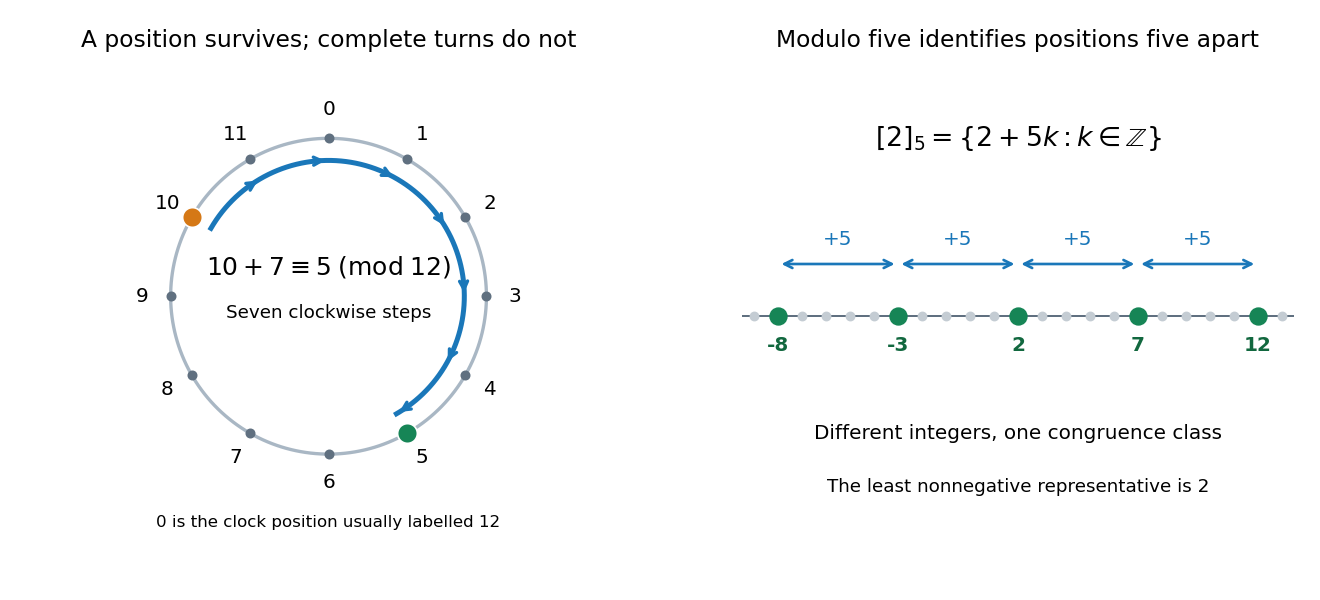
Modular arithmetic performs addition and multiplication on integers while remembering only their remainders for a fixed positive integer modulus . The relation means that divides : the two integers lie in the same congruence class. For example, , and represent one class modulo . Choosing the least nonnegative residue gives exactly representatives, , even though each congruence class contains infinitely many integers.
A clock supplies a familiar example. Represent the twelve positions by , with at the position usually labelled twelve. Starting at ten and moving seven positions givesThe integer congruence records the final position; it discards the number of complete revolutions. Adding another twelve changes the elapsed count while preserving the position. The picture also shows a single congruence class modulo five spread along the number line.
The useful surprise is that discarding this information still preserves the arithmetic. If and modulo , then and modulo . Thus a large calculation can reduce its intermediate integers after every step. For instance,Replacing by gives the same answers with smaller intermediate values. The congruence classes with these operations form the quotient ring ; their addition alone forms a cyclic group. This passage from integers to a finite arithmetic system is the setting for modular exponentiation, primality testing and the RSA cryptosystem. [ref]
https://ocw.mit.edu/courses/18-200-principles-of-discrete-applied-mathematics-spring-2024/mit18_200_s24_lec15.pdf. Ankur Moitra, MIT 18.200, Lecture 15, modular arithmetic and its applications
Multiplicative cancellation needs extra care. Modulo six, , but : multiplication by two has merged distinct congruence classes. Cancelling a factor while retaining the integer modulus is justified when that factor has a modular multiplicative inverse, equivalently when it is coprime to the integer modulus. A linear congruence can consequently have no solutions, one solution class, or several solution classes. The Chinese remainder theorem supplies a complementary operation: splitting a calculation across coprime integer moduli and reconstructing its class modulo their product.
Small remainders can also certify impossibility. A perfect square has residue zero or one modulo four, as checking the four congruence classes shows. Therefore an integer equation has no solution. The converse direction needs care: a permitted residue does not guarantee an integer solution, since but five is not a perfect square. Such local tests provide necessary conditions for Diophantine equations without replacing the full problem.
In Disquisitiones arithmeticae (1801), Carl Friedrich Gauss defines integer congruence in article 1 and adopts the symbol in article 2. Article 12 derives divisibility tests from powers of ten and explains checking arithmetic by its remainders. These passages show a systematic treatment of the same idea; they are not a claim that remainders were first used in 1801. [ref]
https://la.wikisource.org/wiki/Disquisitiones_arithmeticae/Sectio_prima. Gauss, Disquisitiones arithmeticae, section I, articles 1–2 and 12; text from the 1870 collected edition
Exponentiation by squaring computes an integer power by reading the exponent's binary expansion. Appending a binary digit to a prefix of value replaces by , so the corresponding power changes byEach new digit requires one squaring and, only for digit one, one further multiplication. The number of digits grows with the logarithm of the exponent, making this useful for modular exponentiation, primality testing, and powers of matrices using matrix multiplication.[ref]
A Computational Introduction to Number Theory and Algebra by Victor Shoup. Section 3.4, pp. 65–66: binary-prefix recurrence and repeated-squaring algorithm; p. 67: primality-testing application
For a concrete calculation, , so . The optimized left-to-right algorithm used here instead keeps one accumulated power: initialize from the leading digit one, then process only the remaining digits :Thus , using three squarings and two further multiplications, instead of twelve successive multiplications starting at .
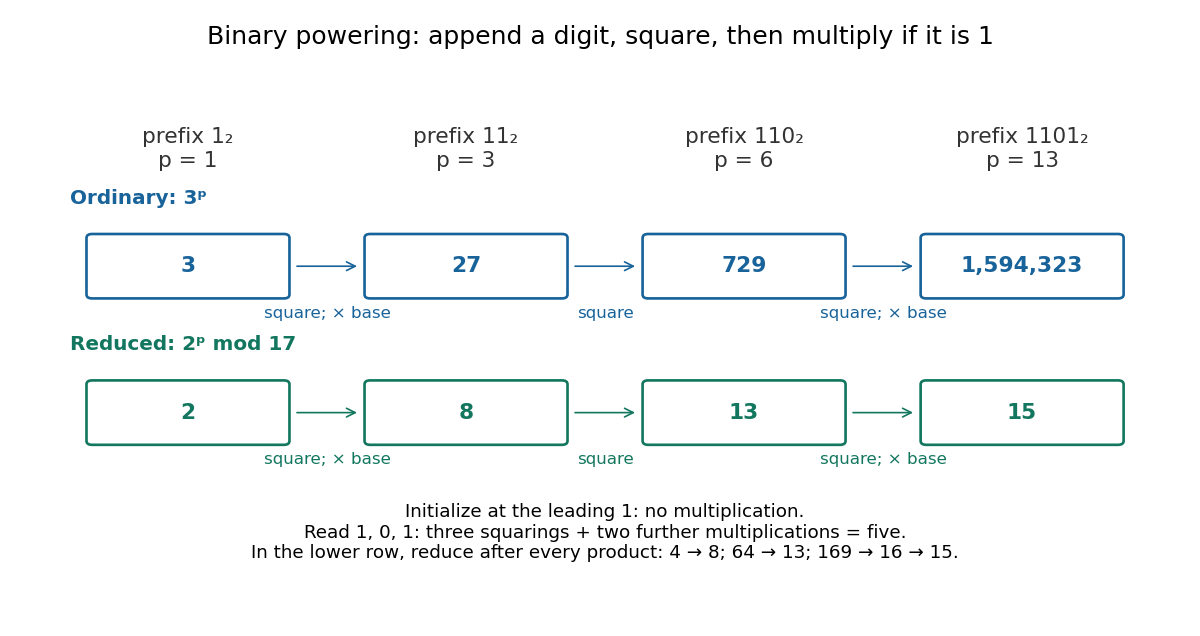
For a general positive integer with leading digit , set and, for , first replace by , then multiply it by if . Return . This explicitly skips the leading digit's otherwise unnecessary operations on one. A Computational Introduction to Number Theory and Algebra by Victor Shoup (Section 3.4, pp. 65–66) presents the version initialized at one and processing every digit; the optimization here makes the counting convention unambiguous.
The loop invariant is , where is the value of the digits already read. Initially and . If the next digit is , then squaring and optionally multiplying give , exactly the next prefix. At termination . This proof uses associativity of multiplication; it works in any monoid, including matrices with the identity matrix as identity element, and needs no commutativity between different bases.
For , return the identity element without performing a multiplication. This is the empty-product convention ; if , the algorithm therefore returns one for by convention, rather than resolving its meaning in every mathematical setting. Negative integer exponents require an inverse element: compute , counting the inversion separately. Over the integers, such an inverse generally leaves the integers, and a zero base has no inverse.
An integrable partial differential equation has enough exact structure, such as a Lax pair, infinitely many conserved quantities, or an inverse scattering transform, to reduce its evolution to auxiliary linear or finite-dimensional data.
Pinned article: Introduction to the OurBigBook Project
Welcome to the OurBigBook Project! Our goal is to create the perfect publishing platform for STEM subjects, and get university-level students to write the best free STEM tutorials ever.
Everyone is welcome to create an account and play with the site: ourbigbook.com/go/register. We belive that students themselves can write amazing tutorials, but teachers are welcome too. You can write about anything you want, it doesn't have to be STEM or even educational. Silly test content is very welcome and you won't be penalized in any way. Just keep it legal!
Intro to OurBigBook
. Source. We have two killer features:
- topics: topics group articles by different users with the same title, e.g. here is the topic for the "Fundamental Theorem of Calculus" ourbigbook.com/go/topic/fundamental-theorem-of-calculusArticles of different users are sorted by upvote within each article page. This feature is a bit like:
- a Wikipedia where each user can have their own version of each article
- a Q&A website like Stack Overflow, where multiple people can give their views on a given topic, and the best ones are sorted by upvote. Except you don't need to wait for someone to ask first, and any topic goes, no matter how narrow or broad
This feature makes it possible for readers to find better explanations of any topic created by other writers. And it allows writers to create an explanation in a place that readers might actually find it.
Figure 1. Screenshot of the "Derivative" topic page. View it live at: ourbigbook.com/go/topic/derivativeVideo 2. OurBigBook Web topics demo. Source. - local editing: you can store all your personal knowledge base content locally in a plaintext markup format that can be edited locally and published either:This way you can be sure that even if OurBigBook.com were to go down one day (which we have no plans to do as it is quite cheap to host!), your content will still be perfectly readable as a static site.
- to OurBigBook.com to get awesome multi-user features like topics and likes
- as HTML files to a static website, which you can host yourself for free on many external providers like GitHub Pages, and remain in full control

Figure 2. You can publish local OurBigBook lightweight markup files to either OurBigBook.com or as a static website.
Figure 3. Visual Studio Code extension installation.
Figure 5. . You can also edit articles on the Web editor without installing anything locally. Video 3. Edit locally and publish demo. Source. This shows editing OurBigBook Markup and publishing it using the Visual Studio Code extension. 
- Infinitely deep tables of contents:




All our software is open source and hosted at: github.com/ourbigbook/ourbigbook
Further documentation can be found at: docs.ourbigbook.com
Feel free to reach our to us for any help or suggestions: docs.ourbigbook.com/#contact