Cryptographic environment
ID: cryptographic-environment

A cryptographic environment is the interactive external context used to judge a cryptographic protocol in universal composability. It supplies honest parties' inputs, observes their outputs, communicates with the adversary, and ultimately outputs a decision bit. The comparison asks whether this bit's probability distribution changes detectably between the real execution and an ideal execution with a cryptographic simulator.[ref]
Universally Composable Security: A Tutorial by Ran Canetti. PDF pp. 20–24, execution model, protocol emulation and quantitative formulation
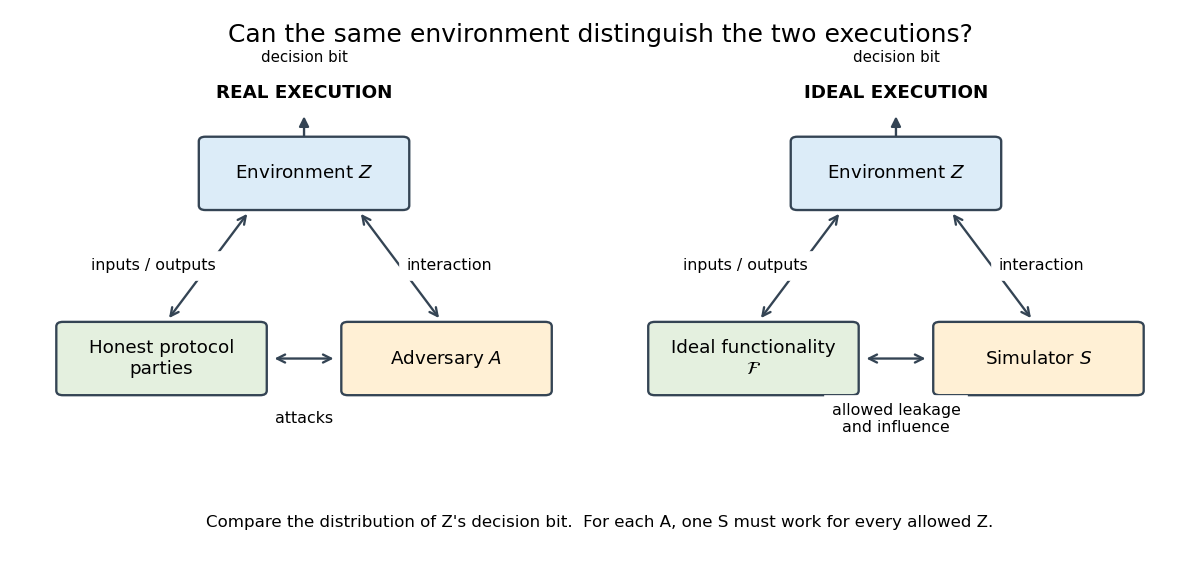
The same cryptographic environment observes either a real protocol and adversary or an ideal service and simulator. Honest-party forwarding is collapsed into the ideal-service box.
Details. 
The cryptographic environment models other software using the service, including choices depending on earlier outputs. It can retain private information with which to check later responses. Its view therefore includes the relationship between inputs, outputs and adversarial messages, not just isolated packet statistics.
An original two-bit example shows why that relationship matters. Let be a random variable with the uniform distribution on a finite set . One system returns ; another returns with an independent uniform bit. Each individual coordinate has the same marginal distribution in both systems. Nevertheless, the test “accept exactly when the two bits agree” has acceptance probabilitiesIts cryptographic distinguishing advantage is . Matching each output's marginal does not match their joint probability distribution. An interactive cryptographic environment can perform corresponding consistency checks against its retained inputs.
In the computational definition, the cryptographic environment has the specified polynomial time bound indexed by the cryptographic security parameter. For each real adversary, one cryptographic simulator must handle every allowed cryptographic environment; choosing a new simulator after learning which particular context will test it changes the requirement.[ref]
Universally Composable Security: A Tutorial by Ran Canetti. PDF p. 23, quantifier order; pp. 74–76, general formulation and restrictions
This breadth explains the usefulness of universal composability: a service can be analysed within a larger application context. The conclusion still concerns the interactions and cryptographic leakage admitted by the stated execution model.
New to topics? Read the docs here!