A Euclidean domain is an integral domain with a function such that, for with , there are satisfying and either or . The function need not be an ordinary absolute value.
The integers use and over a field uses polynomial degree. Repeated division gives the Euclidean algorithm and a greatest common divisor. Choosing a nonzero element of least Euclidean value in an ideal proves that every ideal is principal, so every Euclidean domain is a principal ideal domain.
For a field , polynomial division makes the one-variable polynomial ring a Euclidean domain with Euclidean function equal to the polynomial degree. For a divisor , subtract a suitable scalar multiple of to cancel the leading coefficient of the current remainder. Its degree strictly decreases. Iteration terminates at , where or . Division by the leading coefficient is valid because it is nonzero in a field.
Let be a Euclidean domain with Euclidean function , and let be a nonzero ideal. Choose minimizing the nonnegative integer . For , divide with or . Since , the latter case contradicts minimality. Hence every is a multiple of , giving . The zero ideal is , so every ideal is a principal ideal and is a principal ideal domain.
The ring of integers is a Euclidean domain for . In its lattice choose the nearest row, whose imaginary-coordinate error is at most , then the nearest point on that row, whose real-coordinate error is at most . Every complex number is thus within squared distance of a lattice point, giving Euclidean division. The suborder has the nonprincipal ideal and consequently is not a Euclidean domain for any Euclidean function.
A Euclidean function on an integral domain assigns a nonnegative integer to every nonzero element so that, for with , there are satisfying and either or .
The product of a Gaussian integer with its complex conjugate. It is multiplicative: , which gives the Brahmagupta-Fibonacci identity.
A nonzero Gaussian integer is squarefree if no square of a Gaussian prime divides it. Equivalently, every exponent in its Gaussian prime factorization is at most one, disregarding multiplication by units.
The Gaussian integer is not squarefree, because . By contrast is squarefree: its factors are nonassociate Gaussian primes. Thus squarefreeness in need not agree with squarefreeness in . This distinction is essential when using a Gaussian Möbius function to exclude repeated prime factors.
The Gaussian Möbius function on nonzero Gaussian integers is zero when a square of a Gaussian prime divides the argument, and otherwise equals , where is the number of nonassociate prime factors. It takes value one on units and is unchanged by multiplying its argument by a unit.
To sum over divisors without counting associates four times, one may define it on nonzero principal ideals, or choose one generator from each associate class. Then is one for the unit ideal and zero otherwise: for a product of distinct prime ideals the sum is . This gives Möbius inversion in Gaussian arithmetic.
A Gaussian prime is a nonzero nonunit Gaussian integer irreducible in . Since this ring is a Euclidean domain, irreducible and prime elements coincide. For , is a Gaussian prime exactly when is an ordinary prime number. On a coordinate axis, it is prime exactly when the nonzero coordinate has absolute value an ordinary prime congruent to three modulo four.
Thus , , and are Gaussian primes, while and are not. The multiplicative norm makes these factorizations and primality tests transparent.
An odd Gaussian integer is primary when it satisfies the displayed congruence. The four units have distinct images in , a group of order four; hence every odd ideal has a unique primary generator. Indeed and .
If is a Gaussian integer and is a nonzero prime ideal of , then is a finite field. Complex conjugation preserves , so a nonzero gives the positive integer . Primality supplies a rational prime . Since satisfies the monic polynomial , the ring is a quotient of and has at most elements. It is a finite integral domain, hence a field. The proof does not require to be a principal ideal domain.
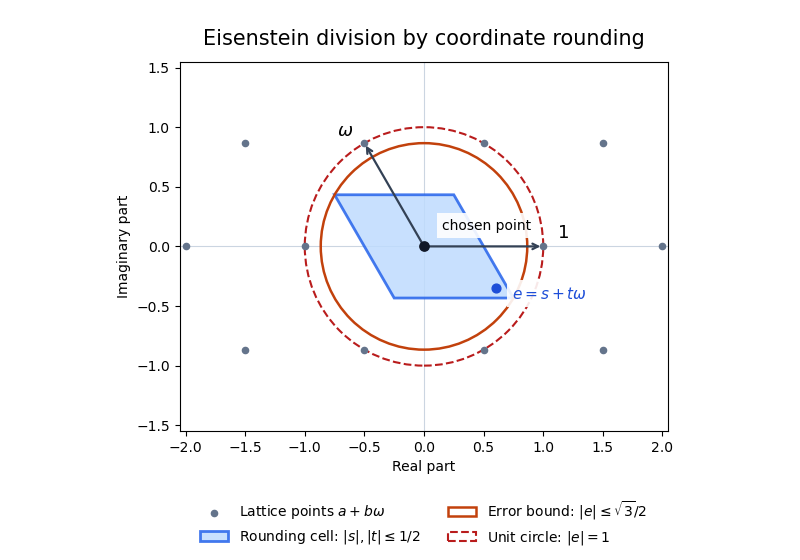
For a primitive cube root of unity , the Eisenstein integers form the triangular latticeTheir multiplicative norm is .
For an Eisenstein integer , with , the norm is . It is a positive integer for , since , and is multiplicative by the multiplicativity of the complex modulus. An element is a unit exactly when its norm is one: one direction follows from multiplicativity and integrality, and the other from the inverse .
Let be a prime number dividing , and set . The case is . For , useThe Eisenstein integer divides this product, but divides neither factor: divisibility by the rational integer in the basis requires both integer coefficients to be divisible by , whereas the second coefficients are and . Thus is not a prime element of .
The Euclidean norm on the Eisenstein integers makes this ring a principal ideal domain. Since irreducible elements of a principal ideal domain are prime, admits a factorization into two nonunits. The positive integral Eisenstein norm is multiplicative, and its value is one exactly on units: when , its complex conjugate is an inverse. Thus and , forcing both norms to be . Writing proves the displayed representation.
Every complex number can be written uniquely as with real , where . Round separately to integers . The error is with , andFor Eisenstein integers with , apply this to to choose . The remainder is an Eisenstein integer and if nonzero. Thus the Eisenstein norm is a Euclidean function and these integers form a Euclidean domain. Coordinate rounding suffices; no closest-point theorem is needed.
Articles by others on the same topic


A Euclidean domain is a type of integral domain (a non-zero commutative ring with no zero divisors) that satisfies a certain property similar to the division algorithm in the integers.