Propositional logic studies reasoning with whole propositions represented by letters such as and , and propositional formulas built from them using logical connectives. The classical two-valued, truth-functional presentation below assigns each primitive proposition either true or false: each compound value depends only on its component values. This is classical propositional logic; other systems, including Intuitionistic propositional logic, have different semantics and rules.
Starting with and , one can build by logical negation, by logical conjunction, by logical disjunction, and by logical implication, then combine these into larger propositional formulas. Parentheses specify the construction: has logical conjunction as its outermost logical connective. Primitive propositions have no internal structure in this language; a first-order formula can additionally describe objects and quantify over them. The formation rules are given in forall x: Calgary, chapter 6.
The following truth table shows the four basic logical connectives. Logical disjunction is inclusive: is true when either or both inputs are true. Classical logical implication has exactly the same values as ; its only false row has true and false. These truth conditions are specified in forall x: Calgary, chapter 9.
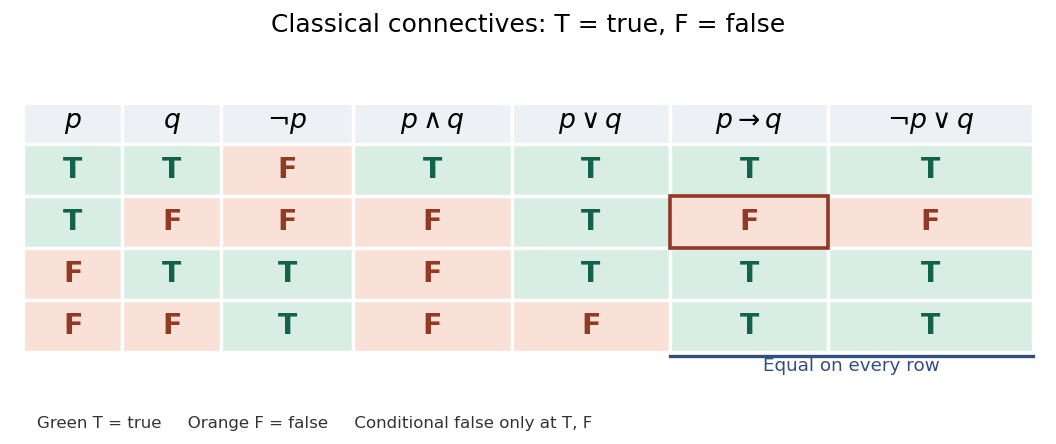
Evaluate from the inside out: first the logical implication, then the outer logical conjunction. The final column also tests the logical implication expressing the modus ponens rule:At , the logical implication is false, so the logical conjunction is false. The abstract syntax tree below separates the construction of the propositional formula from the values propagated through it. Both occurrences of receive the same value from the Boolean valuation. With the opposite assignment , the logical implication is true but the logical conjunction is still false because its second input is false. Recursive evaluation and exhaustive truth tables are explained in forall x: Calgary, chapter 11.
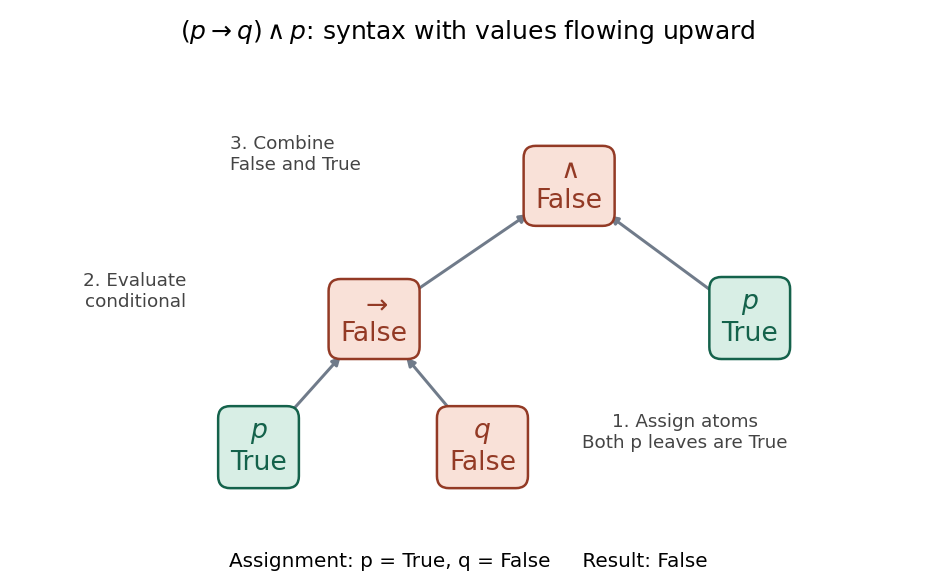
The last column is always true: is a tautology. This expresses the logical validity of the modus ponens rule: whenever both premises and are true, is true. It does not say the premises are true under every Boolean valuation; their logical conjunction is true only on the first row. For a short natural deduction proof outline, assume , extract both conjuncts, apply the implication elimination rule to obtain , then discharge the assumption by the implication introduction rule. See forall x: Calgary, sections 17.3–17.5.
Three tests answer different questions: Boolean satisfiability requires at least one true row, a tautology requires every row true, and a contradiction has every row false. Thus is a tautology, is a contradiction, and is satisfiable but not a tautology: it is true only at . See forall x: Calgary, sections 12.1–12.4.
Propositional logic is useful because an inference pattern can be checked once and reused for many choices of propositions. Its beauty is that a finite truth table completely settles classical truth-functional questions about a fixed propositional formula. But logical validity does not verify real atomic claims. If means “the switch is closed” and means “the lamp is lit”, a valid use of the modus ponens rule still requires establishing its premises about the apparatus; the truth table supplies neither an observation nor a causal explanation. See forall x: Calgary, chapter 2 and chapter 10.
A propositional variable is an atomic symbol assigned a truth value by a Boolean valuation. A propositional formula is built from these symbols by logical connectives. The variables carry no quantifiers over individuals; their values may be chosen independently.
From Boolean clauses containing complementary Boolean literals, derive the Boolean clause formed by removing that complementary pair and taking the remaining Boolean literals. For example, resolving with gives . Backward proof search with a positive-headed Horn clause and an all-negative query is a restricted use of this rule.
An indivisible statement treated as either true or false. In a labelled transition system, an atomic proposition holds at state exactly when .
A propositional formula semantically entails when every Boolean valuation satisfying satisfies . Equivalently, is an unsatisfiable Boolean formula. Deciding semantic entailment is co-NP-complete: a counterexample Boolean valuation certifies failure in polynomial time, while reduces unsatisfiability to semantic entailment.
In propositional logic with the usual two truth values, negating a proposition twice preserves its truth value. Thus the complement of a set taken twice, in one fixed universal set, is the original set.
Every finite collection of finite propositional formulas mentions only finitely many Boolean variables. Two Boolean valuations agreeing on those variables satisfy exactly the same formulas. They therefore have the same value under any weighted formula utility representation using that collection.
This observation limits representation over infinite sets. On , the function indicating whether the selected subset is infinite cannot be represented by a finite rule base: if is the finite set of mentioned indices, and agree on all those indices but require values zero and one. Completeness claims for finite propositional rule bases must therefore specify a finite underlying set or restrict the functions represented.
A contradiction is an assertion or collection of assumptions from which logical falsity follows. Deriving both a statement and its logical negation is a standard example. A contradiction under a temporary assumption can establish that assumption's negation; classical proof by contradiction additionally uses this to establish positive conclusions.
Identify classical propositional formulae when their equivalence is provable from a fixed theory. Their equivalence classes form the Lindenbaum algebra: meet and join are induced by conjunction and disjunction, complementation by negation, and the order by provable implication. Provable equivalence is preserved by each connective, so these operations are well-defined; the familiar classical propositional identities make this a Boolean algebra. A homomorphism of lattices to preserving zero and one also preserves complements and therefore specifies a truth valuation of the atomic propositions. All axioms of the fixed theory represent one. Separating the class of an unprovable formula from one consequently gives a countervaluation, proving the completeness theorem for propositional logic.
Take formulas whose free variables lie among a fixed -tuple and identify them when their universal equivalence follows from . Conjunction, disjunction and negation induce a Boolean algebra; its order is implication modulo . Complete types correspond to ultrafilters and isolated complete types to atoms. For a complete theory in a countable language, finiteness of these algebras for every finite characterizes countable categoricity.
A propositional theory is a set of propositional formulas, sometimes identified with its deductive closure. It is a consistent set of formulae when contradiction is not derivable from it. The completeness theorem for propositional logic identifies consistency with existence of a satisfying Boolean valuation.
A propositional type is a collection of propositional formulas to be jointly realized by a Boolean valuation. A valuation realizes it when every member is true and omits it when some member is false. For propositional omission arguments, the collection need not itself be consistent.
If a consistent propositional theory locally omits every member of a countable family of propositional types, it has a Boolean valuation omitting them all. One may also impose any finite condition consistent with the theory. Successively extend the condition by a negated member of the next type; local omission preserves consistency. The propositional compactness theorem then supplies the valuation. Countability of the ambient language and decidability of consistency are not needed for this argument.
Relative to a consistent propositional theory , a nonprincipal propositional type has no formula consistent with that implies every member modulo . Equivalently, for each finite condition consistent with , some member leaves consistent. This is the local omission condition for the extended omitting types theorem for propositional logic.
A propositional formula is built from atomic propositions using logical connectives. Unlike a first-order formula, it has no quantifiers over individuals. A Boolean valuation interprets its atoms as truth values and evaluates its connectives recursively.
A subformula is a constituent propositional formula in a formula's recursive construction, including the whole formula itself. For an atomic variable the only subformula is itself; for , add to the subformulas of ; for a binary connective, add the combined formula to the union of the two operands' subformulas. The set of distinct subformulas can have smaller cardinality than the number of occurrences in the abstract syntax tree when the same expression appears more than once.
A subformula occurrence specifies a particular position in the syntax tree of a formula. Two occurrences can contain the same logical formula while being different nodes. Replacement of one occurrence does not necessarily replace the others.
Subformula replacement is the operation of replacing one specified subformula occurrence by another logical formula. Its preservation of well-formedness is the subformula replacement theorem.
Replacing one designated subformula occurrence in a propositional formula by another propositional formula preserves well-formedness. Induct on the context surrounding the occurrence: at the root the result is the replacement formula; under a connective apply the induction hypothesis to the affected child and rebuild the parent using its formation rule.
Replacing a designated subformula by a logically equivalent formula preserves logical equivalence of the surrounding propositional formulas. For any Boolean valuation the two expressions at the replaced node have the same truth value. Each logical connective preserves this agreement when its other inputs are unchanged. Induction from that node to the root proves agreement of the whole formulas under every valuation.
Every propositional formula generated by a parenthesized grammar has equally many opening and closing parentheses. By structural induction, atomic formulas begin with equal zero counts; negation preserves them; and a parenthesized binary logical connective adds its two subformula counts and one parenthesis of each kind. An optional paired-parenthesis construction also adds one to both counts. This necessary syntactic invariant is useful for checking generated expressions, though equal counts alone do not guarantee correctly nested syntax.
A propositional substitution maps each atomic propositional variable to a propositional formula and extends recursively through every logical connective. Replacements are simultaneous: a variable appearing inside a replacement formula is not replaced again in the same substitution step. Since propositional logic has no variable-binding quantifiers, this operation has no variable-capture problem.
A conjunction containing each of a specified finite collection of Boolean variables exactly once, either positively or negated. It is satisfied by exactly one Boolean valuation of those variables. The minterms for all valuations are mutually exclusive and collectively exhaustive, so they can encode an arbitrary finite table of values.
The displayed identity follows by testing the two possible truth values of . Existentially forgetting gives . Repeating this operation produces a propositional formula on a specified remaining vocabulary. Logical truth constants are needed if that vocabulary is empty.
If , eliminate the letters private to byEvery assignment satisfying satisfies one disjunct of . If an assignment satisfies , change only the eliminated letters to its witnessing assignment. The modified assignment satisfies and hence , whose letters were unchanged. Thus , and the propositional completeness theorem gives the two derivations. The interpolant uses only common letters; an empty common vocabulary is handled by logical truth constants.
An implication is derivable from a theory precisely when its conclusion is derivable after adjoining its antecedent. Together with classical contradiction rules, this identifies failure to prove a proposition with consistency after adjoining its negation.
Conditional modus ponens derives from and . It is the step which translates a modus ponens rule inference when discharging a common assumption. In the case-elimination Hilbert calculus, the third scheme first gives ; the second scheme combines the two conditionals to give .
In the usual first-order Hilbert system, logical implication discharge requires the appropriate generalization restriction: a variable generalized in the derivation must not be free in the assumption being discharged. Equivalently use a proof system whose generalization rule already forbids variables free in open assumptions. One can first discharge a temporary assumption and then generalize if the quantified variable is not free in the remaining assumptions. Ignoring this side condition would allow deriving universal conclusions from a single arbitrary instance as an open hypothesis.
For standard effective proof presentations, the syntactic deduction theorem and its reverse give effective transformations between proofs in a one-sentence extension and proofs of an implication in the base theory. Arithmetic can verify these transformations, yielding the displayed internal equivalence under the usual representation and proof-predicate hypotheses. It distinguishes internal proof transformations from an unlicensed reflection step taking provability to truth.
Classical propositional logic interprets propositions as true or false and validates principles such as the law of excluded middle and double-negation elimination.
Assume and temporarily assume . A further assumption yields a contradiction and hence by the logical falsity elimination rule; discharge it to obtain . Applying gives , contradicting . Discharge the latter assumption to obtain , apply double-negation elimination, and finally discharge . This is a derivation from the primitive classical natural deduction rules. The principle is named for Charles Sanders Peirce.
A tautology is a propositional formula true under every Boolean valuation in classical propositional logic, such as the law of excluded middle . A primitive proposition is not a tautology, even if it represents a true statement. See forall x: Calgary, section 12.1.
An argument has logical validity in classical propositional logic when no Boolean valuation makes all premises true and the conclusion false: . With no premises, says that is a tautology. See forall x: Calgary, sections 12.4–12.6.
A Boolean valuation assigns each primitive proposition a value in , equivalently , and extends recursively to every propositional formula using the classical logical connectives. The same primitive proposition always receives the same value within one Boolean valuation. For compound propositional formulas and ,Every other case receives the opposite value. Thus gives . A truth table varies the assignment; recursive evaluation computes one row. The truth-functional restriction means that changing what the primitive propositions describe, while retaining their values, cannot change the value of the compound propositional formula. See forall x: Calgary, chapter 9 and section 10.1.
A truth table lists a propositional formula's value for every Boolean valuation of its distinct primitive propositions. With primitive propositions, there are rows: each independently receives T or F. Evaluate compound columns from their subexpressions using the classical rules for logical connectives. This is exhaustive checking, so a formula true on every row is valid in classical propositional logic.
For a computed example over the natural numbers, let mean that is an even number and mean . The choices realize respectively : all four possible inputs.
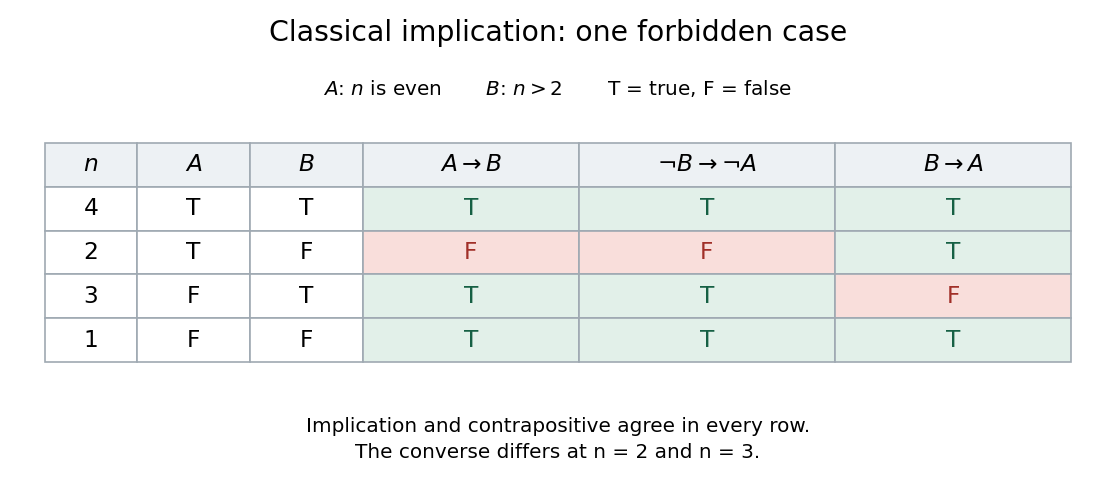
The logical implication and its contrapositive agree on every row; the converse implication differs on two rows. A truth table therefore checks equivalence or supplies a counterexample. Classical truth conditions are given in forall x: Calgary, section 31.2. These two-valued truth tables do not characterize validity in Intuitionistic propositional logic.
A logical connective forms a compound proposition from component propositions; logical truth and logical falsity are the zero-input cases. Logical negation has one input, while logical conjunction, logical disjunction, and logical implication each have two. In classical propositional logic, these logical connectives are truth-functional: their output value is determined by their input values, as listed in a truth table. This does not characterize every kind of logical connective in every logic. See forall x: Calgary, section 10.1.
A binary logical connective true exactly when its two arguments have the same truth value. It is logically equivalent to , and hence to . Its truth table has value one on input pairs and , and zero on and .
Logical implication forms the proposition , read “if , then ”. In classical propositional logic, it is false exactly when is true and is false. Equivalently, it has the same truth table as , using logical negation and logical disjunction. A false hypothesis makes the logical implication true regardless of its conclusion; thus it asserts neither the hypothesis nor a causal connection.
For example, for every natural number , divisibility by four implies that is an even number: . At , both statements are true. At , the hypothesis is false and the conclusion true; at , both are false. The only forbidden case is a multiple of four that is not an even number.
In Intuitionistic propositional logic, a proof of consists of a construction transforming any proof of into a proof of . The implication introduction rule proves under a temporary assumption ; the modus ponens rule applies the result when is available. The classical identification with is not generally intuitionistically valid.
For distinct propositional variables, eliminate each right-associated logical implication to obtain . Exactly one Boolean valuation falsifies all these disjuncts: and . Of the assignments, the other are satisfying assignments. Left-associated implication chains have a different meaning and need not have the same count.
The contrapositive of a logical implication reverses the direction and applies logical negation to both sides: . In classical propositional logic they are equivalent, so either can be proved in place of the other. The contrapositive of “divisibility by four implies being an even number” says that a number that is not an even number cannot be divisible by four.
In Intuitionistic propositional logic, still implies its contrapositive: assumptions and would yield and hence a contradiction. The reverse direction is not generally valid. From and , one obtains only ; obtaining additionally requires double-negation elimination.
The converse implication of is . It exchanges hypothesis and conclusion without logical negation. It need not follow from the original logical implication: is an even number but is not divisible by four. Thus “being an even number implies divisibility by four” is false, although the original implication holds for all natural numbers. Proving both directions establishes an “if and only if” statement; proving a contrapositive establishes the original implication classically, without establishing its converse implication.
A logical implication holds whenever its premise is false. For partial correctness, an execution that never terminates supplies no final state violating the postcondition.
The conjunction holds when both and hold.
An AND gate computes for bits . It is irreversible when only its one-bit output is retained. The Toffoli gate embeds the operation reversibly as ; setting preserves the inputs while recording their logical conjunction.
The disjunction holds when at least one of and holds. Constructively, a proof records which disjunct holds and provides its proof.
A logic gate computing inclusive logical disjunction: its output is one exactly when at least one input is one.
Logical truth is the nullary connective that is always true.
A logical matrix specifies truth values, designated values, and operations interpreting the primitive connectives. To prove nonderivability from an axiom set, it suffices that every axiom instance is designated and every inference rule preserves designation, while the proposed conclusion is not designated under some valuation. The primitive connective symbols need not receive their intended classical meanings: preservation by the displayed rules is what makes the syntactic obstruction valid. Rules with discharged assumptions, such as a deduction theorem for propositional logic, must also preserve consequence for arbitrary assumption sets.
Take ordinary material logical implication on , designate , and interpret negation by the constant-zero operation . Then and are always designated, and modus ponens rule and logical implication discharge preserve consequence. But is false for . Thus the first two schemes and the deduction rule do not derive the last scheme. This detects the loss of a genuine classical-negation principle even though all the displayed schemes are tautologies under the usual classical negation.
Logical falsity is the nullary connective with no proof.
In classical propositional logic, a truth value is false or true, encoded by a bit as zero or one. A Boolean valuation assigns these values to primitive propositions and extends to compound propositional formulas through logical connectives.
Natural deduction presents logic through introduction and elimination rules for each logical connective.
Reading an inference rule backwards to replace a desired conclusion by sufficient subgoals. A conjunction goal can be replaced by its two conjuncts using the conjunction introduction rule; an available disjunction can instead lead to two case subgoals using the disjunction elimination rule. Different choices change the organization and sharing of subproofs. Scope and assumption discharge conditions remain obligations even when a rule is applied backwards during proof search.
Adding unused assumptions to the context of a logical derivation. The original derivation still proves the same conclusion because it need not use every available assumption. When eigenvariables are used, rename them first if necessary to preserve the eigenvariable condition for any newly added assumptions. This explains how disjunction elimination with different branch contexts can be written using a common context containing all their assumptions.
Thinning enlarges the assumptions without changing a conclusion. In a predicate-calculus presentation with context-sensitive generalization, a generalization valid before adding an unused assumption may not be replayable with that assumption open. An explicit weakening step nevertheless imports the already proved conclusion. In propositional calculus with only axiom schemes and modus ponens, weakening is admissible by replaying the proof. The need for a separately stated rule depends on how proof dependencies are represented.
The reflexivity rule for first-order equality: any well-formed term satisfies without additional premises. Together with the equality elimination rule, it derives symmetry: from and , substitute in the first designated argument position of to obtain . Transitivity follows from and by substitution in the second designated argument position of .
Derive each side of a logical biconditional under a temporary assumption of the other, then discharge both assumptions. The surrounding assumptions remain. This is equivalent to deriving the two implications and combining them as the two directions of equivalence.
Introduce exclusive or from either or . To eliminate , derive the same conclusion in two subproofs, one under and the other under , then discharge both pairs of case assumptions. These rules express exactly the two disjuncts of the displayed disjunctive normal form. Conjunction introduction and disjunction introduction derive that formula in each elimination branch; conversely disjunction elimination and conjunction elimination supply the two introduction cases. This proves equivalence without adding an unproved truth-table inference to a formal derivation.
From , temporarily assume . Negation elimination rule gives logical falsity; discharge that temporary assumption by negation introduction to obtain . This is valid in Intuitionistic propositional logic, unlike unrestricted double-negation elimination.
A local derivation made under additional temporary assumptions. Its conclusions can be used within their scopes, but exporting a result requires a rule that accounts for those assumptions. Indentation, boxes or explicit assumption labels record that dependency information.
A temporary assumption is introduced for a hypothetical subproof and retained only within that scope. A suitable inference rule can discharge it while forming a conclusion valid under the surrounding assumptions. Its scope must be recorded even when the assumption is unused inside the subproof.
From infer . Assume , then assume . Implication elimination rule gives and , hence . Discharge and then by the implication introduction rule. The original premise and any surrounding assumptions remain available.
From a logical derivation of , infer under the same surrounding assumptions. To derive the rule, temporarily assume , retain the available , and discharge by the implication introduction rule. Its being unused is allowed.
From , reason under a temporary assumption for a fresh witness . If this yields a conclusion not containing free, close the witness subproof and infer . The eigenvariable condition also requires that not be free in other undischarged assumptions. The rule does not authorize selecting one fixed named object as a witness or allowing the witness to escape its scope.
An eigenvariable condition ensures that a variable chosen as arbitrary or as an existential witness cannot smuggle extra information into a quantifier inference. For the universal quantifier introduction rule, the generalized variable must not occur free in any undischarged assumption. For the existential quantifier elimination rule, the fresh witness must not occur free in the resulting conclusion or in the other undischarged assumptions. Temporary assumptions may contain it if they are discharged before the final inference.
A variable used as an arbitrary parameter in a natural deduction subproof, subject to an eigenvariable condition. For universal introduction, it must be free in no undischarged assumption. For existential elimination, a temporary witness must also be free in no conclusion exported from its subproof. These restrictions distinguish an arbitrary object from one constrained by a special hypothesis.
An invalid quantifier inference that exports a formula still referring freely to a temporary existential witness. From one cannot infer for an independently named object . A two-element interpretation with exactly one -object refutes that inference. Introducing another quantifier after the invalid step does not repair it; the introduction must take place before the witness scope is closed.
Assumption discharge closes a designated temporary assumption together with its dependent subproof. Implication introduction rule turns a logical derivation of under into outside that temporary scope. Negation introduction rule turns a logical derivation of logical falsity under into . Disjunction elimination rule discharges its separate case assumptions while retaining any surrounding premises.
From logical falsity infer any proposition. This rule permits a contradictory case inside a disjunction elimination rule proof to reach the common required conclusion.
From and , infer by capture-free substitution. Rewriting in the opposite direction first uses symmetry of equality.
If is proved and is not free in any undischarged assumption, infer , with capture-free replacement. The freshness condition prevents generalizing from a special object.
From and two subproofs deriving the same conclusion , one under an additional assumption and the other under an additional assumption , infer and discharge those two case assumptions. Any other assumptions remain in force.
If each of , and separately yields the same conclusion , then yields , with the three case assumptions discharged. For , first eliminate the outer logical disjunction, using a nested applications of the disjunction elimination rule on the branch. For , nest the second elimination in the other branch. Common surrounding assumptions remain open.
From , infer ; from , infer .
From , infer either or .
From derivations of and under the current assumptions, infer .
From a propositional formula and its negation, infer logical falsity. This identifies a contradiction inside a natural deduction derivation; a later negation introduction rule may discharge the assumption that led to it.
If a natural deduction subproof derives logical falsity from a temporary assumption , discharge that assumption to conclude . Other undischarged assumptions remain available. This gives a constructive proof of a negation and does not require double-negation elimination.
The rule with premises and conclusion retains the first derivation while allowing an unused second assumption. Under the Curry-Howard correspondence, the output term is the first premise term, with the enlarged context. This allows a lambda abstraction whose bound variable does not occur in its body.
From and , implication elimination derives . Under the Curry-Howard correspondence, this is application: from lambda terms and form .
The implication introduction rule discharges a temporary assumption from a derivation of , producing . Under the Curry-Howard correspondence, a body under gives the lambda abstraction . Unused assumptions may also be discharged.
Intuitionistic propositional logic omits unrestricted excluded middle and interprets implication constructively.
A lattice is a partially ordered set in which every pair has a greatest lower bound, called its meet, and a least upper bound, called its join.
The join of two elements of a lattice is their least upper bound. In a lattice of closed set families, it is the closure of their union.
The meet of two elements of a lattice is their greatest lower bound. For set families ordered by inclusion, it is their intersection whenever that intersection lies in the specified lattice.
A homomorphism between lattices preserves binary joins and meets: and . It is order preserving, since implies and hence . For a map into the two-element lattice, the inverse image of zero is a lattice ideal, and meet preservation says this ideal is prime: if a meet belongs to it, at least one factor does. Conversely the indicator of the complement of a prime lattice ideal preserves both operations. Preservation of distinguished top and bottom elements is an additional requirement for homomorphisms of bounded lattices.
A complete lattice is a partially ordered set in which every subset has a meet and a join, including the empty subset.
Every order-preserving function from a complete lattice to itself has a least and a greatest fixed point. More strongly, its set of fixed points is itself a complete lattice.
A distributive lattice is a lattice in which meet distributes over join and, equivalently, join distributes over meet.
A Boolean algebra is a bounded distributive lattice in which every element has a complement. Its meet, join, and complement abstract conjunction, disjunction, and negation.
An atom is a minimal nonzero Boolean-algebra element. In a Lindenbaum algebra, its nonempty formula class isolates a complete type. A finite Boolean algebra is the power set of its finite atom set. An infinite atomic Boolean algebra need not contain every union of atoms: the finite-cofinite algebra is a simple counterexample.
On an infinite set , take its finite and cofinite subsets with ordinary union, intersection and complement. Singletons are its atoms. Its Stone space consists of the isolated points of together with one nonisolated point whose ultrafilter contains all cofinite sets. For countably infinite this is a countable Boolean algebra with countably many atoms, not the uncountable full power set. It describes two-vector definability over a countably infinite field: dependent directions are isolated atoms and the independent-pair type is the additional nonisolated point.
Every proper lattice ideal of a Boolean algebra extends to a prime lattice ideal. More generally, an ideal disjoint from a lattice filter extends to a prime ideal still disjoint from that filter. This Boolean case of the Stone prime filter theorem is equivalent to the ultrafilter lemma over Zermelo–Fraenkel set theory and is weaker than the axiom of choice.
Articles were limited to the first 100 out of 152 total.
Articles by others on the same topic



In some systems, e.g. including Metamath, modus ponens alone tends to be enough, everything else can be defined based on it.