
For a prime number and an integer not divisible by , Fermat's little theorem states the modular congruenceEquivalently, for every integer , including and multiples of ,The first formulation follows from the second by multiplying by a modular multiplicative inverse of . Conversely, multiply the first by when ; when , both sides of the second are zero modulo . The divisibility condition in the first formulation is essential.[ref]
For , , so and . Also , while : a zero residue class cannot satisfy the first formulation. It does satisfy . A failure at a zero residue class therefore says nothing against a candidate's being a prime number.
The prime number is included. Its only nonzero residue class is one: every odd integer satisfies . Every integer also satisfies , because is even. Testing the first formulation with an even integer would violate its hypothesis.
The useful surprise is that every nonzero residue class returns to one at the same exponent , although its shortest return can be earlier. This gives exponent reduction for units: for a nonnegative integer , when . It also computes a modular multiplicative inverse as modulo , including . Repeated squaring makes these modular exponentiations practical.
In group theory, the nonzero residue classes form the multiplicative group of integers modulo n with , of group order . Lagrange's theorem says that the multiplicative order of divides , giving the guaranteed return. Euler's theorem extends this to a general integer modulus , using the units and Euler's totient function ; the Carmichael function gives the least common return exponent for all units. A nonzero residue class modulo a composite number need not be a unit.
Leonhard Euler's paper presented in 1732 and published in 1738 states a historical formulation: Theorem 1 says that powers with exponent leave zero or one upon division by a prime number . The preceding discussion states the difference-of-powers version and explicitly says that he does not have its proof.[ref]
Euler's totient function is the arithmetic functionIt counts the congruence classes modulo represented by integers coprime to . In particular, , since . For , the coprime integers among are , so ; they form a reduced residue system. [ref]
https://darijgrinberg.gitlab.io/floor.pdf. Darij Grinberg, MIT 18.781 lecture notes, Definition 2.1.2
Counting these congruence classes is useful because they are exactly the classes with modular multiplicative inverses. Their number supplies the exponent in Euler theorem. Möbius inversion gives the product formulawhere runs over distinct prime factors of . Thus for prime powers with , and . The product for is an empty product, so it gives the same convention .
For a prime number and a positive integer , the prime valuation is the exponent of in the prime factorization of , equivalentlyThus because divides but does not; , and . In particular . Multiplication adds prime valuations, , and the fundamental theorem of arithmetic makes comparison of prime valuations an exact test for divisibility between positive integers. This definition extends to a nonzero integer by taking its absolute value; for zero one commonly sets .
Diophantine approximation studies how closely numbers can be approximated by rational or algebraic numbers subject to bounds on their arithmetic complexity.
A composite integer is a Carmichael number if and only if it is a squarefree integer andThe criterion is named for Alwin Korselt. The two requirements are different: the first excludes repeated prime factors, while the second makes the exponent a common multiple of the prime-field return exponents.[ref]
For , the numbers divide with quotients . Thus 1105 is another Carmichael number. By contrast is squarefree, but ; a single failed divisor condition excludes it. This illustrates the appeal of the criterion: a statement about every unit becomes a small calculation using a known prime factorization.
The composite condition must be retained. A prime number is squarefree and satisfies the divisibility condition, but is excluded from the definition of a Carmichael number. The resulting certificate also depends on the supplied factors really being prime numbers; merely finding a product decomposition is insufficient.
A Carmichael number is a composite number for whichEvery unit modulo satisfies the same modular congruence supplied by Fermat's little theorem for a prime number. The name refers to Robert Daniel Carmichael. The coprime qualification is essential: a nonunit can expose a prime factor through a greatest common divisor calculation. A Carmichael number is therefore a Fermat pseudoprime to every coprime base, rather than to every nonzero residue class.[ref]
Carmichael Numbers and Korselt's Criterion by Keith Conrad. Definition 1, printed p. 1: composite input and coprime bases
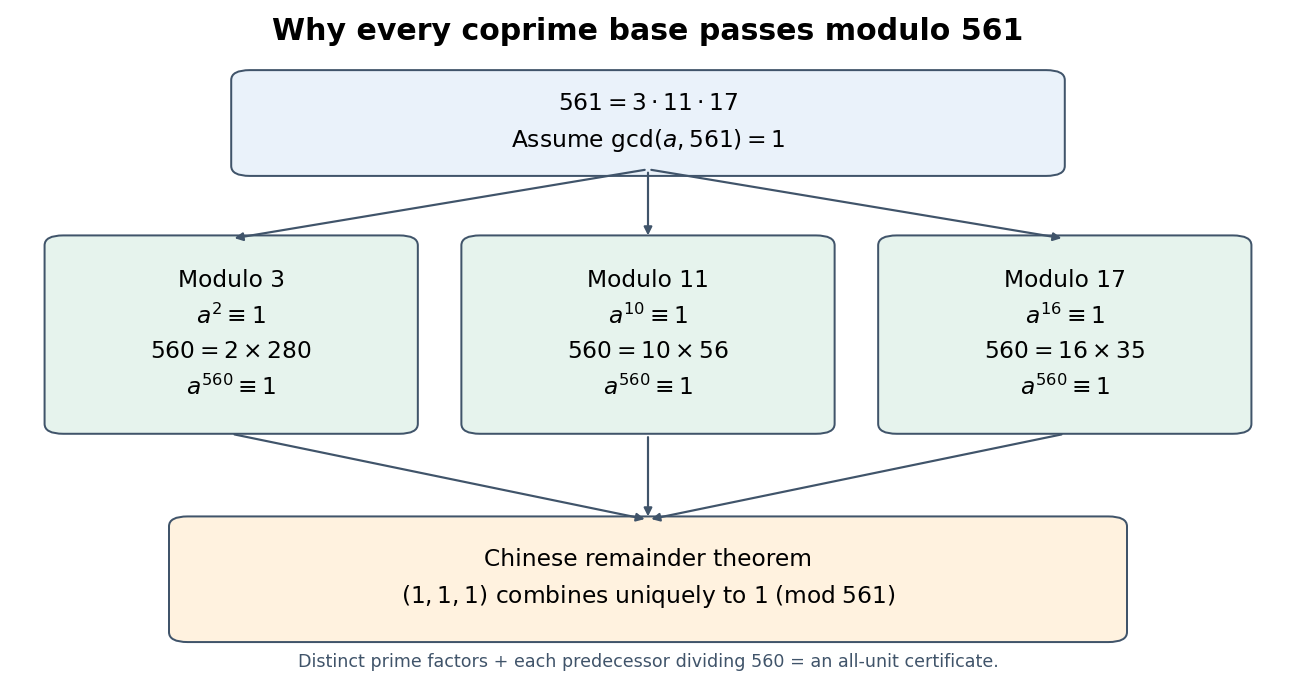
For example,The factors are distinct prime numbers. Their predecessor numbers all divide , so Korselt criterion applies. More explicitly, for any integer coprime to , Fermat's little theorem givesThe Chinese remainder theorem combines these into . This proves all coprime bases pass from three short divisibility checks, rather than from a long table of sampled bases.

Equivalently, a composite is a Carmichael number exactly when for every integer , including nonunits. The equivalence follows from Korselt criterion: modulo each prime factor, either is zero or its nonzero power returns to one, and squarefreeness combines those congruences. This does not say a nonunit satisfies . For instance gives , while ; the greatest common divisor already supplies the factor three.[ref]
The Carmichael function supplies another compact description: a composite is Carmichael exactly when . For , and . In contrast, Euler's totient function gives , which does not divide . The least common return exponent, rather than the number of units, controls this test.
The obstruction is useful to know when interpreting a Fermat primality test: even checking every coprime base cannot certify primality. The passing-base fraction for the Fermat test makes this failure quantitative. Stronger primality tests require additional structure, such as the squaring conditions in a Miller-Rabin primality test.
The historical record predates the name. Václav Šimerka's 1885 paper lists on printed page 224, together with factorizations. This is an early published list of examples, independently of their later name.[ref]
Zbytky z arithmetické posloupnosti by Václav Šimerka. Zbytky z arithmetické posloupnosti, printed p. 224, §9: list beginning with 561 and 1105; archive title sheet identifies Václav Šimerka and 1885
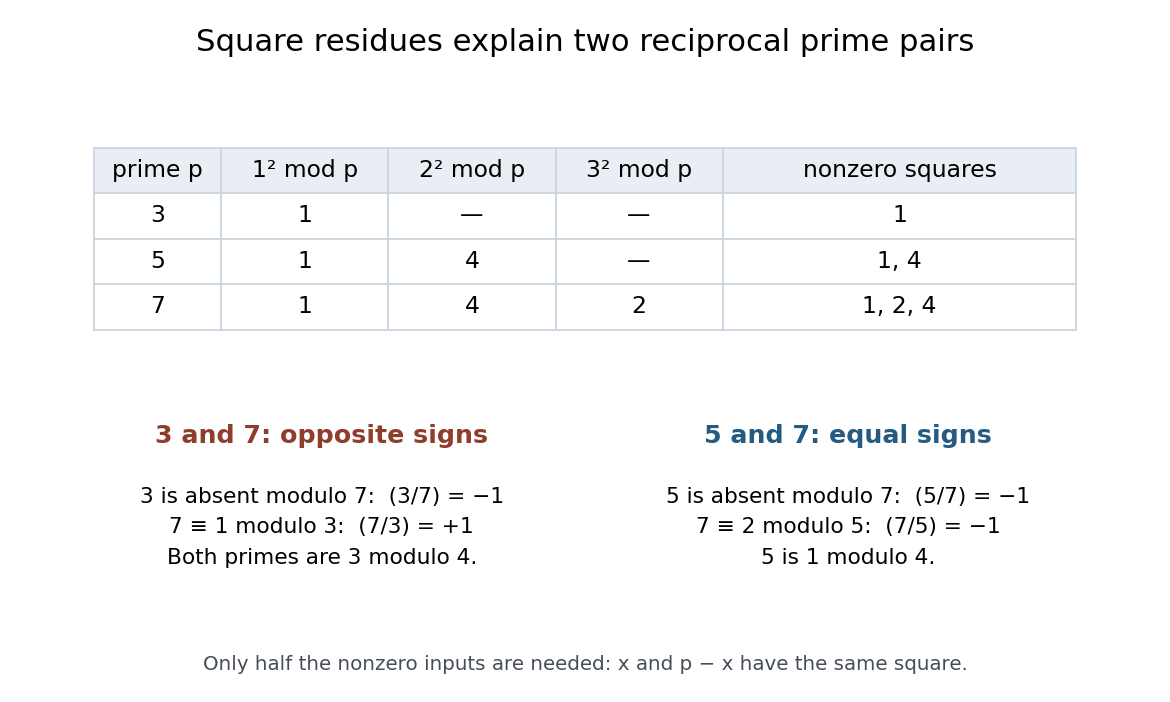
Quadratic reciprocity compares two questions: is the prime number a quadratic residue modulo , and is a quadratic residue modulo ? Let be distinct odd primes. In terms of the Legendre symbol,The two Legendre symbols have opposite signs exactly when both primes are modulo ; otherwise they are equal. Their values are nonzero because the primes are distinct. Equal signs can mean two quadratic residues or two quadratic nonresidues: reciprocity compares the answers rather than declaring either answer positive.[ref]
NIST Digital Library of Mathematical Functions. T. M. Apostol, Chapter 27, §27.9, equation 27.9.3: distinct odd prime hypotheses and reciprocity law
For a direct computation, the nonzero quadratic residues modulo are respectively , , and . Squaring just suffices because and have the same square modulo an odd prime .The pair has a sign flip, whereas has two negative signs. These small quadratic residue tables make the distinction tangible.

The first supplementary law for quadratic reciprocity handles numerator , and the second supplementary law for quadratic reciprocity handles numerator :For an odd prime , is a quadratic residue exactly when , while is a quadratic residue exactly when . The remaining odd congruence classes modulo , namely , make a quadratic nonresidue. These laws fill the cases excluded from swapping distinct odd primes.[ref]
For an odd prime , a nonzero congruence class is a quadratic residue when for some integer . Here "quadratic residue" excludes zero: zero is a square of a number, but is neither a quadratic residue nor a quadratic nonresidue under this convention. Some treatments include zero among quadratic residues; the distinction matters when counting them or discussing their subgroup.[ref]
Quadratic Residue Patterns Modulo a Prime by Keith Conrad. Keith Conrad, Quadratic Residue Patterns Modulo a Prime, §1, p. 1: nonzero convention and equal counts
Modulo seven, squaring the six nonzero congruence classes givesThus the set of quadratic residues is , and the quadratic nonresidues are . In particular, has exactly the two solutions : and . Modulo eleven the quadratic residues are instead . Two is therefore a quadratic residue modulo seven and a quadratic nonresidue modulo eleven: being a quadratic residue depends on the modulus.
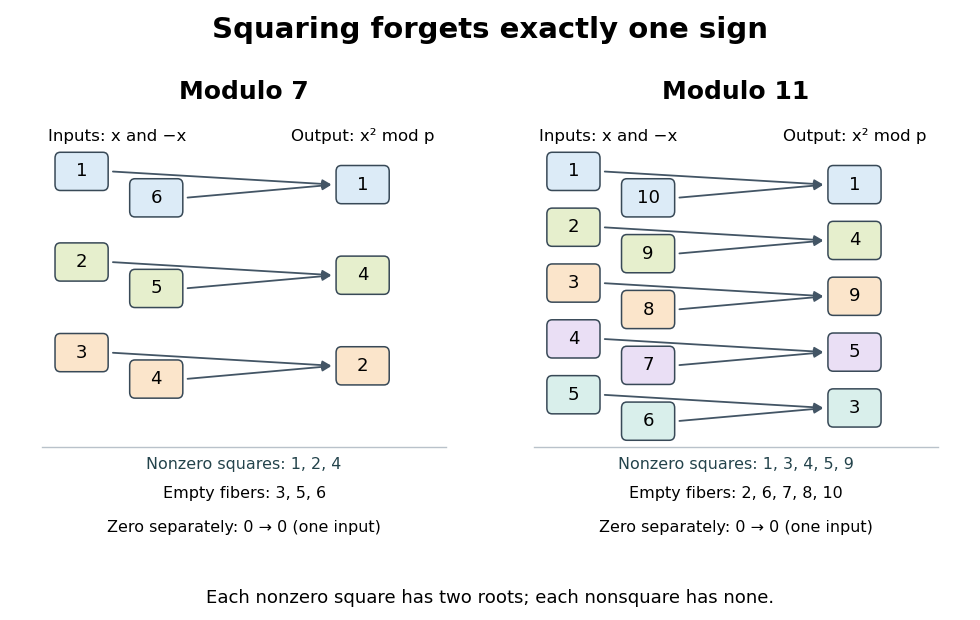

Why do the square roots come in pairs? If , the prime number divides , so it divides one factor: or . For nonzero these are distinct, because is an odd prime. Every nonempty nonzero fiber of a function of therefore contains exactly two inputs. Pairing the nonzero congruence classes gives exactly quadratic residues and quadratic nonresidues. Including zero gives different squares, with one rather than two square roots for zero.
The quadratic residues form a subgroup of the multiplicative group of a finite field , with index of a subgroup two. Indeed, one is a square, , and ; the inverses exist because the inputs are nonzero in the prime field. Equivalently, the squaring group homomorphism has kernel of a group homomorphism and image of a function . The apparent loss of a sign in squaring becomes a precise division of the nonzero arithmetic into two equal parts.
This structure turns a search for square roots into a yes-or-no test: Euler's criterion detects quadratic residues through modular exponentiation, and the Legendre symbol records the result as a sign. For a general integer modulus, the modular congruence still makes sense, but the two-root count and the prime field argument need not survive. For example, has four solutions ; the Chinese remainder theorem separates the sign choices modulo three and five.
A positive integer is decisive when every integer satisfying and is a prime number. There are only finitely many decisive numbers: every prime must divide a decisive , so the Chebyshev theta function gives , which eventually contradicts the linear lower bound for .
For a prime number and a nonzero integer , the P-adic valuation counts the exponent of in its prime factorization:For , it gives , , and . The sign of a nonzero integer does not change these prime exponents. Relative to an ordered factor base, the valuations supply the coordinates of its exponent vector.
The P-adic valuation extends to nonzero rational numbers by . For example, records a factor in the denominator instead of the numerator. Multiplication adds valuations, ; this is the arithmetic reason why adding exponent vectors can make a product a square. In particular, a positive integer is a square of a number precisely when all its prime exponents are even integers, the criterion used by a factor base.
An odd composite number is an Euler pseudoprime to a coprime base whenwhere the right side is the Jacobi symbol.
A Fermat pseudoprime is relative to its base. For example, passes base , but base yields , a Fermat witness. A Carmichael number has the stronger all-coprime-base property. This explains why finding one deceptive base and proving universal deception require different arguments.
There are unlisted articles, also show them or only show them.