For integers and a positive integer modulus , modular congruence meansThus for some integer : the two integers differ by complete cycles of length . For example, because , and because . A modular congruence need not be an equality of integers.
On a twelve-position clock labelled , adding five to nine follows . Hence : the final position remembers the remainder while forgetting a complete revolution.
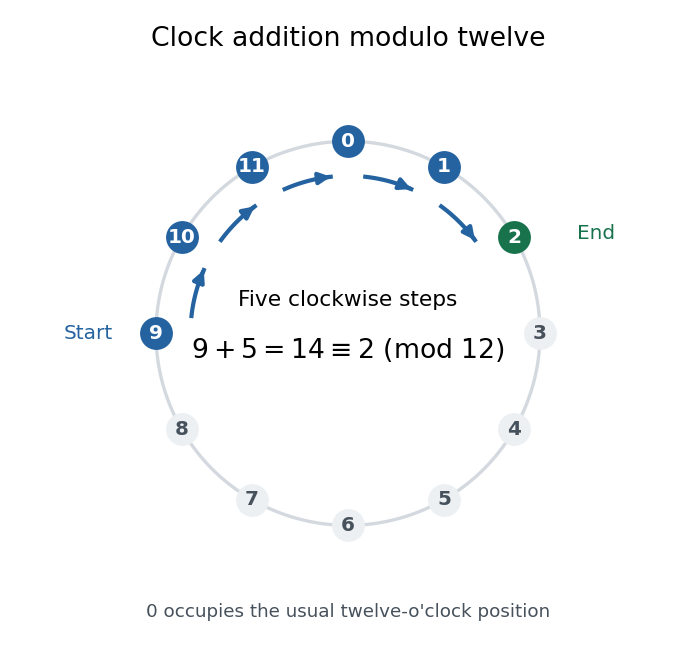
The same idea tracks any count repeating every steps. It also lets us compute sums and products with small residue classes, reducing intermediate results without changing the final class. The justification comes from addition and multiplication being well-defined on residue classes.
In Disquisitiones arithmeticae (1801), Carl Friedrich Gauss defines modular congruence by divisibility in article 1; article 2 describes the integers and adopts . These passages document his presentation and notation, without claiming that repeating remainders began in 1801. [ref]
https://la.wikisource.org/wiki/Disquisitiones_arithmeticae/Sectio_prima. Gauss, Disquisitiones arithmeticae, section I, articles 1–2; original text in the 1870 collected edition
A quadratic congruence is a modular congruence defined by a degree-two polynomial, with solutions sought among residue classes. For odd and invertible modulo , completing the square gives . A Jacobi symbol of for a coprime proposed square rules out solutions, whereas a Jacobi symbol of alone does not establish solubility for a composite modulus.
For a prime and , write . The binomial theorem shows is divisible by : the linear term contains the extra factor and every higher term contains at least . Iteration gives the displayed modular congruence for every , including . Applied to Fermat's little theorem, it yields .
For a positive modulus , a reduced residue system contains exactly one representative of each residue class coprime to . Its size is the Euler totient function . Multiplication by any unit modulo n permutes these classes, which proves the Fermat-Euler theorem after multiplying and cancelling their unit product.
A linear congruence asks for the integers satisfying , where are integers and . Let be their greatest common divisor. There are solutions exactly when divides . When solutions exist, there are exactly solution classes modulo , obtained from one solution byThe divisibility condition follows immediately from : every common divisor of must divide . Conversely, Bézout's identity constructs a solution when . Differences between any two solutions obey , equivalently , since and are coprime. This explains both the spacing and the number of solution classes.
For a complete example, solve . Here divides nine. Dividing the corresponding divisibility statement by three changes the integer modulus too:Because , multiplying by the modular inverse three gives . Lifting this class back to modulus fifteen yields . Direct substitution gives , and , each with remainder nine after division with remainder by fifteen. By contrast, has no solutions, because three does not divide ten.
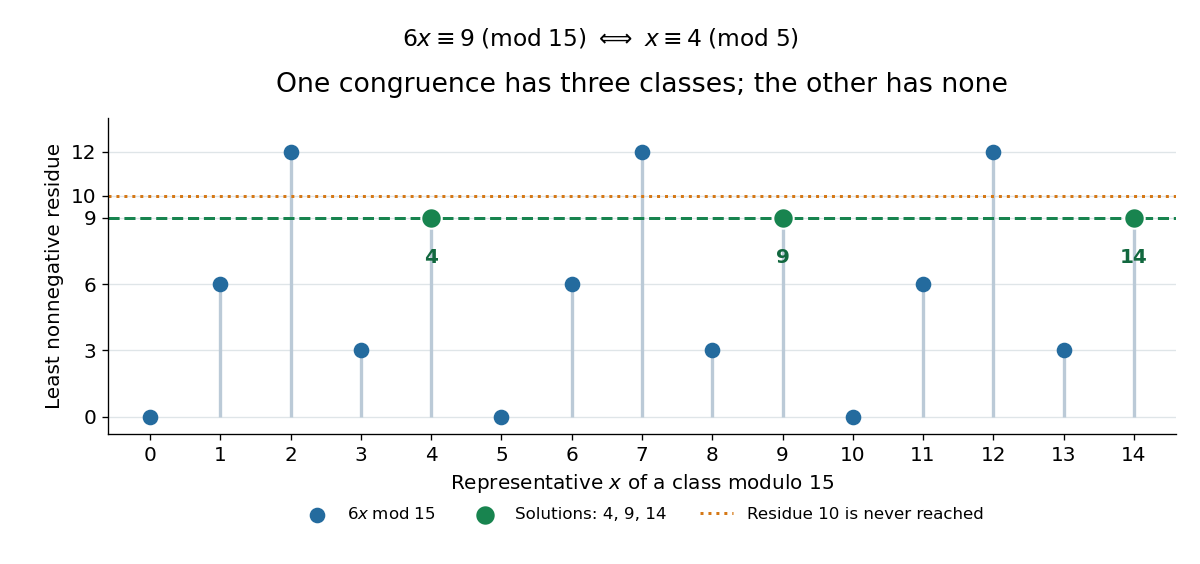


This is why ordinary-looking division cannot be performed blindly in modular arithmetic. Reducing the equation and its integer modulus together keeps all solutions; retaining modulus fifteen after dividing by three would lose valid classes. When , the modular inverse of exists and gives a unique class . The Euclidean algorithm computes the Bézout coefficients needed for this construction. [ref]
https://ocw.mit.edu/courses/18-200-principles-of-discrete-applied-mathematics-spring-2024/mit18_200_s24_lec15.pdf. Moitra, MIT 18.200, Lecture 15, modular inverses and the extended Euclidean algorithm
For integers and positive integers , a common factor may be cancelled from a integer congruence provided the modulus is divided by the corresponding greatest common divisor. Let , , and . The integers are coprime: any common divisor greater than one would give a common divisor of larger than .
By divisibility and Euclid's lemma,This proves the displayed equivalence. If is coprime to , the modulus stays unchanged and this is ordinary cancellation by a modular multiplicative inverse. If , the reduced modulus is , so every pair satisfies the reduced integer congruence.
For a positive integer modulus , the residue class of an integer is the equivalence classIt contains all integers in the same position of the repeating cycle. For example,The residue class is this whole infinite collection; its canonical representative is the least nonnegative residue. Euclidean division gives exactly one such representative in , so there are exactly residue classes. When , there is just one, .
Define addition and multiplication of residue classes byThese definitions must give the same answer whichever integers represent the classes. If and modulo , thenBoth differences are divisible by , proving that the operations are well-defined. For example, and , since . Replacing nine by gives the same answers with smaller intermediate integers.
With these operations the residue classes form the finite commutative ring , a quotient ring. It need not be a field: although neither factor is the zero class. These zero divisors explain why division requires a unit modulo n. Reducing after each multiplication is especially useful in modular exponentiation, where the unreduced powers can become enormous.
For a positive integer modulus , a residue class is a unit when it has a modular multiplicative inverse: some integer satisfies . Modulo twelve, the units are exactlyIn particular, five is its own modular inverse, since . Multiplying all twelve residue classes by five gives a permutation; multiplying the outputs by five recovers the inputs. By contrast, multiplying by six gives only zero and six, with six inputs for each output. It cannot be reversed.
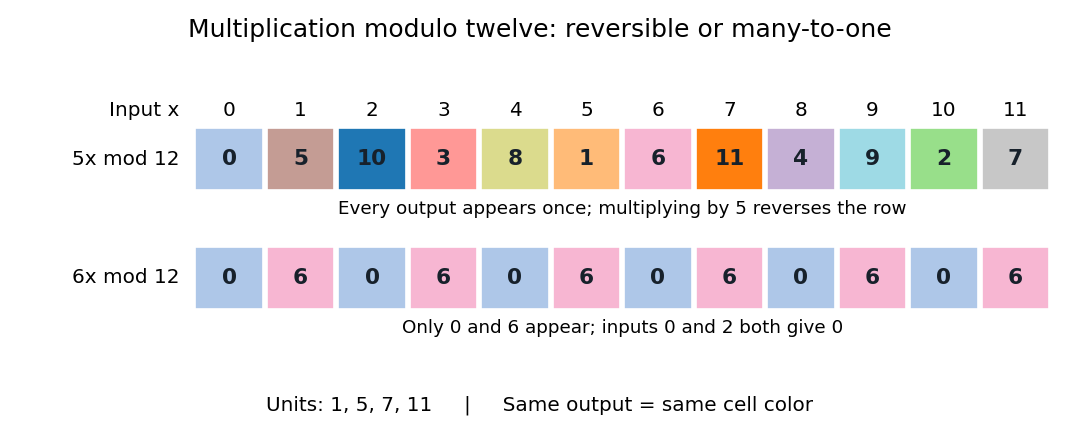
Multiplication by five permutes all twelve residue classes, whereas multiplication by six merges distinct inputs
. Details. 
In general, the exact criterion isFor the forward direction, implies every common divisor of divides one. Conversely, if their greatest common divisor is one, Bézout's identity supplies , so is a modular inverse. The extended Euclidean algorithm computes these coefficients. The units form the unit group under multiplication. [ref]
https://ocw.mit.edu/courses/18-200-principles-of-discrete-applied-mathematics-spring-2024/mit18_200_s24_lec15.pdf. Ankur Moitra, MIT 18.200, Lecture 15 (2024), pp. 3–4: inverses, coprimality and the unit group
Multiplicative cancellation while keeping the same integer modulus is valid for a unit modulo n: from , multiply by a modular inverse of to get . A nonunit cannot be cancelled as a general rule. For example, , yet . Thus division by six cannot undo this multiplication; solving a linear congruence instead keeps track of all possible classes.
This distinction marks the boundary between commutative rings and fields. Modulo a prime number , every nonzero residue class is a unit, so is a finite field. Modulo twelve it is a commutative ring with zero divisors, and is not a field. For , the sole class satisfies and is a unit; this one-element zero ring is not a field. [ref]
https://ocw.mit.edu/courses/18-200-principles-of-discrete-applied-mathematics-spring-2024/mit18_200_s24_lec15.pdf. Moitra, MIT 18.200, Lecture 15, pp. 8–9: the prime-modulus field criterion
Articles by others on the same topic
There are currently no matching articles.