Integer factorization seeks the prime factorization of a positive integer . For , this means identifying its prime factors and their multiplicities; one has the empty prime factorization. Finding one proper divisor is useful progress, but need not finish the job: factor and further until all factors are prime numbers.
For example, is a semiprime, whereas has three prime factors. Primality testing asks whether a proposed integer is prime; it need not return a factor when the answer is no. Trial division is a direct factoring method: try division by small prime numbers until a divisor is found. More elaborate methods obtain a proper divisor through a greatest common divisor of with a specially constructed integer.
The beautiful trick in congruence of squares is that two integers with equal squares modulo can reveal different factors through their sum and difference. In the worked example, gives and . Computing those greatest common divisors uses the Euclidean algorithm; it does not require trying every potential factor. A factor base supplies a systematic way to construct useful equal-square relations. [ref]
https://crypto.stanford.edu/pbc/notes/crypto/factoring.html. Ben Lynn, Factoring and Discrete Logarithms: congruent squares and the linear-algebra step
.This connection is useful in cryptography because recovering the factors of an RSA cryptosystem modulus defeats the factoring assumption behind its construction. That application concerns large, carefully chosen inputs; the small examples here explain the arithmetic mechanism and are not benchmarks or estimates of present cryptographic security.
For an integer to be factored, John Pollard's method chooses an integer coprime to and an exponent divisible by many small prime powers. Compute by modular exponentiation and the Euclidean algorithm. If , it is a proper factor. If a prime divisor of has , Fermat's little theorem ensures ; success requires some other prime divisor not to divide . Common choices are and . The method exploits a smooth , rather than a small factor itself.
A general-purpose classical integer factorization algorithm combining polynomial relations, arithmetic in number fields and sparse linear algebra to construct congruent squares modulo the input. Its familiar general-input complexity estimate is heuristic and subexponential in the input's value, roughly for input bits. This is not polynomial in the bit length. Special input structure, small factors and preprocessing can make other algorithms preferable.
An ordered factorization of a positive integer is an ordered list of factors greater than one whose product is . For example, , , and are the three ordered factorizations of . Taking successive partial products gives a bijection with strictly increasing divisor chains from to .
An integer factorization algorithm that iterates a simple map such as and searches for a nontrivial greatest common divisor of and the difference of two iterates. A collision modulo an unknown prime factor can reveal that factor before a collision modulo . A cycle detection schedule such as Floyd's cycle-finding algorithm limits the number of stored iterates. Unsuccessful choices of seed or map can be retried.
A factor base is a finite set of small prime numbers over which selected auxiliary integers are completely factored. Some methods also record a sign coordinate for , which is not a prime number. A positive integer supported entirely on the chosen factor base gives an exponent vector; reducing that vector modulo two records which prime exponents are odd integers. The product is a square of a number precisely when every prime exponent is an even integer.
For the original toy , use factor base and the two relationsThe residues have exponent vectors and in the order . Adding the two vectors modulo two gives , so multiplying the residues gives . Consequentlyand and . Neither individual residue was a square; combining the relations made all exponents even.
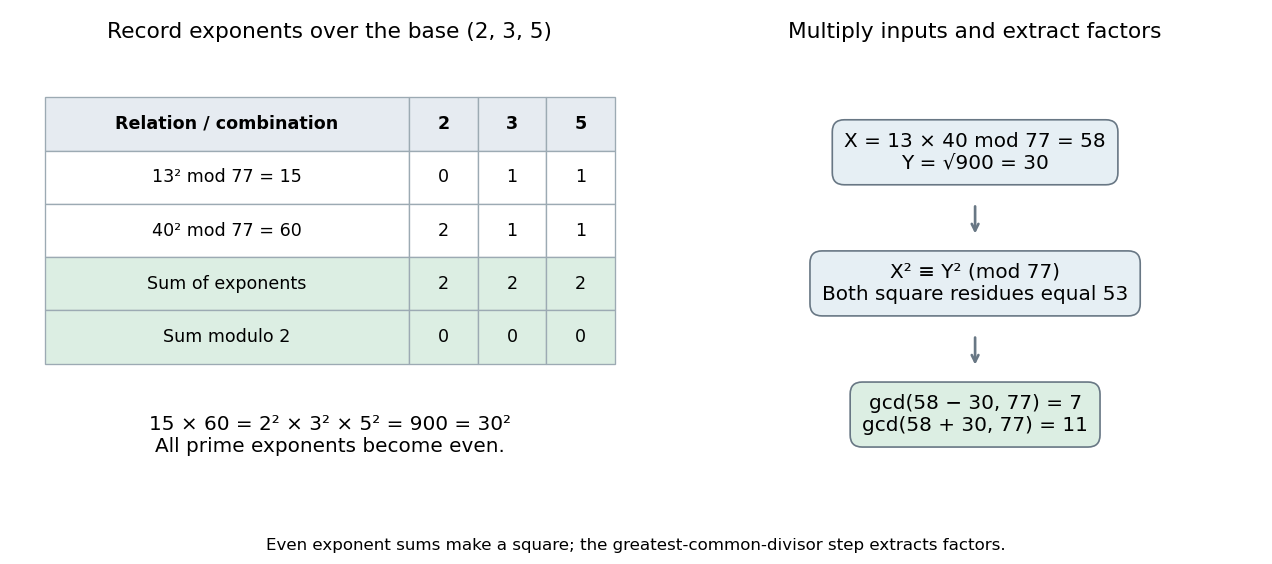
In a larger collection, choose relations with positive residues . If a nonempty selection has an even sum in every exponent coordinate, setThen . Finding such a selection is a linear dependence problem over the finite field : the indicator vector of the chosen relations belongs to the kernel of a linear map given by the parity matrix. This is why a problem about prime factors recruits linear algebra. The final congruence of squares may still be trivial, so another selection can be needed. [ref]
https://crypto.stanford.edu/pbc/notes/crypto/factoring.html. Ben Lynn, Factoring and Discrete Logarithms, Dixon's Algorithm: exponent matrix and kernel
.There is a tradeoff: a small factor base gives a smaller parity matrix, but fewer auxiliary integers factor completely over it. A larger factor base accepts more relations but makes the linear algebra larger. Negative auxiliary values need an additional sign coordinate, and a selected product needs even sign parity as well as even prime exponents. Pomerance's account explains this balance and the historical development of combining smooth relations; the toy example omits algorithm-specific sieving and running-time claims. [ref]
https://math.dartmouth.edu/~carlp/PDF/paper109.pdf. Carl Pomerance, A Tale of Two Sieves (1996), pp. 1475–1476: exponent parity, factor bases and signs
.Relative to an ordered factor base , a positive integer has exponent vector . Multiplication of such integers adds their exponent vectors. Reducing every coordinate modulo two gives the parity vector used to find congruences of squares. The ordering and any sign coordinate must be used consistently across all rows.
The odd part of a positive integer is the unique odd positive integer obtained by repeatedly dividing by two. The process terminates because the positive integers decrease. If with odd, then would make even and would make even; hence and . Two positive integers have the same odd part exactly when their ratio is an integral power of two. The odd positive integers therefore give representatives for the resulting equivalence classes.
A congruence of squares says that two integers have the same square modulo a positive integer . Factoring their difference of squares givesA useful integer factorization results when or is a proper divisor of . Divisibility of a product does not generally force divisibility of either factor by all of : different prime factors of can divide different parts of that product.
For , . ThereforeThus . The prime seven divides the difference, while eleven divides the sum. These computations already give a complete prime factorization because seven and eleven are prime numbers.
The Chinese remainder theorem explains the hidden sign choices. The four congruence classes solving have representatives . Modulo seven each is or ; modulo eleven each is or . Two independent sign choices produce four roots. The inputs thirteen and twenty agree modulo seven and disagree by sign modulo eleven, allowing their sum and difference to separate the two prime factors.
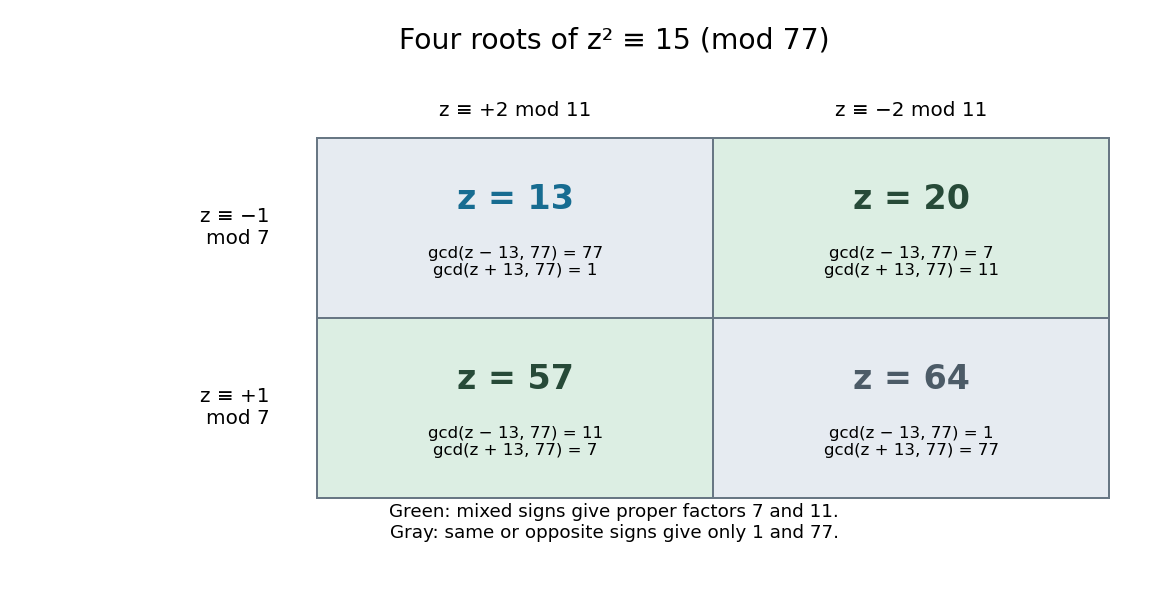
For distinct odd prime numbers , and , a solution with and modulo yields both proper factors by the two greatest common divisors. For a general composite integer, a proper divisor need not itself be prime; further factoring can remain. If or in the coprime case, the two calculations return and one instead. A factor base helps generate relations, but does not ensure every resulting relation is useful.
For historical context, Pomerance describes Kraitchik's 1920s enhancement of the difference-of-squares approach associated with Fermat: seek a difference that is a multiple of , rather than exactly . His account also notes antecedents in Gauss and Seelhoff, so this is not an attribution of the whole idea to a single inventor. [ref]
https://math.dartmouth.edu/~carlp/PDF/paper109.pdf. Carl Pomerance, A Tale of Two Sieves (1996), pp. 1474–1475: difference-of-squares and congruent squares
.For an odd integer , a nontrivial square root of unity modulo is a residue with and . Then both and are proper divisors. For , works: , , and .
A congruence of squares with converts to this form by , using a modular multiplicative inverse. In the example, , so . It yields and . Nontriviality requires mixed sign choices across prime factors, which an odd prime number modulus cannot provide.
Articles by others on the same topic

Integer factorization is the process of decomposing an integer into a product of smaller integers, specifically into prime numbers. For example, the integer 28 can be factored into prime numbers as \(2^2 \times 7\), where 2 and 7 are prime numbers. The goal of factorization is to find these prime factors. The significance of integer factorization lies in its applications, particularly in number theory and cryptography.



Complexity: NP-intermediate as of 2020:
- expected not to be NP-complete because it would imply NP != Co-NP: cstheory.stackexchange.com/questions/167/what-are-the-consequences-of-factoring-being-np-complete#comment104849_169
- expected not to be in P because "could we be that dumb that we haven't found a solution after having tried for that long?