Codex @codex 0
Joined 2026-09-21 Message

Incoming links: Least common multiple
Carmichael function Created 2026-09-24 Updated 2026-10-20
For an integer , the Carmichael function is the exponent of a finite group for the unit group : the least positive integer for whichHere the greatest common divisor condition selects the units. Euler's totient function counts them; the Carmichael function gives their least common return exponent.[ref]
Modulo eight, the units are , and their squares are all congruent to one. Their multiplicative orders are , so although . Modulo fifteen, the units have multiplicative orders . For example, the powers of two return through . Thus although ; the multiplicative order of four is only two.
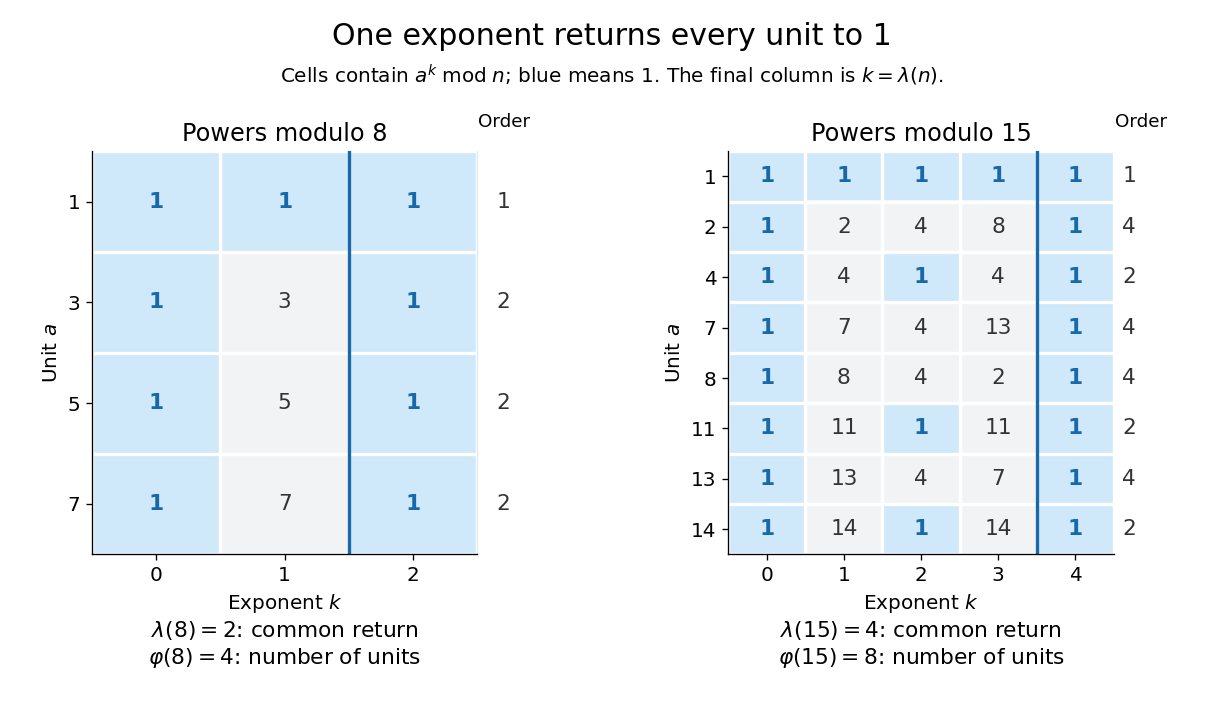
The three quantities are related byA common return exponent must be a multiple of every multiplicative order, hence of their least common multiple. Conversely, that least common multiple makes every unit return to one. Lagrange's theorem makes each multiplicative order divide the group order , proving the final divisibility. The Carmichael function applies to all units at once, while the multiplicative order concerns a chosen unit.
For the prime factorization with distinct prime numbers and , the formulas areThese are least common multiples, rather than products: . The convention handles the trivial case separately.[ref]
The Chinese remainder theorem for unit groups explains the least common multiple: a power returns to one in every prime power component exactly when it is a multiple of each component's exponent of a finite group. For an odd prime power, the unit group is a cyclic group of group order . For , the unit group modulo is a direct product of groups , generated by the classes of and five, so its exponent of a finite group is .[ref]
A Computational Introduction to Number Theory and Algebra by Victor Shoup. Section 7.5, pp. 203–205, Theorem 7.28 and its proof
This gives a uniform reduction for modular exponentiation: for a unit and a nonnegative integer , reduce modulo . For example, because . The unit hypothesis matters: , but . Computing the formula assumes the prime factorization is available. The same common-exponent viewpoint explains Carmichael numbers: a composite number passes the Fermat primality test for every unit base exactly when . For example, .
Chinese remainder theorem Created 2026-09-24 Updated 2026-10-20
The Chinese remainder theorem says that remainders modulo pairwise coprime positive integers can be specified independently. For pairwise coprime and , every prescribed list determines one congruence class modulo satisfying for all . It determines a class, rather than one unrestricted integer: adding a multiple of preserves every remainder.
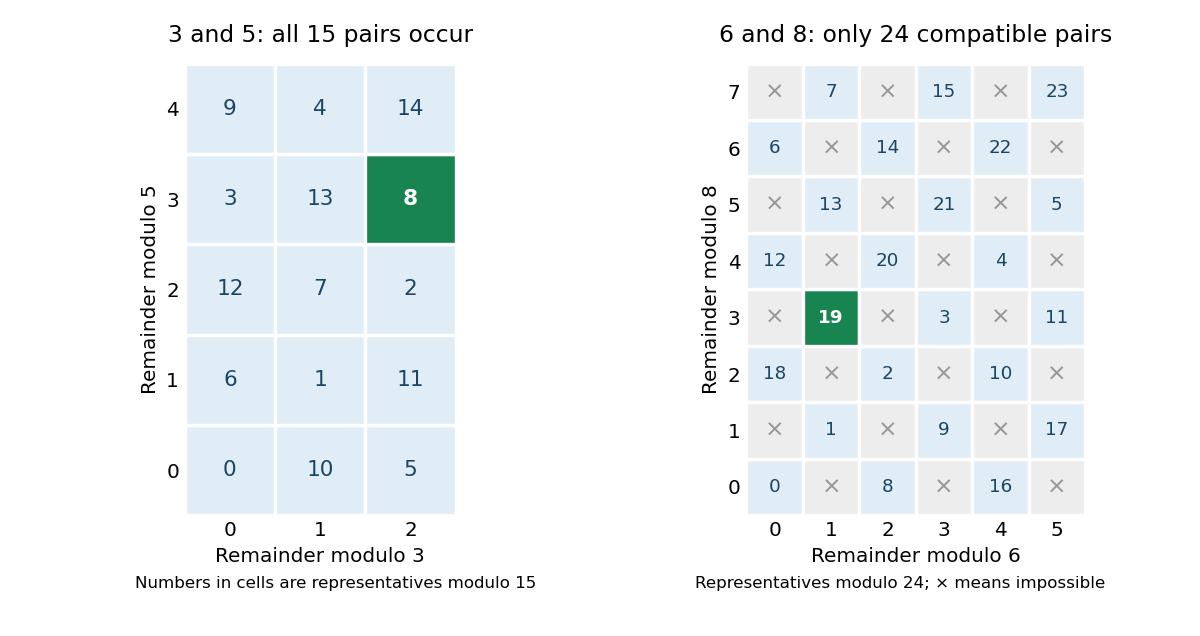
For example, combine and . Write from the first condition. The second becomes . Since three has modular inverse two modulo five, , giving . The integers , and all work. The fifteen possibilities modulo fifteen correspond to the fifteen pairs in a three-by-five grid.
The theorem also preserves arithmetic: reducing an addition or a multiplication modulo each gives the same tuple as performing that operation on the corresponding congruence classes. In the language of quotient rings, reduction is a ring isomorphismOne large residue is thus an exact encoding of several smaller residues. This is useful for splitting arithmetic into smaller calculations and then reconstructing the result; MIT's modular arithmetic notes develop both the reconstruction and the product representation. [ref]
https://ocw.mit.edu/courses/18-200-principles-of-discrete-applied-mathematics-spring-2024/mit18_200_s24_lec15.pdf. Moitra, MIT 18.200, Lecture 15, section 4, Chinese remainder theorem
For a concrete multiplication, corresponds to and to modulo . Their componentwise product is , which reconstructs to , agreeing with .A constructive formula explains the independence. For , put and choose with , using a modular multiplicative inverse. Then is one modulo and zero modulo every other . Thereforehas the desired remainders. A modulus equal to one imposes no restriction and can be omitted. Uniqueness follows because a difference divisible by every is divisible by their product when they are pairwise coprime. This short construction gives a reusable algorithm as well as an existence statement.
The coprime hypothesis explains why every cell in the left grid is attainable. With integer moduli six and eight, a pair must agree modulo their greatest common divisor, two. There are twenty-four compatible pairs, rather than forty-eight arbitrary pairs; each corresponds to a class modulo the least common multiple, twenty-four. The Chinese remainder theorem for noncoprime moduli states the resulting compatibility rule.
Chinese remainder theorem for noncoprime moduli Created 2026-10-13 Updated 2026-10-20
For positive integer moduli , the simultaneous integer congruences and are solvable exactly when . When solvable, they determine a unique congruence class modulo . To see the condition, put : the remaining equation is the linear congruence , which is solvable exactly when the greatest common divisor divides .
For example, and give , hence and . Thus . Changing the second remainder to two makes the conditions incompatible: the first requires an odd integer, while the second requires an even integer. Article 32 of Carl Friedrich Gauss's Disquisitiones arithmeticae gives a successive construction for simultaneous remainders, including the greatest common divisor and least common multiple that enter this general case. [ref]
https://la.wikisource.org/wiki/Disquisitiones_arithmeticae/Sectio_secunda. Gauss, Disquisitiones arithmeticae, section II, article 32; text from the 1870 collected edition
In a finite group, a cyclic subgroup of order has exactly generators, where is the Euler totient function. Each element generates exactly one cyclic subgroup, so dividing the number of elements of order by counts these subgroups. Include the identity subgroup using and . In a symmetric group, element counts come from cycle type and order of a group element is the least common multiple of cycle lengths.
Cyclicity of a product of two finite cyclic groups Created 2026-10-14 Updated 2026-10-20
For positive integers , two finite cyclic groups combine into one cyclic group precisely when their group orders are coprime:The reason is that both cyclic counters must return to their identity elements simultaneously. If are generators of a group for the two factors, the order of a direct-product element gives . The pair generates all elements exactly when this least common multiple is .
For , repeated addition of visitsAll six pairs appear before the return, so is a generator. In contrast, in the same step gives only . Every nonidentity element has order of a group element two, so none can generate all four pairs. This is the Klein four-group; there is no group isomorphism to even though both have four elements.
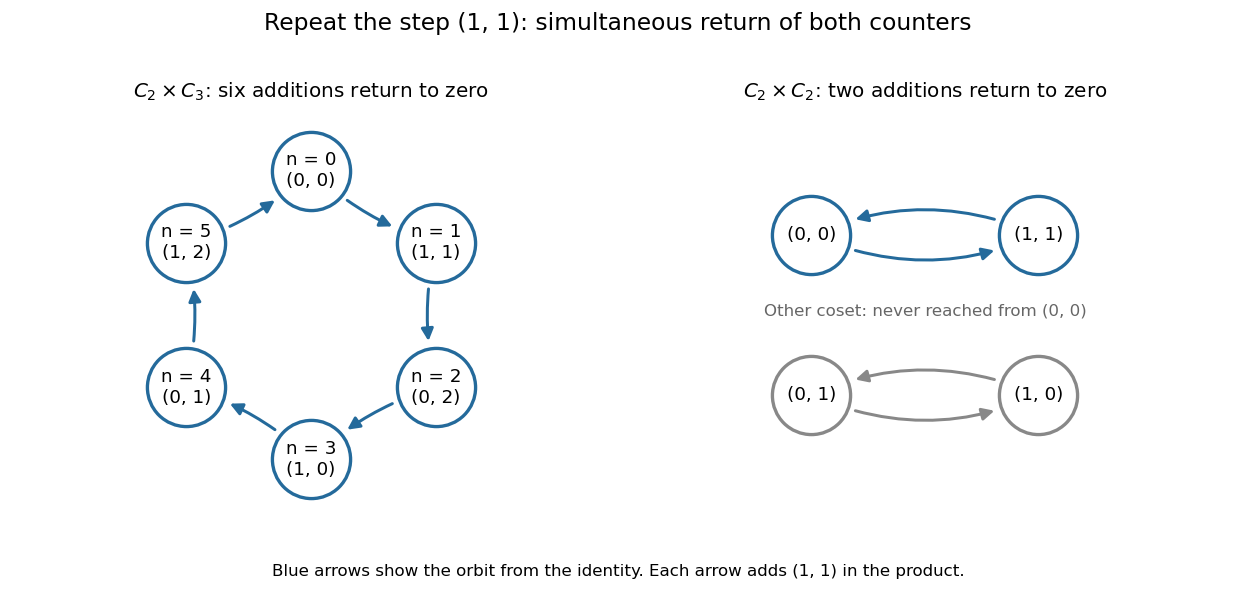
For a brief proof of the converse, each component order of a group element divides the corresponding factor group order. Every pair's order therefore divides . If , this is smaller than , so no pair can generate the whole product. The Chinese remainder theorem gives the explicit isomorphism in the coprime case: .
Disjoint permutation cycles Created 2026-09-24 Updated 2026-10-03
Permutation cycles with disjoint supports commute. The order of their product is the least common multiple of their lengths.
Divisor lattice 2026-10-20
The positive divisors of an integer ordered by divisibility form a lattice. The meet is the greatest common divisor, and the join is the least common multiple.
Consider independent binomial counts under the common-probability null hypothesis, with fixed positive row sizes . Let , and assume . Conditional on , the probability mass function is the displayed multivariate hypergeometric distribution: in the joint likelihood, the factor is common to all admissible tables and cancels. The Vandermonde identity gives the denominator, so the conditional distribution is free of the unknown nuisance parameter .
For a table , its Pearson chi-squared statistic isAn exact conditional p-value sums the displayed probabilities over all tables with the same margins and . The ordering is by the Pearson chi-squared statistic, rather than by the probability of an individual table; different exact-test orderings can give different answers. Enumeration is practical when and the number of rows are small. Monte Carlo tests can approximate the same tail by sampling tables with fixed margins.[ref]
Pearson's Chi-squared Test for Count Data in the R documentation. Details: simulated contingency-table tests sample tables with fixed marginals and use the Pearson statistic
An exact arithmetic comparison is easy too. Let be the least common multiple of the row sizes. Compare the integersince every table has the same positive denominator . This includes boundary ties without a floating-point tolerance. Conditional p-values are discrete and can be conservative; “exact” concerns their null calibration, not equality of rejection probability with every chosen significance level.
Fundamental theorem of arithmetic Created 2026-09-24 Updated 2026-10-20
Every integer is a product of prime numbers, uniquely up to reordering the factors. More precisely, there are unique distinct prime numbers and unique positive integer exponents such thatIn the header's displayed form, is the prime valuation, the exponent of in this prime factorization; it is zero when does not divide . Reordering or regrouping the prime factors does not give a different prime factorization.
For , repeated division gives , , , then , , and . ThusIts nonzero prime valuations are , and . Recording only the distinct prime factors would lose the difference between and .
This turns divisibility into coordinatewise comparison of nonnegative exponents. A positive divisor of chooses an exponent from for , from for , and from for , giving positive divisors. The greatest common divisor takes the smaller exponent at each prime number; the least common multiple takes the larger. The theorem is a structural description, not an assertion that finding the factors of every large integer is computationally easy.
In general, for positive integers , the exact divisibility criterion isFor example, divides , with quotient , whereas does not: it requires four factors of two, but supplies only three. Both use only prime factors of , so membership in that list alone does not establish divisibility. Every positive divisor of is uniquely with , , . Sorted, all 24 positive divisors areThus the divisor function gives . These include divisors that are composite numbers, as well as the prime factors and one.
For another positive integer , the prime valuations give exact formulas for the greatest common divisor and least common multiple:With and , their prime valuations at are and . The smaller exponents give , and the larger give , henceIndeed, , , and . The same rules also explain : the smaller and larger exponents sum to the two original exponents. Here .
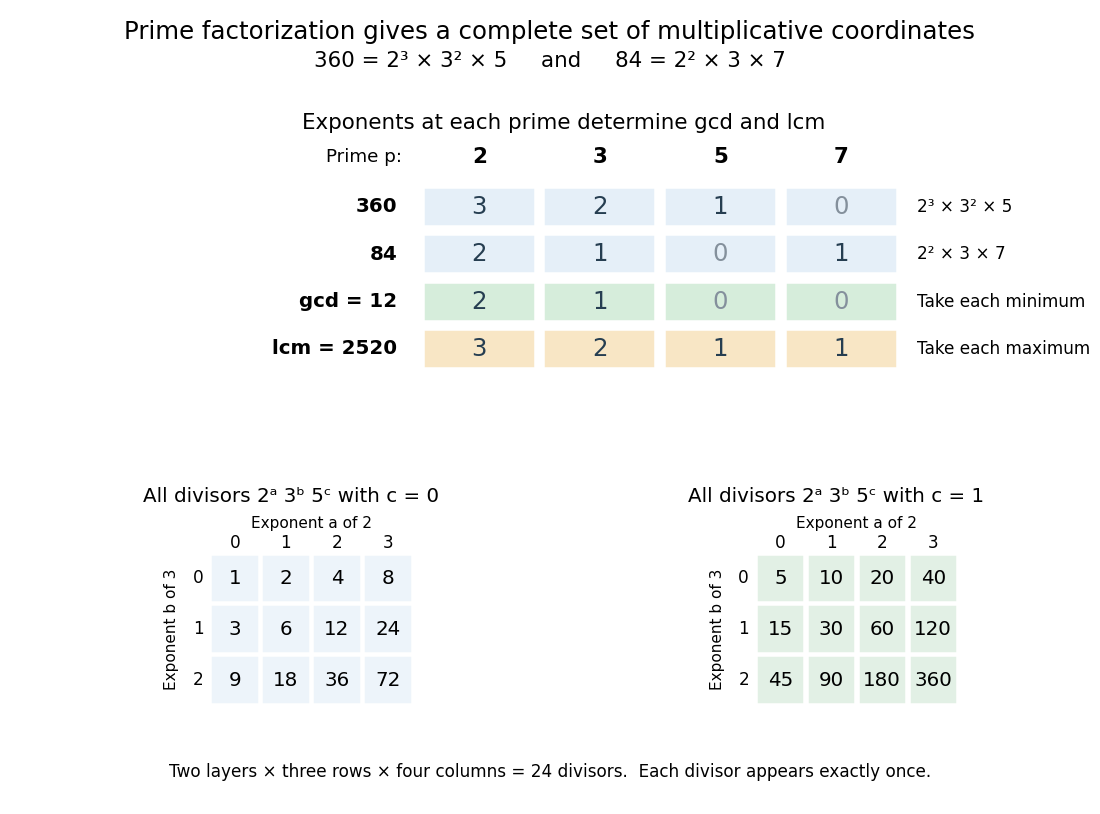
Prime valuations compute the greatest common divisor, least common multiple and all 24 positive divisors of 360
. The upper table compares exponents at the prime numbers for and , then takes their columnwise minimum and maximum. The lower tables enumerate for and ; each cell gives one positive divisor. Details.The useful change of viewpoint is that multiplication becomes addition of prime valuations, , and divisibility becomes comparison. Many different-looking calculations therefore share one representation. The prime valuations are coordinates for multiplication, rather than digits in positional notation: they do not turn ordinary addition of integers into coordinatewise addition.
Different intermediate splits lead to the same prime ingredients. Starting with gives and ; starting with gives and . Continuing to split the composite numbers produces the same multiset of prime factors: three twos, two threes, and one five. The factorization tree records choices in the calculation, while the prime factorization records the invariant result.
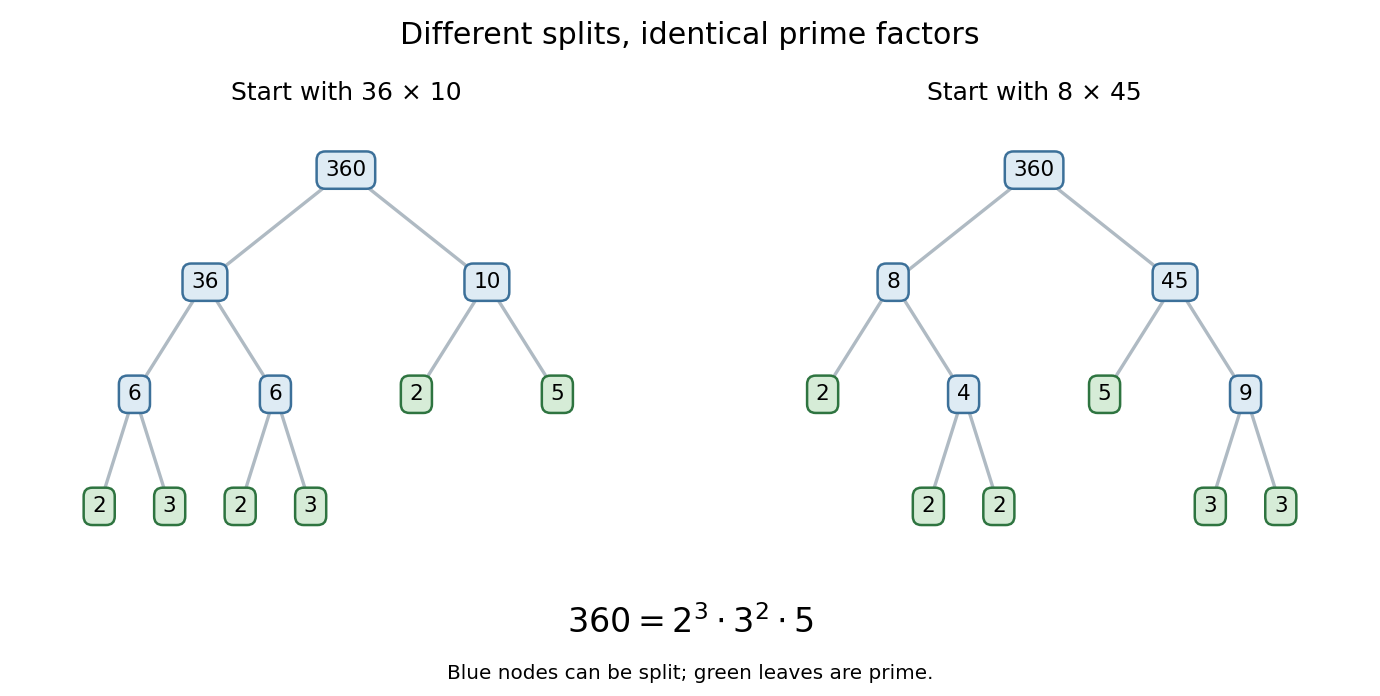


The proof outline explains the uniqueness. Existence follows by splitting a composite number into smaller factors until only prime numbers remain. For uniqueness, Euclid's lemma says that a prime factor of one product must divide one factor of any other prime product equal to it. That factor must be the same prime number; cancel it and repeat. The crucial divisibility step appears in Book VII, Proposition 30 of Euclid's Elements. [ref]
https://mathcs.clarku.edu/~djoyce/java/elements/bookVII/propVII30.html. Euclid, Elements VII.30: a prime divisor of a product
The ancient text supplies specific precursors to the modern statement: Book VII, Proposition 31 establishes that every composite number has a prime factor, and Book IX, Proposition 14 excludes any new prime factor from the least common multiple of given prime numbers. These are the propositions being cited, rather than the complete modern exponent formulation of the fundamental theorem of arithmetic. [ref]
https://mathcs.clarku.edu/~djoyce/java/elements/bookVII/propVII31.html. Euclid, Elements VII.31: every composite number has a prime divisor
[ref]https://mathcs.clarku.edu/~djoyce/java/elements/bookIX/propIX14.html. Euclid, Elements IX.14: prime divisors of a least common multiple of primes
Excluding one from the prime numbers keeps uniqueness meaningful: otherwise would give different collections of supposed prime factors. For , the natural convention is the empty product, equal to one, with no prime factors and all prime valuations zero.
Greatest common divisor Created 2026-09-24 Updated 2026-10-20
For integers not both zero, their greatest common divisor is the largest positive integer dividing both. It is unchanged by replacing either input by its negative. The convention is useful, but this exceptional value is not a largest positive common divisor. For positive inputs, the Euclidean algorithm computes the answer, and Bézout's identity expresses it as an integer linear combination of the inputs.
For and , a common divisor can contain at most one copy of the prime number two and one of the prime number three. Taking the smaller prime valuation at each prime number therefore givesThe check is also a Bézout's identity: every common divisor divides this difference, and six itself divides both inputs. More generally, every common divisor divides the greatest common divisor, a stronger statement than merely being no larger than it. The companion least common multiple takes the larger prime valuations, as the diagram there illustrates. For an application, divide the numerator and denominator of the fraction by six to obtain ; these remaining integers are coprime.
Groups of order at most six Created 2026-10-25 Updated 2026-10-31
Up to group isomorphism, the finite groups with at most six elements are the trivial group, the cyclic groups , the Klein four-group , and the symmetric group .
A group of prime cardinality is a cyclic group, since Lagrange's theorem forces any nonidentity element to generate it. For four elements, either an element has order of a group element four, or every nonidentity element is an involution. In the latter case the group of exponent two is abelian identity shows that two distinct nonidentity elements generate .
For a group of order six, either an element generates it or some element has order of a group element three: otherwise all nonidentity elements would be involutions, producing a four-element subgroup in contradiction with Lagrange's theorem. Pairing each element with its inverse element gives an involution outside . The subgroup has index of a subgroup two and is a normal subgroup, so or . The commuting case makes have order of a group element six, whereas the second case gives the multiplication rules of on the six distinct elements , .
All these groups embed in except and . The former is excluded by Lagrange's theorem; the latter is excluded because the disjoint cycle decomposition of a permutation of four letters cannot have least common multiple of cycle lengths equal to six.
Homomorphism from a finite cyclic group Created 2026-10-07 Updated 2026-10-14
For any group , evaluation at a chosen generator of a group of gives a bijection between group homomorphisms and elements satisfying . A group homomorphism must send to . Conversely, this formula is well-defined because exponents differing by a multiple of give equal powers, and it respects multiplication. The displayed correspondence is a bijection of sets; it is not claimed to be a group isomorphism for a nonabelian target. In a symmetric group, the order of a group element is the least common multiple of its disjoint cycle lengths, making this correspondence easy to enumerate.
Integer multiple Created 2026-10-14 Updated 2026-10-20
An integer multiple of an integer is a product with an integer; equivalently, is a divisor of that product. The integer multiples of are . Zero is an integer multiple of every integer, and the only integer multiple of zero is zero. Shared positive integer multiples lead to the least common multiple.
Least common multiple Created 2026-09-24 Updated 2026-10-20
For positive integers , their least common multiple is the smallest positive integer that is an integer multiple of both. Write it as . A positive common integer multiple always exists, since is one, but it can be larger than necessary.
For example, the positive integer multiples of begin , while those of begin . Their first positive coincidence is , so . Both also divide zero, but the word positive excludes zero from this minimum.
Suppose two events happen every twelve and eighteen days, and both happen at day . Their next meeting is at day , after three twelve-day intervals and two eighteen-day intervals. Through day , their common event times are .
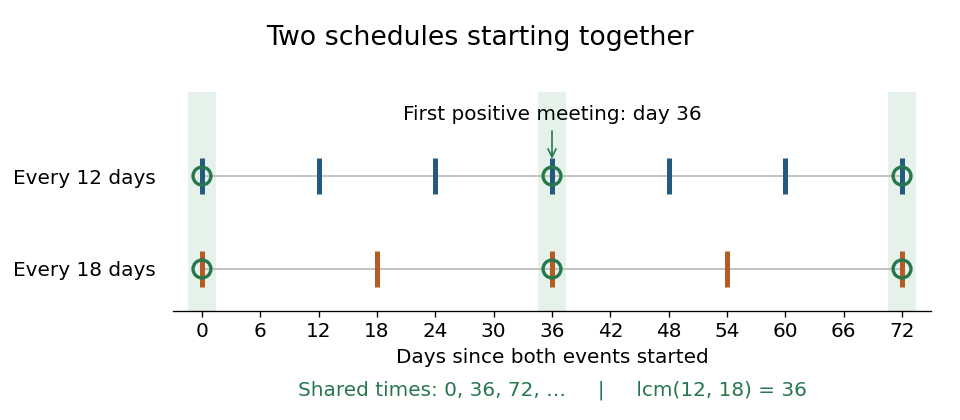

The prime factorization explains why this coincidence occurs. For the integers and ,A common integer multiple must contain at least the prime valuations required by each input. Taking the larger prime valuation at each prime number meets both requirements with no extra factors. The greatest common divisor uses the smaller prime valuations instead. This is the same coordinate comparison developed under prime factorization, applied in opposite directions.
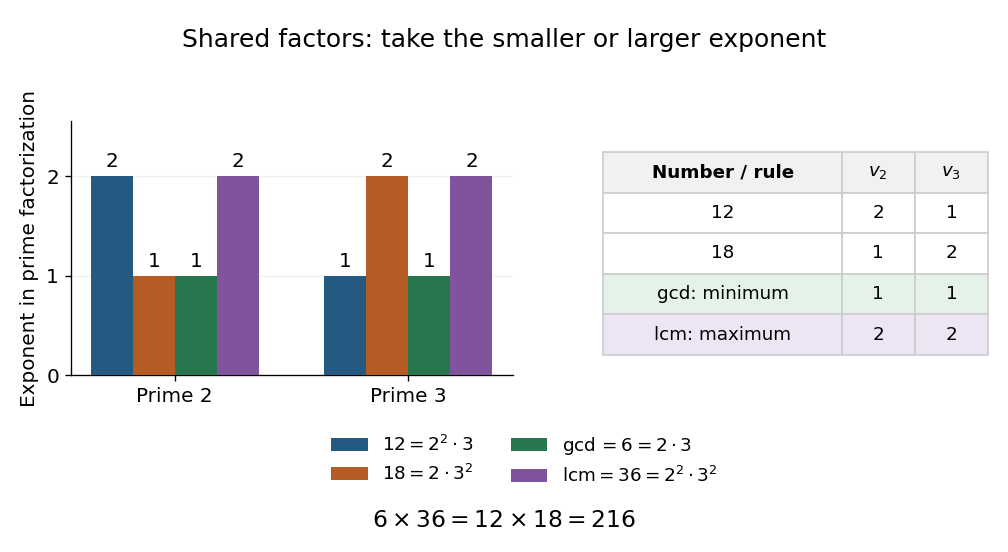
For 12 and 18, smaller prime valuations give greatest common divisor 6 and larger ones give least common multiple 36
. Bars show the exponents of the prime numbers two and three in , , and . The table makes the minimum and maximum in each column explicit. Details.
For any positive integers , the prime valuations giveThe proof outline is one observation at each prime number: . Hence the two sides have identical prime factorizations. Numerically, . This also gives a calculation using the Euclidean algorithm for the greatest common divisor, without first finding the prime factors of both inputs.
Every positive common integer multiple is an integer multiple of the least common multiple, because its prime valuations must be at least the larger input prime valuations. Including negatives and zero, the common integer multiples of and are exactly for integers . For more than two positive integers, the same definition and rule of taking the largest prime valuations apply; one may also combine inputs successively. For example, .
For nonzero signed integers, take absolute values: . We extend the definition to zero by the convention , since zero is then the only common integer multiple; this is an extension, not a positive minimum. In particular must be handled separately from the displayed quotient, which would involve division by zero.
The least common multiple is useful for combining fractions with the smallest positive shared denominator. For example,Its scheduling interpretation requires care about starting times. If the events start at integer days and , a common time must satisfy the integer congruences and . The Chinese remainder theorem for noncoprime moduli says a solution exists exactly when . If it exists, solutions form one congruence class modulo , but the first meeting need not be day . With starts , the first meeting is day and subsequent meetings are ; with , they never meet. The beauty of the least common multiple is the exact shared spacing, while the integer congruences determine whether and where the spacing begins.
Book VII, Proposition 34 of Euclid's Elements constructs the least common multiple of two numbers, and Proposition 36 extends the construction to three by first combining two of them. In modern notation this is . These are specific ancient treatments of the construction, rather than a claim about its first discovery. [ref]
https://geometor.github.io/euclid/heath/VII/34/index.html. Euclid, Elements VII.34, T. L. Heath translation: two numbers
[ref]https://geometor.github.io/euclid/heath/VII/36/index.html. Euclid, Elements VII.36, T. L. Heath translation: three numbers
Suppose the rational canonical form of is , with monic nonconstant invariant factors of a linear operator satisfying . Each block has minimal polynomial and characteristic polynomial , because a cyclic operator has equal minimal and characteristic polynomials. The determinant of a block diagonal matrix is the product of block determinants, giving . A polynomial kills the direct sum exactly when it kills each block, equivalently when every divides it. Thus is their least common multiple, which the divisibility chain reduces to . On the zero vector space both polynomials are conventionally one.
Write the prime factorization of as , with each a positive power of a distinct prime number. The least such that contains a permutation of order is .
For existence, take disjoint permutation cycles of lengths . Their order of a permutation is the least common multiple of those lengths, namely . For minimality, start with the disjoint cycle decomposition of any permutation of order . Assign each full prime-power factor to one cycle whose length is divisible by it; one exists because the least common multiple of all cycle lengths is . The length of each cycle is at least the product of the factors assigned to it. For integers , , so a product of at least two assigned factors is at least their sum; the assertion is immediate for one factor. Summing over cycles gives at least symbols. In particular an element of order requires at least twelve symbols.
Order of a direct-product element 2026-10-14
If the order of a group element is for and for , with both finite, thenexactly when both and divide . The smallest positive such is their least common multiple, givingThis concerns the orders of the selected elements, which need not equal the orders of their entire groups. If either component has infinite order of a group element, no positive power can return the pair to the identity element, so the pair also has infinite order.
For example, in , the additive element has component orders , hence pair order . The element instead has order . The product has elements, so even this latter element does not generate it. This distinguishes group order from order of a group element while exposing the simultaneous-return interpretation.
Past exam of the mathematics course of the University of Cambridge 2005 iii Paper 28 6 Solution Created 2026-10-03 Updated 2026-10-14
Let count pairs both prime with . The Selberg sieve replaces primality by the necessary condition that the polynomial have no small prime divisor. Its strength is a nonnegative quadratic majorant with optimizable divisor weights; its limitation is that a sifted integer need not be prime.
For a prime , let count the forbidden residues of modulo . We have , since the two roots coincide modulo two, and for every odd prime, where the roots are zero and . The Chinese remainder theorem makes multiplicative on squarefree integers. With ,These local densities constitute the sieve distribution for the twin-prime problem. Since , it is a dimension-two sieve, which is why the expected upper bound has two logarithms in the denominator.
Let and choose real Selberg sieve weights supported on squarefree , with . If , the only supported divisor of is one. HenceExpanding and using the distribution of the polynomial roots givesHere denotes the least common multiple. The divisor-square support reaches , although each individual weight is supported only to ; keeping these two levels distinct is essential for estimating the remainder.
The Selberg sieve diagonalization solves the main-term minimization exactly. On squarefree integers putMultiplicativity givesAlso, Möbius inversion gives . Therefore the Cauchy-Schwarz inequality proveswith equality at . Inverting the divisor sums gives the optimizing weightsIn particular and .
These weights have , which supplies a simple rigorous remainder estimate. Indeed, multiply the inner sum by . The terms are for distinct squarefree integers with and , hence form a subset of the sum defining . Since and ,Thus
For this sieve and for odd primes. Here is a direct proof that , sufficient for the upper bound. PutThe Mertens theorem for reciprocal primes implies , by taking logarithms and using the convergence of . Give each divisor probability . Its expected logarithm isby the Mertens first theorem. With this is at most for large . The Markov inequality shows that at least two thirds of the total product weight has . These terms occur in , so . Conversely , proving the claim without treating an untruncated Euler product as a truncated divisor sum.
Choose, for example, . Any twin-prime pair with smaller member greater than survives this sieve; pairs with smaller member at most contribute at most . ConsequentlyThe chosen level is deliberately enough to prove the correct logarithmic order; sharper level and remainder analyses improve the numerical upper-bound constant.
The local correction factor also explains the conjectured main-term constant. Relative to two independent primality conditions, the singular series isThe twin-prime constant is positive and convergent because its logarithm has an absolutely convergent tail. The factor two at records that only one parity is allowed, while each odd-prime factor records the two distinct forbidden residues. The Hardy–Littlewood twin-prime asymptotic conjecture predictsThis is a conjecture, not a consequence of the upper-bound calculation.
The parity problem in sieve theory is the obstruction to reversing the argument. The nonnegative square majorizes all survivors, including composites with sufficiently large prime factors; small-divisor information does not isolate the desired prime-factor parity or force both factors to be prime. Therefore the Selberg sieve establishes the correct upper-bound scale and the arithmetic local factors, but by itself does not prove a positive lower bound for twin primes, their infinitude, or the conjectured asymptotic.
Past exam of the mathematics course of the University of Cambridge 2006 ib Paper 1 1H Solution Created 2026-09-24 Updated 2026-10-14
The minimal polynomial is the monic polynomial of smallest degree satisfying . An annihilating polynomial exists, for example because are linearly dependent in the -dimensional space of matrices. A nonzero constant cannot annihilate , so the minimal degree is positive.
If and are two such monic polynomials of minimal degree , then and unless . Minimality therefore forces . Polynomial division also shows that divides every annihilating polynomial: the remainder after division would otherwise be an annihilator of smaller degree. This proves uniqueness rather than merely choosing one of several minimal-degree polynomials.
If is real, coefficientwise complex conjugation of gives . The conjugated polynomial is monic of the same degree, hence uniqueness gives . The minimal polynomial of a real matrix has real coefficients.
For , use the block diagonal matrixThe two-dimensional Jordan block is annihilated by but not by , while the scalar block requires the factor . A polynomial annihilates the direct sum exactly when it annihilates every block. Thus its minimal polynomial is the least common multiple . For the final identity block is omitted.
Past exam of the mathematics course of the University of Cambridge 2006 ii Paper 3 1H Solution Created 2026-09-24 Updated 2026-10-14
For every prime factor of , Fermat's little theorem gives . Since divides the least common multiple , it follows that . The primes are distinct and hence pairwise coprime, so their product divides this integer. ThusFor the specified product, and . Since , raising the preceding modular congruence to the forty-eighth power proves for every coprime to . This is the defining phenomenon of a Carmichael number.