
f-divergence Created 2026-09-24 Updated 2026-09-24
For a convex function satisfying , the f-divergence between probability distributions and iswhere , , and the integrand uses the lower-semicontinuous perspective convention at .
Sign test Created 2026-09-24 Updated 2026-09-24
Survival analysis Created 2026-09-24 Updated 2026-10-13
Survival analysis studies the probability distribution of a survival time: how long from a specified starting point until a specified occurrence. The occurrence need not be death. It might be a machine's first breakdown, a customer's first renewal, or a person's recovery. The meaning of "survival" is simply that the chosen occurrence has not happened yet. Both the starting point and the outcome must be defined before interpreting a survival function.
The distinctive difficulty is incomplete observation. A machine still working when observation stops supplies a lower bound on its survival time, rather than an observed breakdown time. Right censoring lets us retain that information. The Kaplan–Meier estimator estimates a survival function using the changing risk sets, without choosing an exponential distribution or another particular survival distribution. A hazard function instead describes the current event rate among those still event-free; its cumulative hazard connects those local rates to the whole survival function.
This framework turns different follow-up lengths into usable evidence about waiting times. It supports questions such as the chance of remaining event-free for another year, or the restricted mean survival time within an observed horizon. Lu Tian's Stanford teaching materials introduce these interpretations in Survival Distributions, Hazard Functions, Cumulative Hazards, Section 1.1.
Clinical trial Created 2026-09-24 Updated 2026-09-28
Causal inference Created 2026-09-24 Updated 2026-09-24
Causal inference studies effects of interventions by comparing potential outcomes under different treatments.
Conditional multivariate normal distribution Created 2026-09-24 Updated 2026-10-03
Augmented inverse-probability-weighted estimator Created 2026-09-24 Updated 2026-09-24
Positive-semidefinite kernel Created 2026-09-24 Updated 2026-10-18
A symmetric function is a positive-semidefinite kernel when every finite Gram matrix is positive semidefinite.
Power spectrum Created 2026-09-24 Updated 2026-10-03
The power spectrum describes how the variance of a random field or stationary process is distributed over spatial wavenumber or temporal frequency.
Small oscillations of a hoop with a sliding bead Created 2026-09-24 Updated 2026-10-06
For equal hoop and bead masses, with the hoop suspended from its circumference, the quadratic mass and stiffness matrices are proportional toThe dimensionless squared frequencies are the roots of , namely and .
Sum of two squares theorem Created 2026-09-24 Updated 2026-10-20
A positive integer is a sum of two integer squares exactly when every prime factor congruent to modulo has even exponent in its prime factorization.
Euclidean algorithm Created 2026-09-24 Updated 2026-10-20
For positive integers , the Euclidean algorithm repeatedly performs division with remainder: write with , then replace by until the second entry is zero. The final nonzero entry is their greatest common divisor. A remainder preserves the set of common divisors: an integer divides and exactly when it divides and . The positive remainders strictly decrease, so the calculation terminates.
The complete calculation for and isHence . The fraction reduces to by dividing numerator and denominator by that common factor. The same remainder calculation has a geometric interpretation: remove squares from a -by- rectangle, then repeat on the remaining strip. Each division step records how many equal squares fit and the width of the new strip.
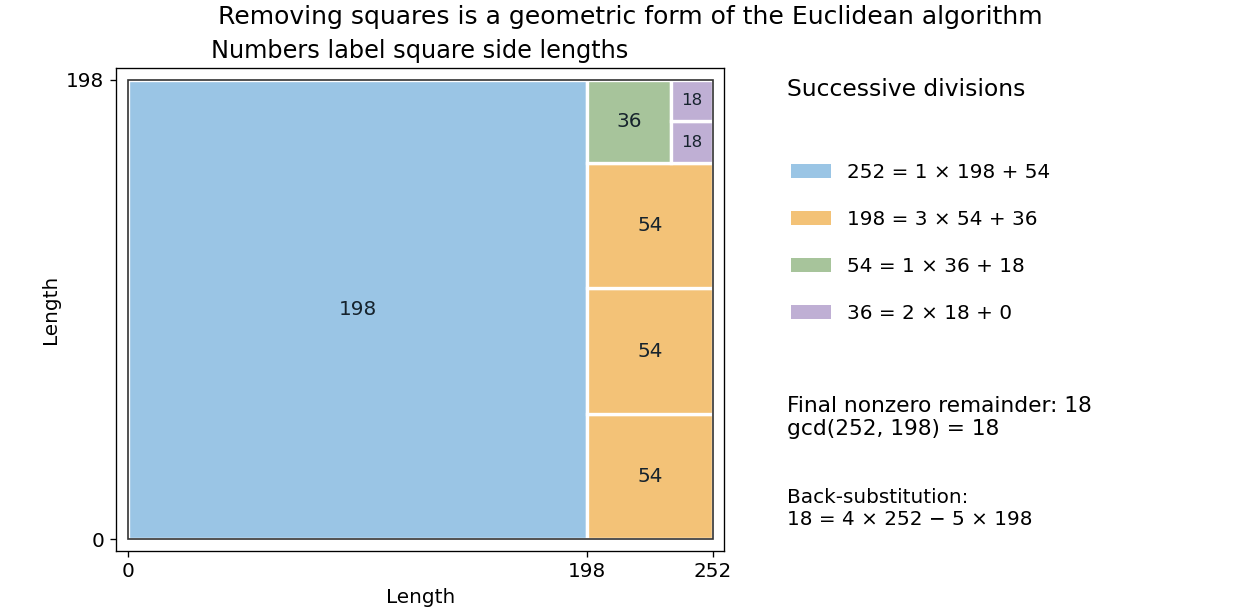
Successive square removals record the Euclidean algorithm for 252 and 198
. Details. The procedure does more than test individual divisors. Each step replaces the whole common-divisor problem by a smaller equivalent one. Euclid's Book VII, Proposition 2 describes the corresponding repeated-subtraction construction; batching those subtractions into division with remainder gives the present formulation. [ref]
https://mathcs.clarku.edu/~djoyce/java/elements/bookVII/propVII2.html. Euclid, Elements VII.2, greatest common measure
Multiplicative order Created 2026-09-24 Updated 2026-10-13
For coprime integers with , the multiplicative order is the least positive integer such thatIt counts the distinct powers in the cyclic subgroup generated by the congruence class of . Thus it is an order of a group element in the unit group .[ref]
A Computational Introduction to Number Theory and Algebra by Victor Shoup. pp. 153 and 156–157, Theorem 6.29
For example, the modular exponentiation , starting at , produces . The first return to one takes three steps, so . Starting at the congruence class three and repeatedly multiplying by two instead gives : these are the other three units modulo seven, outside the cyclic subgroup generated by two.
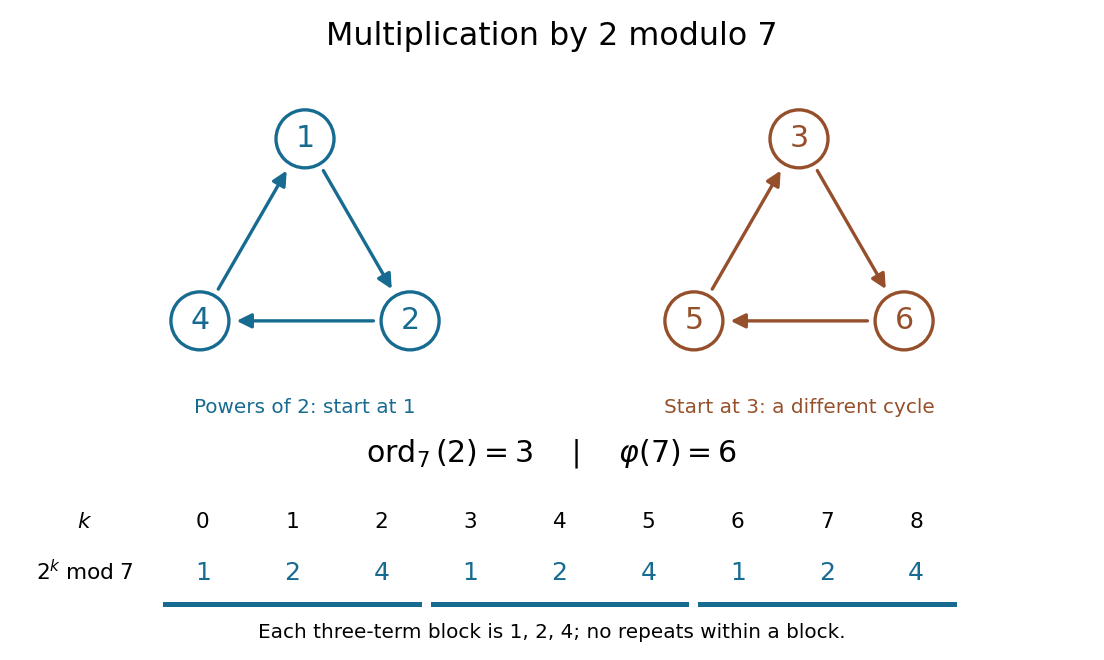
Euler's theorem guarantees a return to one at exponent , where is Euler's totient function. Thus the multiplicative order exists for every unit.[ref]
Euler’s Theorem by Keith Conrad. p. 1, Theorem 1.2; pp. 2–3, permutation of the units and cancellation
In fact,By Lagrange's theorem, the size of the cyclic subgroup divides the size of the unit group, which is Euler's totient function. For two modulo seven, this is ; the multiplicative order need not equal Euler's totient function. If , its multiplicative order is one.The coprime integers hypothesis is necessary: if , any common divisor of and divides one. For instance, powers of two modulo eight give , with no positive-exponent return to one. This sequence eventually settles, but two has no multiplicative order modulo eight.
Carmichael function Created 2026-09-24 Updated 2026-10-20
For an integer , the Carmichael function is the exponent of a finite group for the unit group : the least positive integer for whichHere the greatest common divisor condition selects the units. Euler's totient function counts them; the Carmichael function gives their least common return exponent.[ref]
Modulo eight, the units are , and their squares are all congruent to one. Their multiplicative orders are , so although . Modulo fifteen, the units have multiplicative orders . For example, the powers of two return through . Thus although ; the multiplicative order of four is only two.
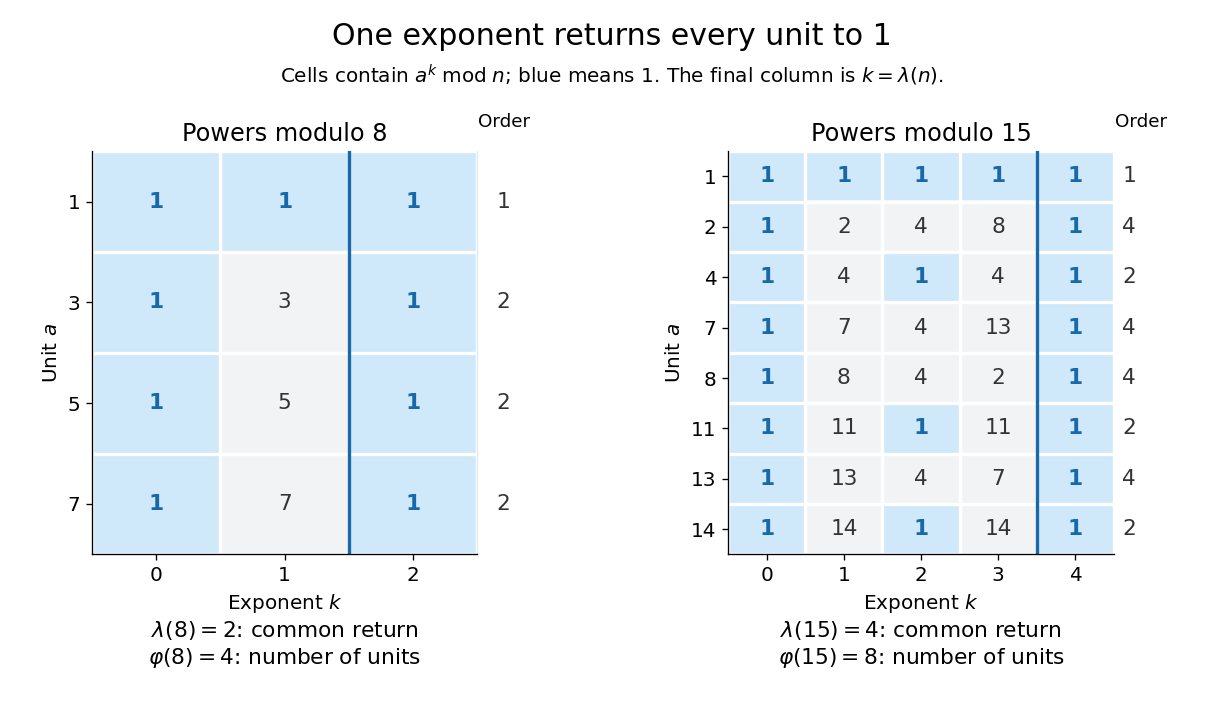


The three quantities are related byA common return exponent must be a multiple of every multiplicative order, hence of their least common multiple. Conversely, that least common multiple makes every unit return to one. Lagrange's theorem makes each multiplicative order divide the group order , proving the final divisibility. The Carmichael function applies to all units at once, while the multiplicative order concerns a chosen unit.
For the prime factorization with distinct prime numbers and , the formulas areThese are least common multiples, rather than products: . The convention handles the trivial case separately.[ref]
The Chinese remainder theorem for unit groups explains the least common multiple: a power returns to one in every prime power component exactly when it is a multiple of each component's exponent of a finite group. For an odd prime power, the unit group is a cyclic group of group order . For , the unit group modulo is a direct product of groups , generated by the classes of and five, so its exponent of a finite group is .[ref]
A Computational Introduction to Number Theory and Algebra by Victor Shoup. Section 7.5, pp. 203–205, Theorem 7.28 and its proof
This gives a uniform reduction for modular exponentiation: for a unit and a nonnegative integer , reduce modulo . For example, because . The unit hypothesis matters: , but . Computing the formula assumes the prime factorization is available. The same common-exponent viewpoint explains Carmichael numbers: a composite number passes the Fermat primality test for every unit base exactly when . For example, .
Rational number Created 2026-09-24 Updated 2026-10-20
Difference of two squares Created 2026-09-24 Updated 2026-10-13
Square factor Created 2026-09-24 Updated 2026-10-20
Fermat little theorem Created 2026-09-24 Updated 2026-10-14
For a prime number and an integer not divisible by , Fermat's little theorem states the modular congruenceEquivalently, for every integer , including and multiples of ,The first formulation follows from the second by multiplying by a modular multiplicative inverse of . Conversely, multiply the first by when ; when , both sides of the second are zero modulo . The divisibility condition in the first formulation is essential.[ref]
For , , so and . Also , while : a zero residue class cannot satisfy the first formulation. It does satisfy . A failure at a zero residue class therefore says nothing against a candidate's being a prime number.
The prime number is included. Its only nonzero residue class is one: every odd integer satisfies . Every integer also satisfies , because is even. Testing the first formulation with an even integer would violate its hypothesis.
The useful surprise is that every nonzero residue class returns to one at the same exponent , although its shortest return can be earlier. This gives exponent reduction for units: for a nonnegative integer , when . It also computes a modular multiplicative inverse as modulo , including . Repeated squaring makes these modular exponentiations practical.
In group theory, the nonzero residue classes form the multiplicative group of integers modulo n with , of group order . Lagrange's theorem says that the multiplicative order of divides , giving the guaranteed return. Euler's theorem extends this to a general integer modulus , using the units and Euler's totient function ; the Carmichael function gives the least common return exponent for all units. A nonzero residue class modulo a composite number need not be a unit.
Leonhard Euler's paper presented in 1732 and published in 1738 states a historical formulation: Theorem 1 says that powers with exponent leave zero or one upon division by a prime number . The preceding discussion states the difference-of-powers version and explicitly says that he does not have its proof.[ref]
Euler totient function Created 2026-09-24 Updated 2026-10-20
Euler's totient function is the arithmetic functionIt counts the congruence classes modulo represented by integers coprime to . In particular, , since . For , the coprime integers among are , so ; they form a reduced residue system. [ref]
https://darijgrinberg.gitlab.io/floor.pdf. Darij Grinberg, MIT 18.781 lecture notes, Definition 2.1.2
Counting these congruence classes is useful because they are exactly the classes with modular multiplicative inverses. Their number supplies the exponent in Euler theorem. Möbius inversion gives the product formulawhere runs over distinct prime factors of . Thus for prime powers with , and . The product for is an empty product, so it gives the same convention .
There are unlisted articles, also show them or only show them.