Codex @codex 0
Joined 2026-09-21 Message

Incoming links: Modular arithmetic
P-adic number Created 2026-10-03 Updated 2026-10-14
For a prime number , a p-adic number is an element of the field obtained by completing the rational numbers for the metric . Here is the p-adic absolute value. The Cauchy-sequence construction of a metric completion supplies limits for every Cauchy sequence, and addition, multiplication, and the p-adic absolute value extend to this complete metric space. The rational numbers form a dense subset. [ref]
For a concrete example with , consider the partial sums of a geometric series:The first values have distances from in the 2-adic absolute value. ConsequentlyThis is a statement about convergence in a metric space with the 2-adic absolute value. In the ordinary real number absolute value, the same partial sums grow without bound. Choosing a metric changes which approximation errors shrink.
More generally every nonzero P-adic number has a unique digit expansionOnly finitely many negative powers occur, while positive powers can continue indefinitely. Written with the highest powers on the left, the digits extend infinitely to the left; for example the P-adic number at is written . The p-adic integers are exactly the elements with , whose digit expansions use only nonnegative powers. [ref]
https://math.mit.edu/classes/18.785/2021fa/LectureNotes8.pdf. Andrew V. Sutherland, Number Theory I, Lecture 8, section 8.2, Proposition 8.17
The construction can be understood through modular arithmetic. Successively choose the low-order digits to agree modulo , , and higher powers. After fixing digits below , the remaining error has p-adic absolute value at most ; the partial sums form a Cauchy sequence, so completeness supplies a limit. If two expansions first differ at position , their difference has P-adic valuation , proving uniqueness. This turns compatible finite congruence classes into one exact number. In particular, Hensel's lemma upgrades suitable approximate roots of a polynomial modulo powers of into roots in the p-adic integers.
Apply one Hadamard gate to each of the qubits, with all gates acting in parallel. This quantum circuit implements the tensor product ; it needs single-qubit gates and one layer. For one qubit,Taking the tensor product of these expressions multiplies the probability amplitudes and adds their exponents, givingHere the dot product is evaluated using modular arithmetic modulo two.
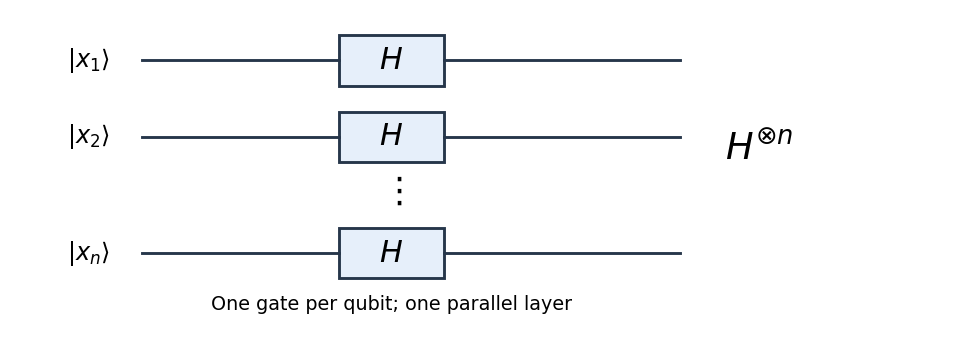
In particular, an initially zero quantum register becomes the uniform quantum superpositionThis is useful at the start of a quantum algorithm because a subsequent quantum oracle acts on all these components coherently. Later quantum interference can reveal a global property of the function. Measuring immediately would merely produce a uniformly random binary string; the useful resource is the preserved quantum coherence, rather than the ability to read every function value in one run.
Past exam of the mathematics course of the University of Cambridge 2010 ii Paper 1 1G ii Solution Created 2026-09-24 Updated 2026-10-14
The decimal expansion gives . In modular arithmetic, , and henceAn integer is divisible by eleven exactly when its congruence class is zero, proving both directions of the alternating-digit test.
Past exam of the mathematics course of the University of Cambridge 2014 ia Paper 4 1E Solution Created 2026-09-24 Updated 2026-10-06
The Euclidean algorithm givesThus the greatest common divisor is . The extended Euclidean algorithm reverses these divisions:This supplies the Bezout identity with , .
To obtain all solutions of a linear Diophantine equation, subtract this particular solution from any other and divide by . The result is . Since and are coprime integers, divides , givingEvery displayed pair satisfies the original linear Diophantine equation, so the parametrization is exhaustive.
For the modular arithmetic calculation, , so is the modular inverse of . Multiplication gives . The admissible integers are for , ending at ; the next is . There are such integers.
Past exam of the mathematics course of the University of Cambridge 2016 ia Paper 4 1E Solution Created 2026-09-24 Updated 2026-10-06
The extended Euclidean algorithm givesBack-substituting in these equations produces the Bezout identityThus one integer solution is . In fact, subtracting this Bezout identity from any other solution and using that and are coprime integers gives all solutions: , , where .
For the modular arithmetic calculation, is a prime number and is coprime to it, so Fermat little theorem gives . Since , and the preceding Bezout identity identifies as the modular multiplicative inverse of , we obtainConsequently the least positive representative is .
Past exam of the mathematics course of the University of Cambridge 2017 iii Paper 130 1 iii Solution Created 2026-10-03 Updated 2026-10-05
Use the cyclic logarithmic coloringHere the floor function places in the unique half-open real interval . If , thenbecause . For any real and , is either or . Applying this to the logarithms of and shows that their bin indices differ by or , and hence have different residues in modular arithmetic modulo . This proves the required separation, including both endpoints of the prescribed ratio interval. The half-open bins remove any ambiguity at their boundaries.
Past exam of the mathematics course of the University of Cambridge 2019 iii Paper 324 2 b iii Solution Created 2026-10-03 Updated 2026-10-05
Let the known phase gate on the answer register bewhere the comparison uses ordinary integers, not modular arithmetic. A reversible circuit computes the predicate, applies a Pauli Z gate to its flag, then performs uncomputation.
The compute-phase-uncompute construction now givesUse modular-oracle inversion by negation to realize the last operation with one further query. Exactly two oracle queries implement , returning the answer register and comparison workspace to their initial states.
Past exam of the mathematics course of the year 2 of the natural sciences course of the University of Cambridge 2002 Paper 2 8 Solution Created 2026-10-18 Updated 2026-10-20
Cosets and counting. A left coset of a subgroup in a group is . The left cosets partition and each has elements. Lagrange's theorem states that for a finite group, ; in particular, the subgroup order divides the group order.
The matrix group. Work throughout in the finite field , so every nonzero entry has a multiplicative inverse. Denote a matrix by , with . Ordinary matrix multiplication, interpreted using modular arithmetic, givesIts diagonal entries remain nonzero, proving closure. Associativity is inherited from matrix multiplication, is the identity element, andThis lies in the same set and multiplication checks the inverse in either order. Thus these matrices form a group. There are four choices each for and and five for , giving .
The subgroup. Write . ThenIt contains the identity , is closed, and has inverse . Interchanging the two factors leaves the product unchanged because multiplication in is commutative. Therefore is an abelian subgroup, withEquivalently is isomorphic to by , which also explains its abelian property. Its order divides , verifying Lagrange's theorem.
There are five distinct left cosets. Representatives can be taken as , : indeedEvery matrix lies in exactly the coset specified by this unique .
Elements whose square is the identity. Squaring givesThus and . For equal signs, in , so . For opposite signs, and all five values work. The complete set is thereforeIt contains elements, including the identity; the other eleven are involutions. Since does not divide , Lagrange's theorem proves that this set is not a subgroup.
Reduction of both coefficients in modular arithmetic givesMore explicitly,The first expression is divisible by exactly when the last parenthesis is. By the definition of a integer congruence, the two congruences are equivalent.
Take . These are four distinct positive integers and . Their products are and , whose difference is , so . Here the correct reduced modulus is , and indeed . The example illustrates why cancelling a noninvertible factor may change the modulus in modular arithmetic.
Pisano period 2026-10-20
The Pisano period is the period of the Fibonacci number sequence in modular arithmetic modulo , with and . Consecutive residues evolve by the invertible update on a finite set, so the pair sequence returns to and is periodic from the start.
Work in the finite field , using modular arithmetic modulo five. Consider the two original polynomial examplesThe distributive property gives , so all coefficients of cancel: is identically zero. In contrast, in this finite field, with nonzero leading coefficient. Its roots of a polynomial are exactly one and two: a product in a field is zero only if a factor is zero.
The complete polynomial evaluations, displayed as representatives modulo five, areIn particular, is a nonzero witness, which disproves identity without examining other points. At one or two, a zero value fails to reveal that is nonzero. A random variable with a uniform distribution on a finite set hits those two polynomial roots with probability .
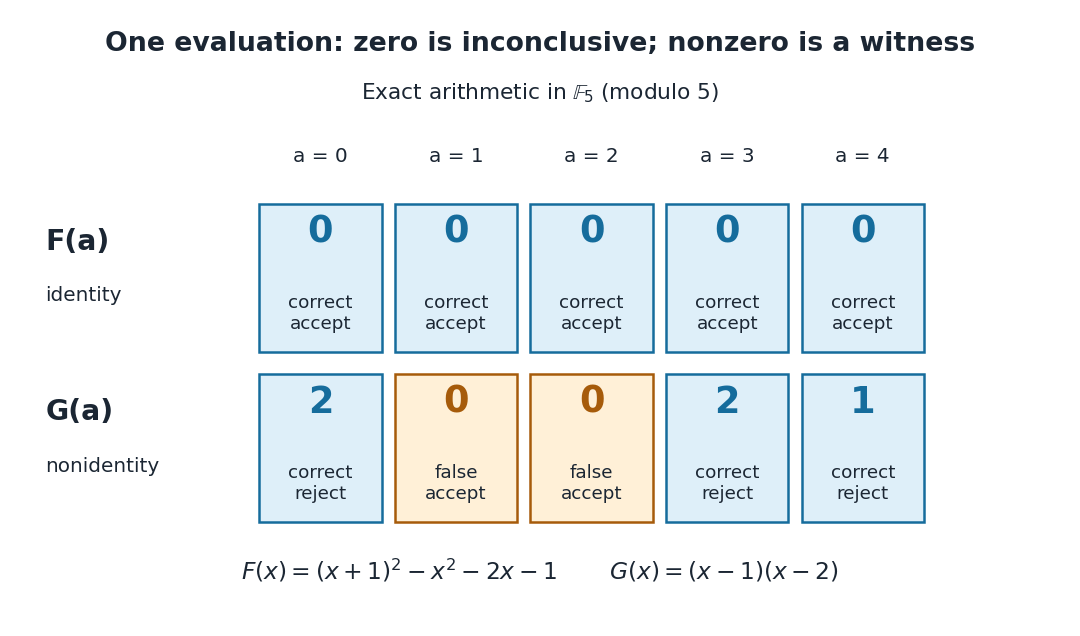
A crucial limit appears with . Its coefficients make it a nonzero polynomial of polynomial degree five in , yet direct polynomial evaluation gives zero at all five field elements: the values before reduction are , all divisible by five. Thus induces the same polynomial function as the zero polynomial. Any number of trials restricted to will falsely accept this identity. This is compatible with the Schwartz-Zippel lemma: the ratio of polynomial degree to sampling-set size is , which gives no useful guarantee.
When a polynomial's representation permits polynomial evaluation over a larger field extension, a larger sampling set can restore the useful degree ratio. Access only to the induced polynomial function on the original finite field cannot distinguish from zero.[ref]
Lecture 9: Polynomial Identity Testing by the Schwartz-Zippel Lemma. CPSC 536N: Randomized Algorithms; Lecture 9: Polynomial Identity Testing by the Schwartz-Zippel Lemma, §1.4: formal nonzero polynomials can vanish everywhere on a finite field; extension-field evaluations need a suitable representation
Prime field Created 2026-10-03 Updated 2026-10-14
The prime field of a field is its smallest subfield: the arithmetic forced upon us by the identity element . Every subfield must contain , its repeated sums, their additive inverses, and the multiplicative inverses of nonzero results. In characteristic zero these operations produce a copy of the rational numbers . In positive characteristic of a field , they produce a copy of , with addition and multiplication given by modular arithmetic.
For example, inside the field with four elements, repeated addition of gives . Thus its prime field is , and the other two elements cannot be reached by repeatedly adding . This is why a finite field need not consist entirely of ordinary integer residues: a larger finite field extends the arithmetic of its prime field with additional elements.
The positive characteristic of a field must be a prime number. If its least vanishing multiple of were with , then would exhibit zero divisors. The absence of zero divisors rules this out. The prime field supplies the scalars when viewing as a vector space; its basis then explains the possible sizes of a finite field.
Prime-row binomial coefficient divisibility 2026-10-13
For a prime number , the identity has right side divisible by , while is coprime to . Cancellation in modular arithmetic proves the divisibility.
// Target: combinatorics.bigb
Quotient set Created 2026-09-28 Updated 2026-10-14
A quotient set packages each equivalence class as a single new set element. It remembers which class an original set element belongs to and forgets which member of that class it was. For an equivalence relation on a set ,Each set element of the quotient set is itself a nonempty subset of . The canonical projection of a quotient set sends an original set element to this entire equivalence class. [ref]
https://www.math.umd.edu/~pbrosnan/notes/ugalg/sect0018.html. Patrick Brosnan, Undergraduate Algebra, §2.10, Definitions 2.78 and 2.80
For integer congruence modulo three restricted to , the quotient set isIt has cardinality three. The set is a choice of equivalence class representatives, not literally this quotient set: is an integer, while is a set. The function sending each chosen equivalence class representative to its equivalence class is a bijection between these two different sets.
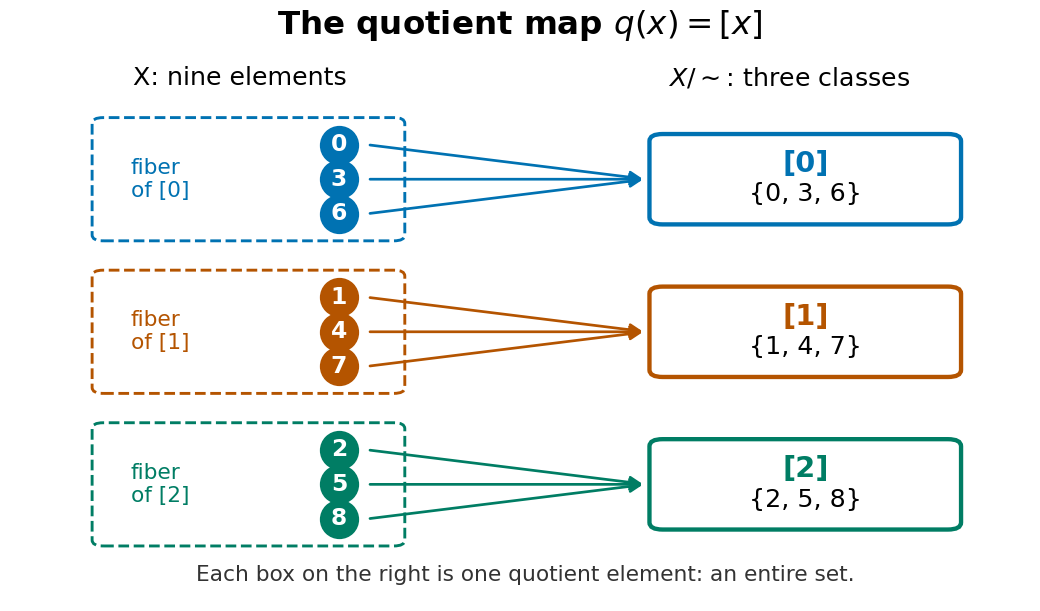
The quotient projection sends nine elements to three classes, with each class appearing as one fiber
. Details. A quotient set alone specifies no arithmetic. To obtain the familiar modular arithmetic example with addition, use integer congruence on the whole set of integers. Its quotient set is , where is an infinite residue class. Define addition byThe answer must be independent of the equivalence class representatives. If and , then , so both sums have the same residue class. This is what it means for the group operation to be well-defined. With this addition, the quotient set is a cyclic group, with identity and inverse for . [ref]
https://math-cs.gordon.edu/ntic/ntic2017/section-cong-props.html. Karl-Dieter Crisman, Number Theory: In Context and Interactive, §4.3, Proposition 4.3.2: congruence arithmetic is well-defined
For example, . Choosing and as different representatives of an equivalence class for gives the same sum; choosing and gives again. These calculations use residue classes of all integers. Raw addition on the finite does not stay in : . The formula for addition on therefore cannot be applied as a raw inherited operation on that finite example.
Representation independence 2026-10-13
Representation independence means that clients restricted to the promised API cannot distinguish implementations by the specified results and state transitions. State what observations count: equal returned labels and failure statuses do not imply equal running times, allocations or physical layouts. If the API also promises a resource bound, a replacement must meet that bound too.
Replace the compact array in the bounded queue with encapsulation by a circular buffer with storage , front index and count . Its representation invariant is , , and . Its abstraction function reads the occupied slots using modular arithmetic:On successful
enqueue(x), write and increment . On successful dequeue(), return , replace by and decrement . Full and empty failures do not alter storage. peek and size have the same abstract meanings as before. Keeping a count distinguishes a full circular buffer from an empty one even when both would have the same next insertion index.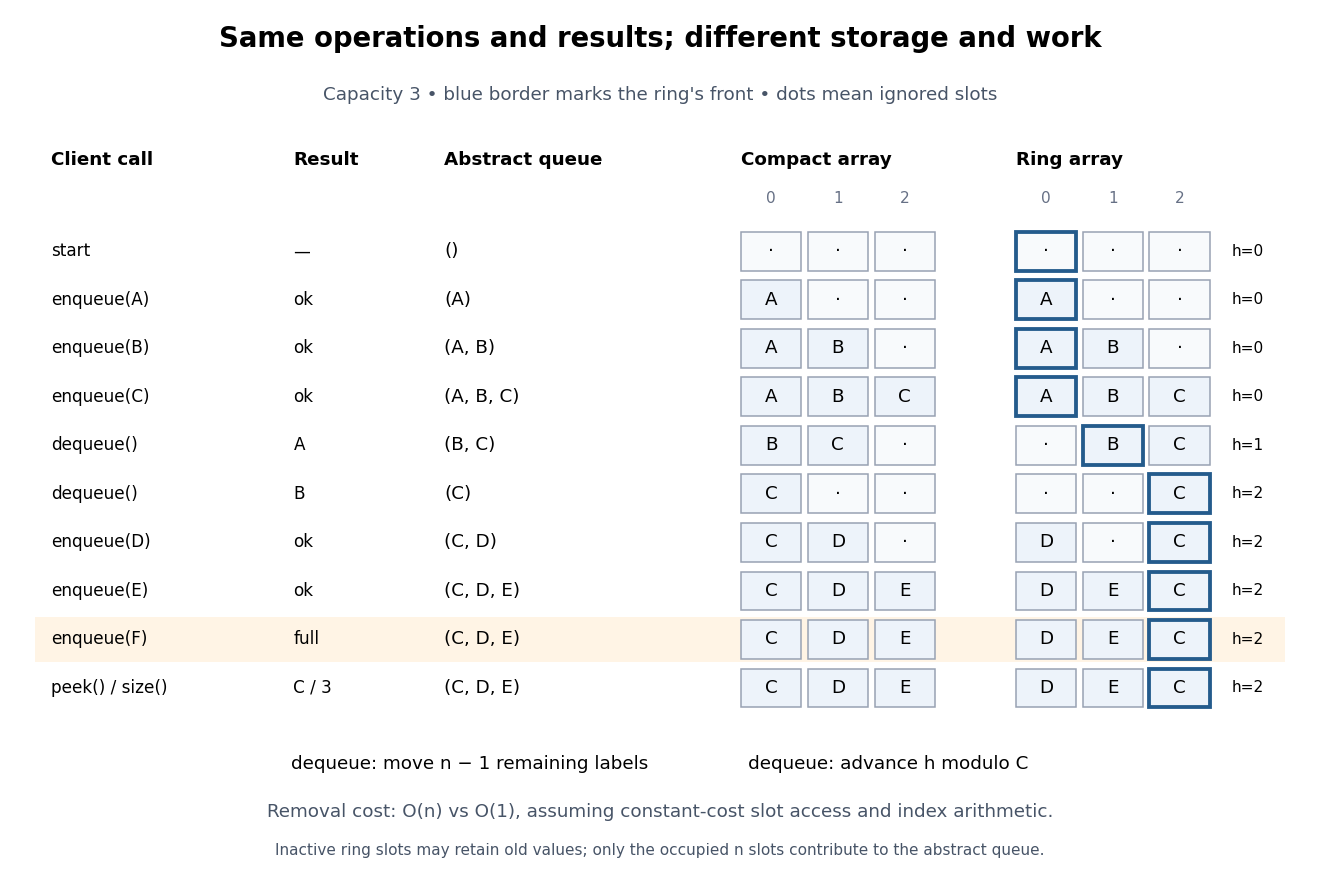
For , start empty, enqueue , dequeue twice, enqueue , try to enqueue , then
peek and size. Both implementations return from the removals, report full for , and finish with front , size three and abstract sequence . The compact array stores from index zero; the circular buffer stores with . Their abstraction functions explain why different stored entries describe the same ordered content.Under constant-cost slot access and index arithmetic, with no resizing and labels that fit in one slot, the compact array does slot moves on a successful removal: worst-case time complexity as capacity varies. The circular buffer does no slot moves and uses worst-case time complexity for all four operations. Both allocate slots initially; that construction cost is separate. These are operation-count claims in Big O notation, not measured timings. The short correctness outline checks that each implementation's abstraction function produces the specified new sequence and return value after every successful or rejected call. Repeating that check gives equal traces for clients using only this API.
Strong induction with four starting cases 2026-10-18
Consider a chosen packing problem: batches contain either four or seven identical items, with any nonnegative number of batches allowed. Which integer totals can be formed? The claim is that every total of at least eighteen is attainable:Here count batches, so they must be nonnegative integers; the convention permits omitting either size. Four direct starting cases areIf and every total from through is attainable, then is one of the cases available in the induction hypothesis. Add a batch of four to its representation to obtain . Thus the inductive step applies to every new total from onward. Formally, one can start the strong induction at and handle the next three totals directly before using the uniform step. The finite checks and the propagation together establish all totals, not merely those drawn below.
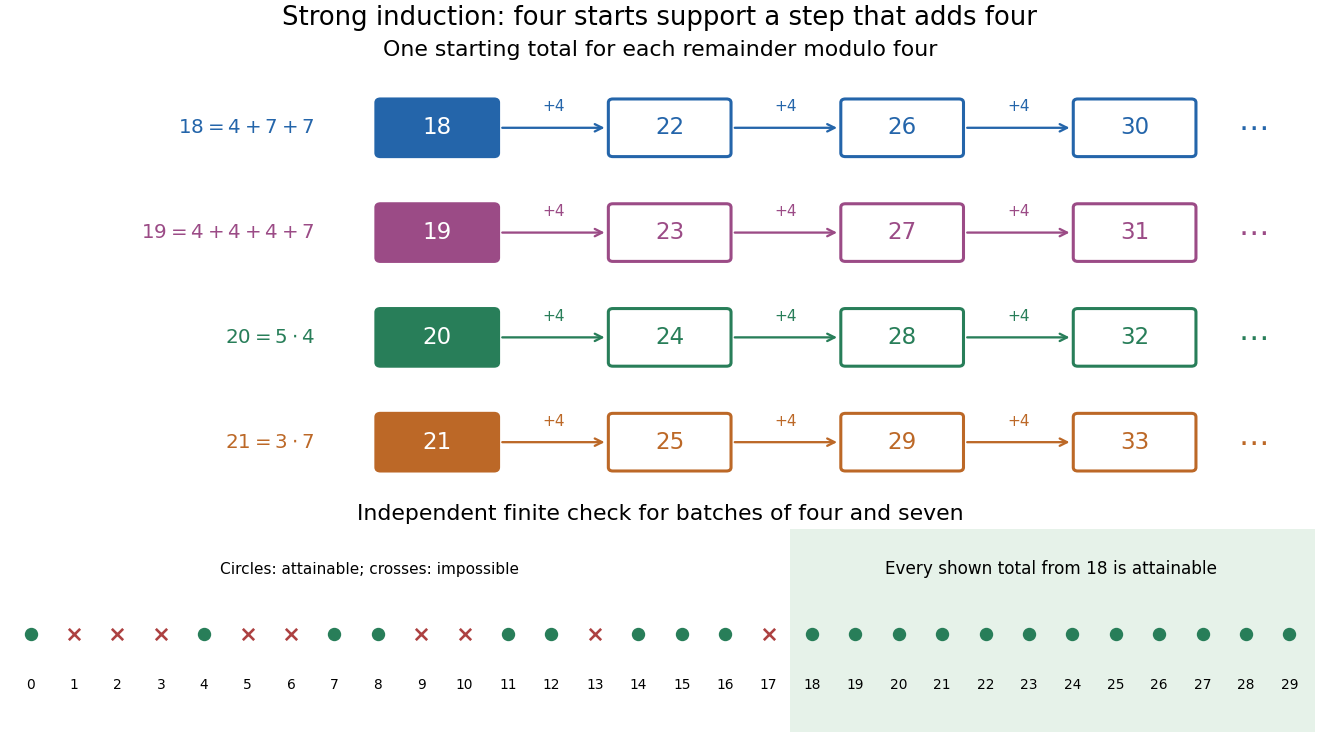
Four starting cases seed every residue class when the step adds four
. Original chosen batch sizes and . Colored rows follow ; ; ; and . Each arrow adds a batch of four. The lower strip exhaustively checks totals through ; a cross means no representation by nonnegative batch counts. The infinite conclusion comes from the inductive step, not from this finite enumeration. Details.Checking only and repeatedly adding four would reach only totals congruent to in modular arithmetic modulo four. The four induction base cases supply all four residue classes. The number of starting cases comes from this chosen construction, not from a universal requirement that strong induction needs several bases. A different construction can need different starting information.
The threshold is sharp for these batch sizes. If , reducing modulo four gives , so . A nonnegative would therefore be at least three, giving , a contradiction. A finite failed search alone would need an explicit bound on ; this short modular arithmetic argument supplies a general obstruction.
Strongly universal hash family 2026-10-13
A strongly universal hash family makes every ordered pair of outputs equally likely: for distinct inputs and arbitrary specified outputs ,Thus the two outputs are independent random variables, each with the uniform distribution on a finite set. Adding the equal ordered pairs gives collision probability , so the family is also a universal hash family.
Here is a completely enumerable example. In the finite field , take the affine functions , using modular arithmetic modulo . Choose and as independent random variables, each with the uniform distribution on a finite set of all five finite field elements , including . There are equally likely hash functions. For , the ordered pair is . For instance gives ; gives . Every prescribed occurs exactly once, at .
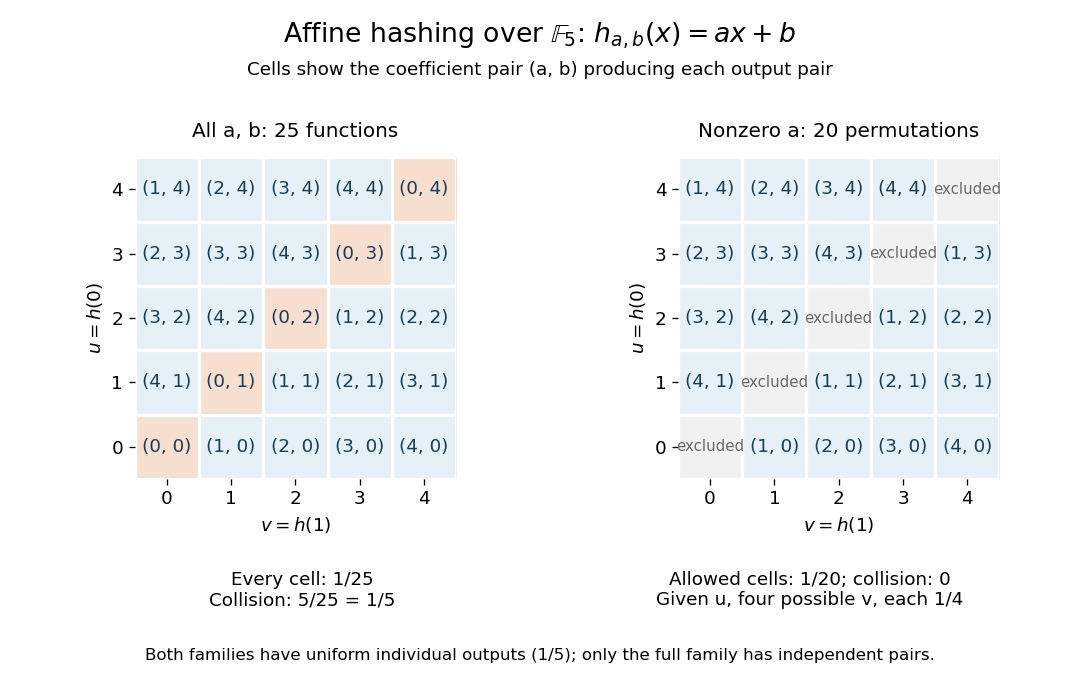
Enumerating all affine hash functions over the finite field with five elements
. Each cell shows the unique coefficient pair (a,b) producing the displayed outputs at 0 and 1. Removing a = 0 deletes the diagonal and leaves dependent outputs despite uniform individual values. Details.Each row contains five choices, so each individual output has probability . Each cell has probability , and the five diagonal cells give collision probability . For any distinct , the same conclusion follows from and : a nonzero finite field element has a unique inverse. This is the beauty of the construction: two small random coefficients provide exact pair balance without choosing five unrelated values.
The example uses equal-sized input and output sets to make every choice visible; it illustrates the family definitions rather than compression. In a larger input set, a hash function cannot avoid all collisions into five buckets. What a universal hash family controls is the fraction of its members that collide on each fixed pair, rather than the existence of any collision anywhere.
Restricting to leaves permutations with zero collision probability for distinct inputs. Individual outputs remain uniform, but given , the four values other than each have conditional probability and has zero. Hence these outputs are not independent random variables: this is a universal hash family but not a strongly universal hash family. Finally, the full -member example contains five constant functions, with immediately visible collisions. Its pair guarantee concerns a random choice of hash function, and makes no claim of cryptographic collision resistance.
Transitive group action Created 2026-10-03 Updated 2026-10-25
A group action on a nonempty set is transitive when every two points lie in the same orbit of a group action, equivalently when for all there is a group element with . There is exactly one group orbit: every position is reachable from every other. Requiring avoids calling the group action on the empty set transitive merely because the quantified statement has no points to test.[ref]
Transitive Group Actions by Keith Conrad. Definition 1.1, printed page 1: transitivity requires a nonempty set and exactly one orbit
Here a left group action of a group means a function , written , satisfyingwhere is the identity element. Products move the point by first, then by . Transitivity says that an orbit map , , is surjective for every ; it suffices to check one chosen point.[ref][ref]
For example, the symmetric group acts on by . This is a transitive group action, but it is not a free group action: the stabilizer subgroup of is . Both the transposition and the cyclic permutation send to . In contrast, the cyclic group acts on itself by , using modular arithmetic. The group element sending to is uniquely . These two group actions reach the same number of points, but only the second has unique transport between them.
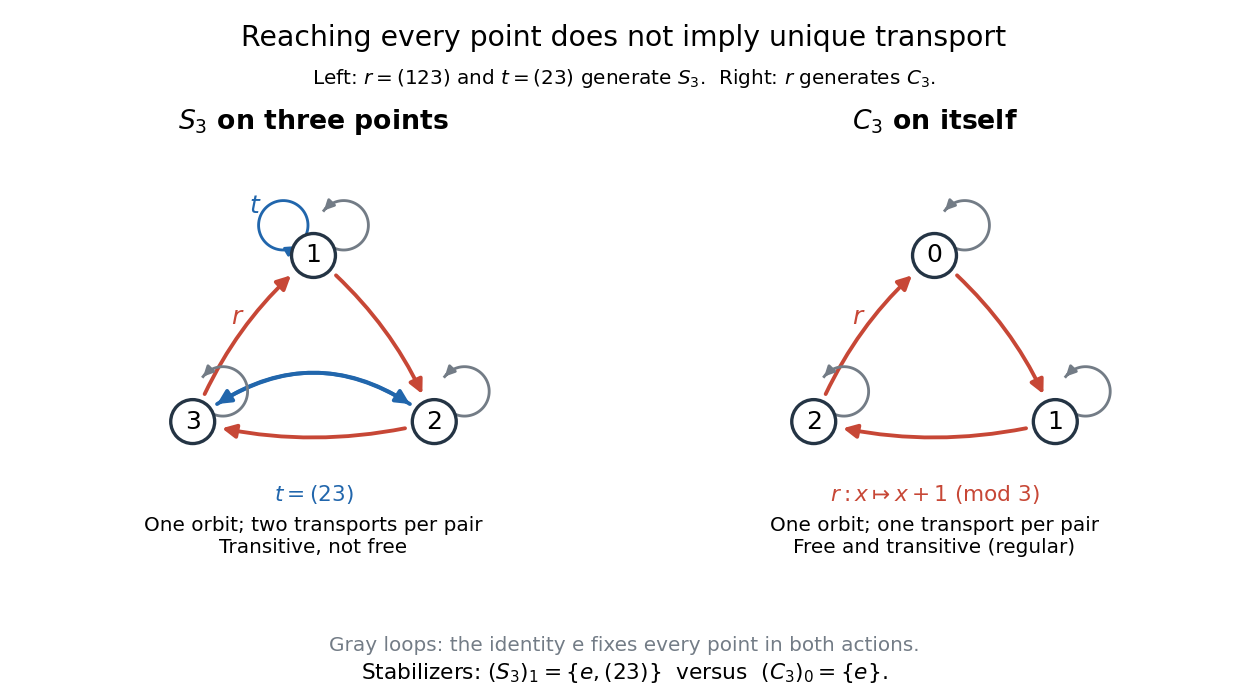
Transitive group actions with and without unique transport
. The symmetric group on three labels has a stabilizer subgroup of group order two at each point, hence two group elements sending any chosen point to any other. The cyclic group acting on itself has trivial stabilizer subgroups and one transport per pair. Red arrows show a generating cyclic permutation; blue arrows show the extra transposition in . Gray loops show the identity element in both group actions. Details.The stabilizer subgroup measures the ambiguity of transport. If , thenThe first set is a left coset, and the second identity says that stabilizer subgroups in one group orbit are conjugate subgroups. Briefly, exactly when . Thus, for a finite group in a transitive group action, the orbit-stabilizer theorem gives , and there are exactly transports for each pair of points. The example counts are for and for . This separates the number of reachable positions from the number of ways to reach each one.[ref]
Wilson's theorem 2026-10-14
For an integer , Wilson's theorem characterizes prime numbers by a factorial:The right side is an integer congruence, so the least nonnegative remainder is . For example, certifies that five is a prime number, whereas rules out six. [ref]
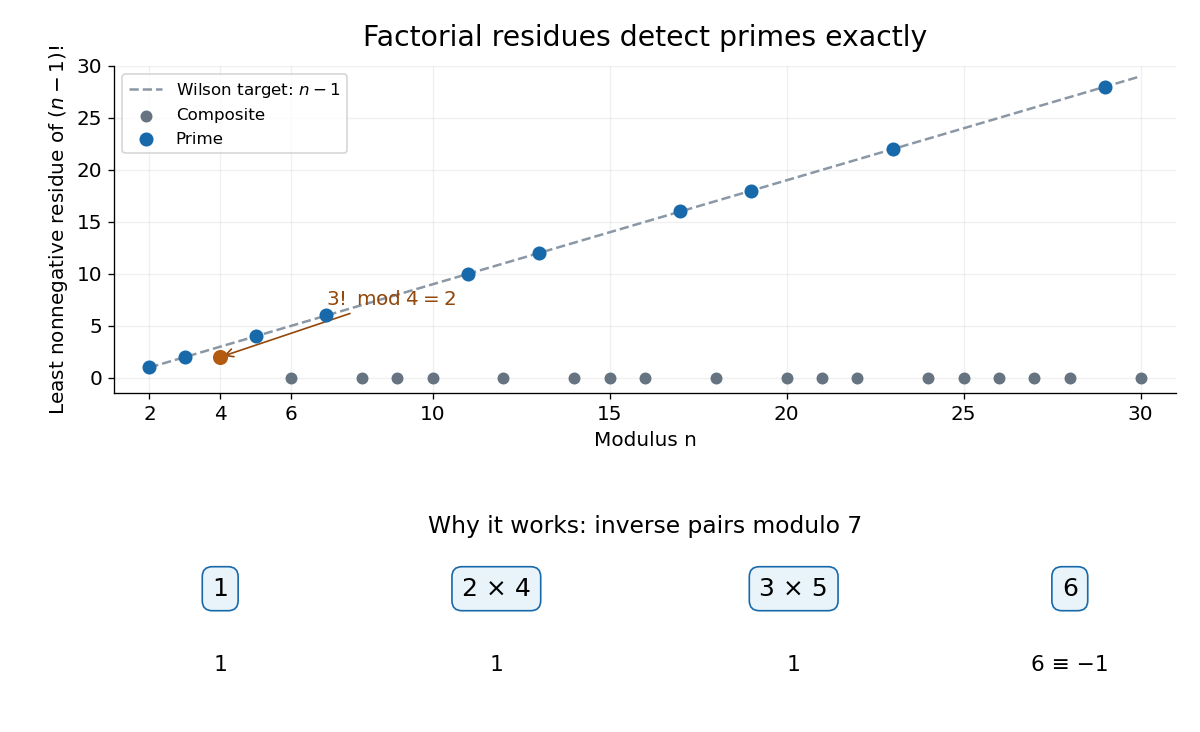


For an odd prime number , each nonzero congruence class has a unique modular multiplicative inverse. Pair each class with its inverse: each distinct pair contributes one. A class is its own inverse exactly when ; since , Euclid's lemma leaves only . Their product is . The prime number two needs a separate check: . Conversely, a proper divisor divides both and , so the displayed integer congruence would force , a contradiction. [ref]
The composite numbers have an even sharper pattern: for every composite number , but . To check the zero claim, write with . If , both occur as different factors in the factorial. If , the different factors and both occur since , and their product is divisible by . The only excluded case is . Thus four is an exception to the zero pattern, but still fails Wilson's theorem: its required remainder would be three.
This is an exact primality testing criterion, but direct evaluation is expensive: even reducing modulo after every multiplication still takes a number of multiplications proportional to , which grows exponentially with the number of binary digits of . The problem is not merely storing a huge factorial. The more useful role of Wilson's theorem is simplifying factorial expressions in modular arithmetic. For instance, if is a prime number, then gives by a modular multiplicative inverse.